A sophisticated phishing campaign dubbed “Operation CloudFire” has emerged, exploiting calendar invites and reverse proxies to hijack live Google sessions among corporate users since mid-August 2026. This operation bypassed defenses that usually rely on domain reputation, static link checks, and machine learning-based filters, by leveraging legitimate infrastructure and compromised trust relationships.
How the Attack Works
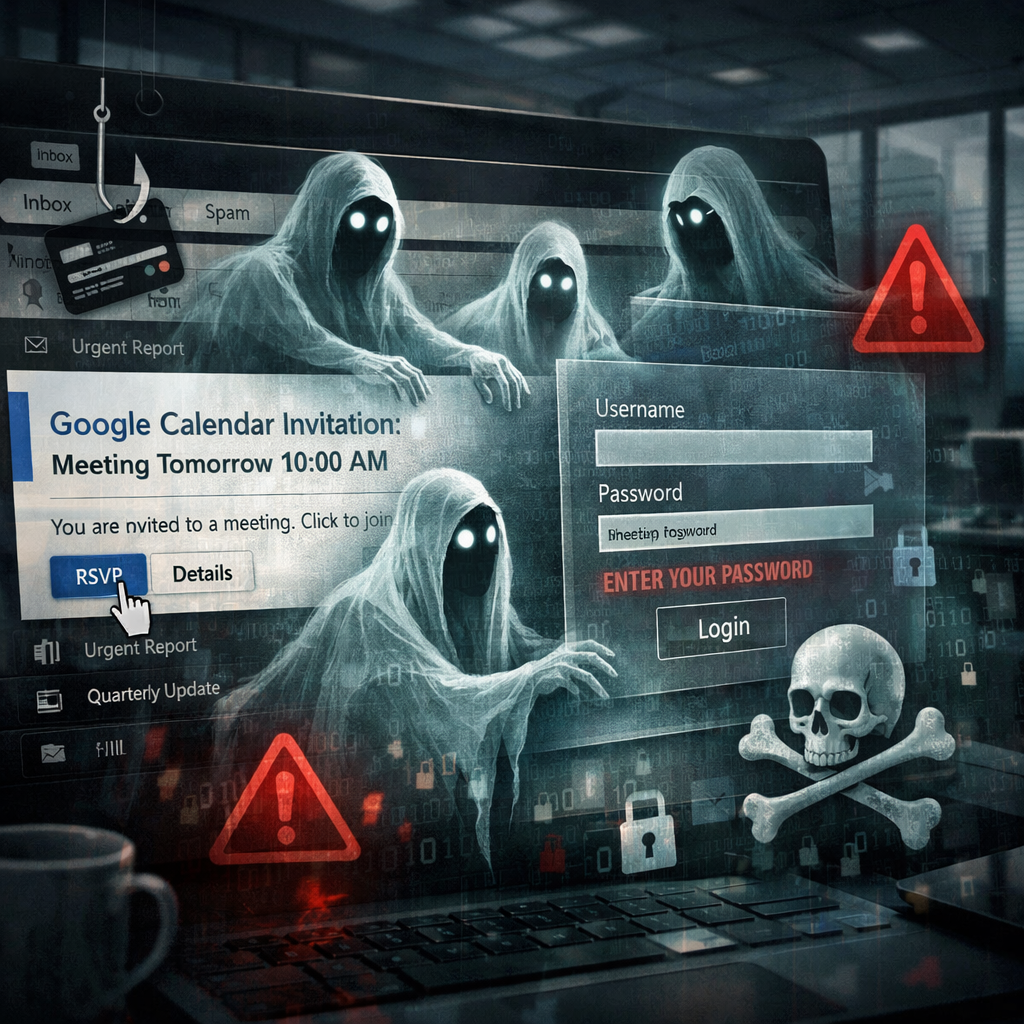
The attackers send out what appear to be Google Calendar invites, often using BCC so multiple targets are included, and seemingly from organizations the recipients have previously interacted with. The lures are mundane and unthreatening—voicemail notifications, missed payments, RFPs or legal summons—to avoid standing out in a crowded inbox. Key links appear to point at Google services via Google redirects, shareable files, or well-known brands such as Intuit; reputational and certificate checks on these domains pass with flying colors.
Clicking the link leads to a live, real-time reverse proxy sitting between the victim and Google’s genuine sign-in page. The victim enters credentials and any second-factor authentication, whether via SMS, authenticator app, or device interaction—all relayed through the proxy while the attackers observe. Essentially, no form of multifactor authentication can stop session capture once the proxy is in place.
Why Detection Was Evading Security Controls
Multiple layers of obfuscation shielded this campaign from standard defenses. First, emails start with a Google redirector, giving an impression of legitimacy. A Cloudflare Turnstile challenge is often incorporated to add a familiar protective barrier—sometimes using Cloudflare’s genuine infrastructure. The final credential-harvesting page is dynamically built via JavaScript in the browser, which means URL scanners, passive proxies, and automated crawlers generally cannot see or flag the malicious content ahead of time.
Also key: the domains used are mostly freshly registered, sometimes just hours ahead of use. Certificates are obtained swiftly, and domains are kept short-lived. This infrastructure paralysis makes blocking harder, as each element is cheap and disposable. Early versions registered domains just before sending invites; one wildcard certificate was even issued before its domain was officially registered.
Scale, Impact, and What Took It Down
Over a single month, participating organizations recorded more than 68,000 malicious messages blocked, analyzed over 2,100 malicious URLs, and saw nearly 900 domains taken down. Attackers also compromised thousands of individual sender accounts. Activity peaked during U.S. business hours, enhancing its plausibility. Attackers leveraged the compromised accounts to send invites using recognizable names and contact lists within legitimate root domains.
Damage from a hijacked session can be extensive. Beyond mailbox access, attackers can exploit Google Workspace audit logs, escalate privileges, grant OAuth tokens, and use the account for further compromise—all without immediate detection in many organizations. The campaign eventually shifted some focus from calendar invites toward shared Google Drive documents and file-share invites.
Researchers disrupted the infrastructure underlying CloudFire by reporting malicious endpoints to Cloudflare. Abuse reports triggered warnings being displayed to users who clicked dangerous links—effectively preempting credential prompts. While detection techniques helped block over 99% of the messages, only a layered approach—considering message origin, sending relationship, intent, and domain endpoints—proved robust.
At time of reporting, the campaign has quieted. But signs indicate attackers may be preparing to pivot, possibly targeting Microsoft 365 environments. A M365 branch was found in lightweight form—pointing to potential future expansion once ready.
The full technical breakdown, indicators of compromise, and timeline have been shared in a detailed whitepaper for security teams hunting similar threats.
Why This Matters
This campaign spotlights how attackers are outpacing conventional defenses. Even with strong reputation systems and multifactor protection in place, a determined adversary using live proxies and carefully crafted lures can still breach session security. Organizations must elevate their threat detection strategies—treating calendar invites as risky, tracking sending relationships, and deploying layered detection that analyses intent, context, and infrastructure together. The speed and scale of this attack also show that prevention alone won’t do—it must be paired with rapid response, network visibility, and preparedness for pivots to keep up with evolving strategies.