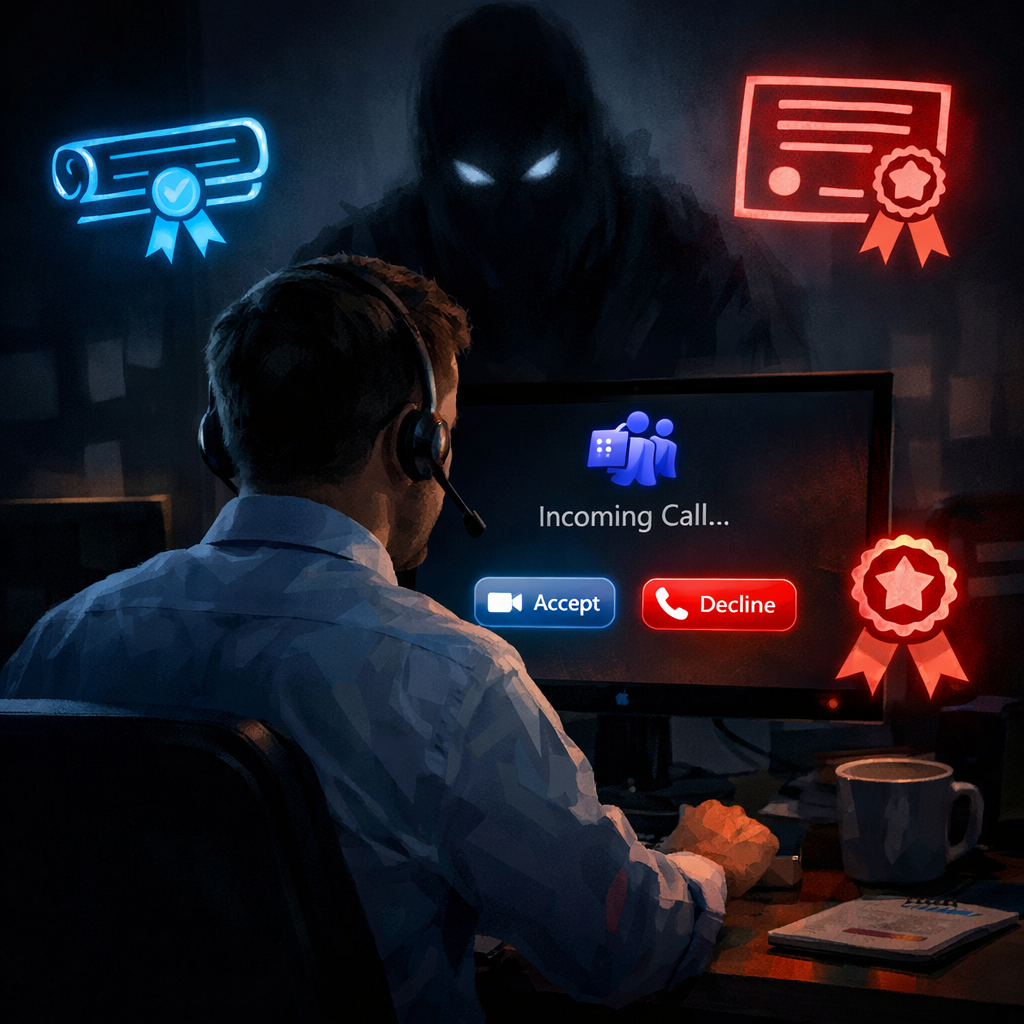
Security teams have uncovered a new scheme in which cybercriminals leverage Microsoft Teams messages and calls to impersonate internal IT support, convincing employees to give them remote access—and eventually abusing enterprise digital certificate systems.
How the Deception Unfolds
The attacks begin when threat actors create accounts with display names mimicking help desk staff and use tenant names resembling those of the target organization, making them look “trusted” at a glance. They initiate Teams chats or calls and pressure employees to approve remote-support sessions using legitimate tools like Microsoft Quick Assist. Once granted, that access becomes the gateway for deeper intrusion.
After control is gained, attackers drop an archive in the Downloads folder, set up a staged “update” directory in the user’s profile, and extract files. These include portable runtimes such as Python, Bun, or Java that enable execution of attacker-controlled code. One executable still had metadata identifying it as “Bun,” highlighting the limits of trusting file names alone. The compromised system is then probed—for information about network status, running processes, and Windows configurations—before reaching into sensitive domain infrastructure.
Abuse of Certificates, Data Theft & Red Team Warnings
In two separate incidents investigated in late October 2026, attackers abused misconfigured certificate templates within Active Directory Certificate Services (AD CS). In one case, an ESC1-vulnerable template allowed low-privileged users to supply another identity, resulting in certificates for highly privileged accounts. Attackers compromised workstations, issued certificates for multiple privileged users, and detected SMB file access, then began using DCSync to extract account and directory information. Files (some up to three years old) were later exfiltrated using an SFTP server.
The second incident used ESC8 and the PetitPotam NTLM relay to force a domain controller to authenticate to an attacker-controlled system. From there, attackers obtained a domain-controller certificate and used certificate-based Kerberos authentication to get a ticket-granting ticket—essentially giving them the keys to the domain. Though alerts triggered defensive actions, one privileged identity was left uncontained, allowing the attacker to reach further into critical assets.
Defensive Measures & Indicators to Watch
Key indicators include malformed remote access requests, suspicious external calls on Teams labeled “Scam suspected” or “External,” unusual certificate issuance, and Kerberos event anomalies. In the first intrusion, indicators of compromise (IoCs) included SHA-256 hashes for malicious JavaScript and Python scripts used for initial access.
To guard against similar attacks, Microsoft recommends the following steps:
- Verify support requests using pre-established channels before granting remote access.
- Restrict external Teams access and limit unapproved remote tools.
- Audit AD CS settings—especially certificate templates with weak permissions—and enforce HTTPS and extended authentication protections on enrollment endpoints.
- Revoke certificates that weren’t authorized and track Kerberos ticket issuance carefully.
- Check for privileged identities excluded from containment—just one unblocked account can sustain access.
On a broader level, combining collaboration logs with remote-session data, process activity, certificate issuance and authentication logs gives defenders better visibility into attack paths.
This alert serves as a reminder that even trusted platforms like Teams and remote-support tools can be weaponized when policies, certificate management, and employee vigilance fall short.
Why It Matters: These incidents illustrate that cyber attackers are no longer relying only on vulnerabilities in software—they’re exploiting social engineering, misconfigurations, and trust. Until organizations treat support tools, certificates, and identity systems as attack surfaces, they’ll continue to be blindsided. Experts should consider this a benchmark: verify every remote support request, harden certificate authority setups, and build incident response systems that can connect the dots between Teams chats, certificate issuance, and authentication abuse to stop attacks before damage mounts.