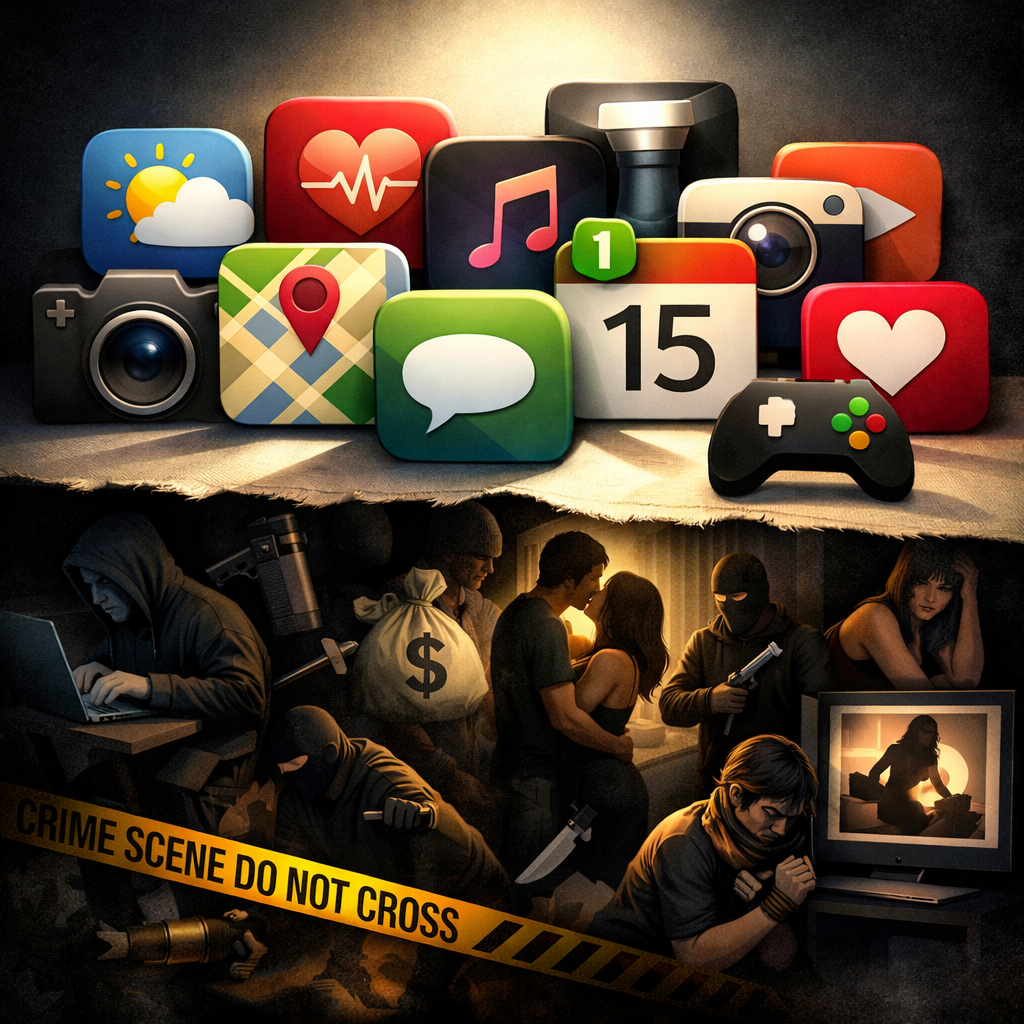
A recent probe uncovered over 400 AI-powered apps in Apple’s App Store—and Google Play—featuring deeply disturbing hidden capabilities. What seemed like run-of-the-mill utilities—like pet-photo editors, language tutors, or fitness assistants—harbored secret features enabling users to generate violent or sexual deepfake content using uploaded images.
How innocuous apps mask abusive features
The operation appears orchestrated by a single Chinese organization running more than 400 interconnected apps and domains. On the surface, these apps behave normally. But once certain conditions are met—often triggered by tapping an ad—hidden web interfaces activate that enable explicit sexual or violent deepfake generation. Some content options include “bedroom rape” scenarios or “threatening knife” scenes, where a figure holds a weapon to another person.
These apps routinely passed Apple and Google’s review processes, as well as Meta’s ad guidelines, by showing benign versions of themselves under review. It wasn’t until after installation or ad engagement that they loaded servers with the abusive content. Designers also uploaded thousands of video ads promoting these features on platforms like Facebook and Instagram, despite policies forbidding such content.
Platform responses: enforcement and limits
After being alerted, Apple removed 19 of the offending apps. Their explanation: these apps had complied with the rules during review, but later redirected the approved content source to pornographic or violent deepfake material—effectively bait-and-switch behavior.
Meta of course took sweeping action as well, disabling over 10,000 advertising accounts tied to domains connected with the abusive network. Apple claims to have strengthened protections to guard against this tactic in future.
This issue highlights serious gaps in how app stores and ad networks enforce policies around deepfake and explicit content. Review systems are being circumvented by developers hiding disallowed behavior until after approval—often via remote content changes or server redirects. The ad ecosystem is also complicit: promotional content that violates policy is used to draw users into installing the apps.
Even though some apps were swiftly taken down and accounts suspended, many remain available, potentially exposing users to non-consensual or otherwise harmful content without their knowledge. Platforms are under pressure to move faster and smarter in identifying deceptive behavior.
What this means and where we go from here: Deepfake technology already poses complex ethical and legal challenges. When developers hide sexual or violent content behind innocent facades, it turns these tools into instruments of abuse. App marketplaces must evolve beyond static review systems—adopting dynamic monitoring, better ad audits, and transparent developer accountability. For users, vigilance is essential. Always check which permissions apps request and what ads they show—not just what’s promoted on the store listing.