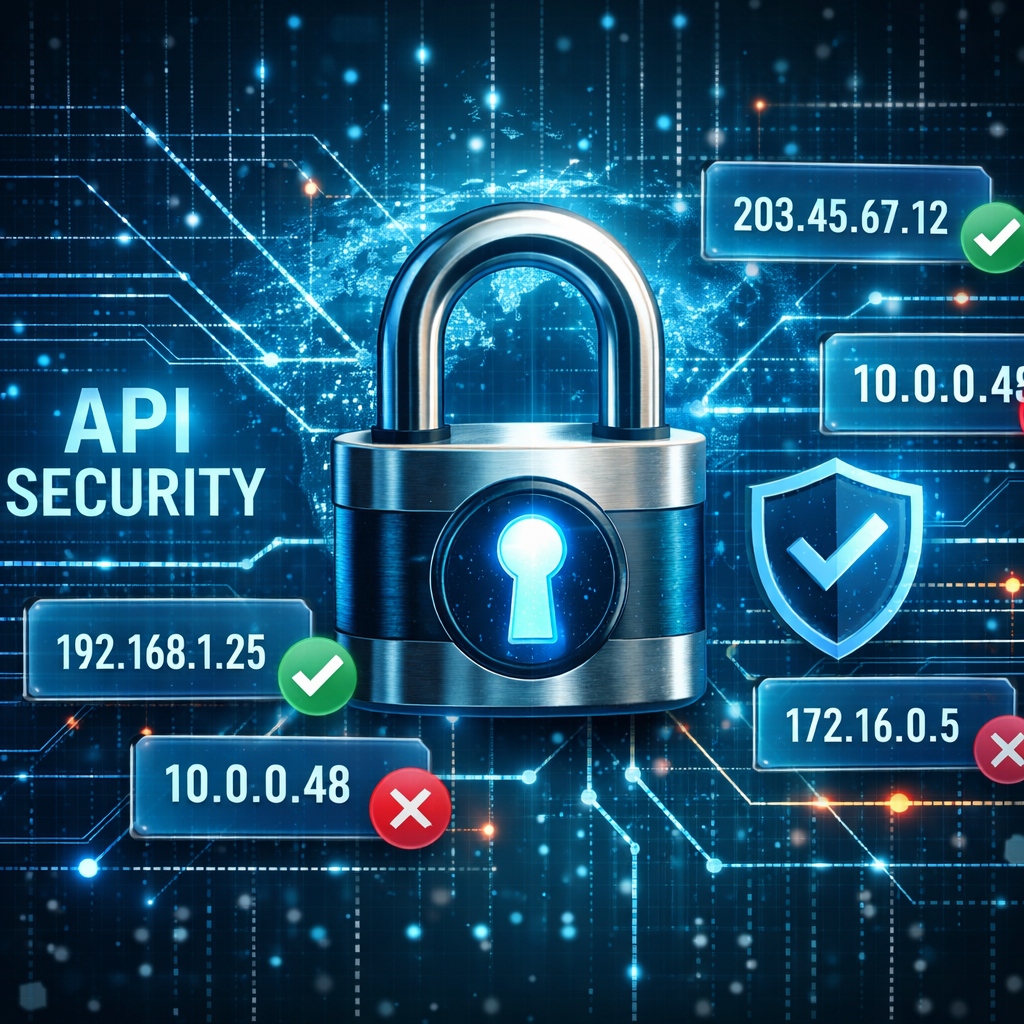
Shopify is compelling public app developers to enable IP allowlisting for any use of its Admin API, stepping up its safeguards against misused API tokens. The policy takes effect for most apps on November 20, 2026, with those making heavy use of bulk operations needing to comply even earlier—by November 12, 2026. Meantime, requests outside the authorized IP ranges will receive HTTP 403 rejections once enforcement is live.
This change transforms IP allowlisting—initially introduced as optional on October 27—into a hard requirement. The system now validates not only the token included in Admin API requests, but also the source IP, tightening protections around stolen or compromised credentials. Submissions from unapproved IPs or networks are blocked, and any request whose origin can’t be confidently determined is likewise rejected.
Deadlines, Consequences, and Transition Paths
Developers who don’t meet the November 20 deadline risk having their apps removed from Shopify’s App Store and barred from new installs. Existing instances will still work until April 1, 2027, after which Admin API calls will fail outright. Apps leveraging bulk queries and mutations have a stricter deadline, November 12, because of their increased risk surface. Starting January 15, merchants will begin seeing admin dashboard alerts if apps are not yet compliant.
Tasks like configuring IP allowlisting are handled via the Dev Dashboard’s Settings. Developers can allowlist specific IPs or ranges for static infrastructure. For apps hosted on platforms with dynamic IPs, Shopify supports allowing entire hosting networks through their autonomous system numbers (ASNs). Up to 10 ASNs may be authorized per app, and developers also have the option to restrict access by country—up to 10 in total. The system requires choosing either address-based or network-based rules; each replaces the other once saved.
Testing is part of the rollout process. Before enforcement starts, developers are urged to confirm that valid traffic continues being accepted, and that requests from outside allowed sources are indeed rejected. The official Shopify update referencing these changes includes slight date inconsistencies: while the detailed bulk-operations section lists November 12, a summary version shows November 11.
In parallel, Shopify is also pushing public apps to switch to expiring offline tokens by January 1, 2027. This adds token lifespans as another hedge against misuse, aligning with the enhanced network restrictions.
The move is clearly meant to reduce risk from token theft and misuse, illustrated by recent incidents where attackers leveraged unrotated API tokens. While IP allowlisting isn’t a cure-all—an attacker operating from an approved network could still act suspiciously—it significantly raises the bar for unauthorized API access.
Why It Matters & What to Watch: Shopify’s enforcement of IP allowlisting is part of a broader push to secure cloud-based APIs against stolen credentials. Developers must audit their hosting setups, ASNs, and network footprints immediately to ensure compliance—especially those with variable or cloud-based infrastructure. Expect merchant awareness to rise after the January warnings, and for token management practices to come under greater scrutiny throughout 2027. Security posture here could become a differentiator in trust and app store visibility.