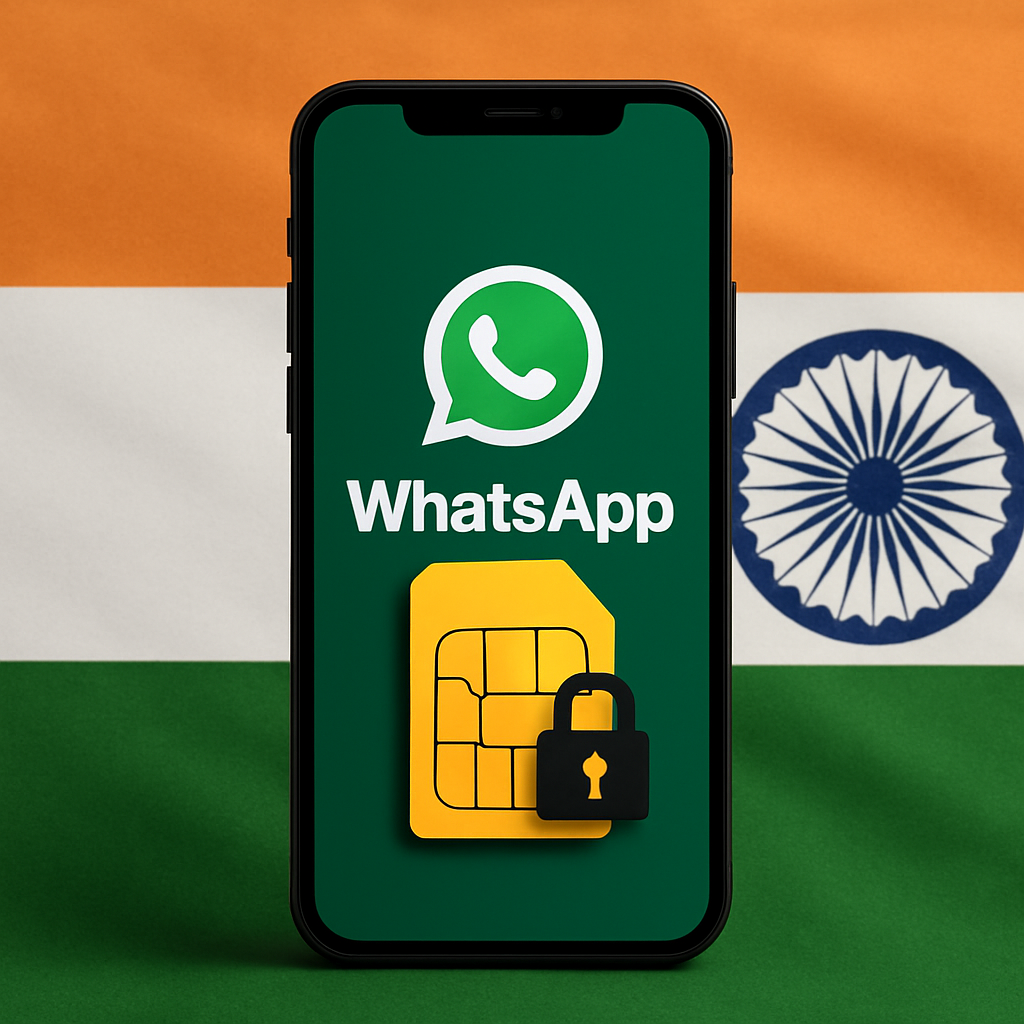
Starting January 1, 2027, WhatsApp users in India may be required to have their messaging account tethered to an active registered SIM card, under impending government regulations. These changes stem from mandates set out by the Department of Telecommunications (DoT), aligned with the Telecom Cyber Security Rules, 2024 as amended, aimed at tightening security measures across major messaging platforms. All eligible services—WhatsApp among them—must comply by December 31, 2026. Without adherence, users who access their accounts from secondary devices like tablets or phones without a registered SIM could be blocked from using the service.
What SIM-Binding Means for Users
The modulated requirement—called “SIM-binding”—forces an ongoing link between a messaging account and the SIM tied to its registered mobile number. Unlike standard verification codes used just during setup, SIM-binding necessitates that the registered SIM remain active on the device. The directive is intended to prevent misuse of inactive or deactivated SIMs that are still linked to messaging accounts, a loophole allegedly exploited for fraud, phishing, and false impersonation.
The regulation came into effect from rules notified on November 28, 2025, under the amended Telecom Cyber Security Rules. Affected platforms include WhatsApp, Telegram, Signal, Snapchat, ShareChat, Josh, JioChat, and Arattai. These services will need to ensure that accounts aren’t accessible without the presence of the registered SIM, especially to combat misuse of Indian numbers from outside the country. The government reported cyber-fraud losses surpassed ₹22,800 crore in 2024, underscoring the need for greater accountability and traceability.
Expected Disruptions & Device Compatibility
The rules also address linked devices—tablets, companion phones, or other secondary hardware—though how each platform implements restrictions will influence how service is impacted. Devices still tied to the registered SIM may continue to function while roaming is unaffected. Users who deactivate, switch, or remove their SIM cards, especially while traveling, may face sudden logout or access denial depending on behavioural triggers built into the app. Previously, all web sessions were required to terminate every six hours; this blanket rule has since been supplanted by risk-based logout triggers.
The policy aims not just to prevent number misuse but also to make accounts easier to trace, especially in fraud cases involving outside attackers. Nonetheless, the government cautions that SIM-binding does not guarantee immunity from all forms of account compromise, such as attacks targeting linked devices. Users are urged to monitor their Linked Devices settings and remove any sessions that look suspicious.
While January 1, 2027 is the target date for rollout, enforcement may be uneven depending on each platform’s readiness and implementation details. Not all users will necessarily notice disruption immediately—final policies may vary in how strictly secondary device access, logged-in WITHOUT the registered SIM, is curtailed.
What this means: The SIM-binding requirement transforms how messaging services authenticate and maintain accounts. For users, especially those relying on WhatsApp on tablets, secondary phones, or without having a SIM physically in the device, this disrupts familiar workflows. Technically, it may protect against certain fraud vectors—even those using inactive numbers—but it places more control in the SIM operator’s realm. Users will need to stay alert to updates from their platform of choice, and regularly audit linked sessions to avoid being caught off guard.