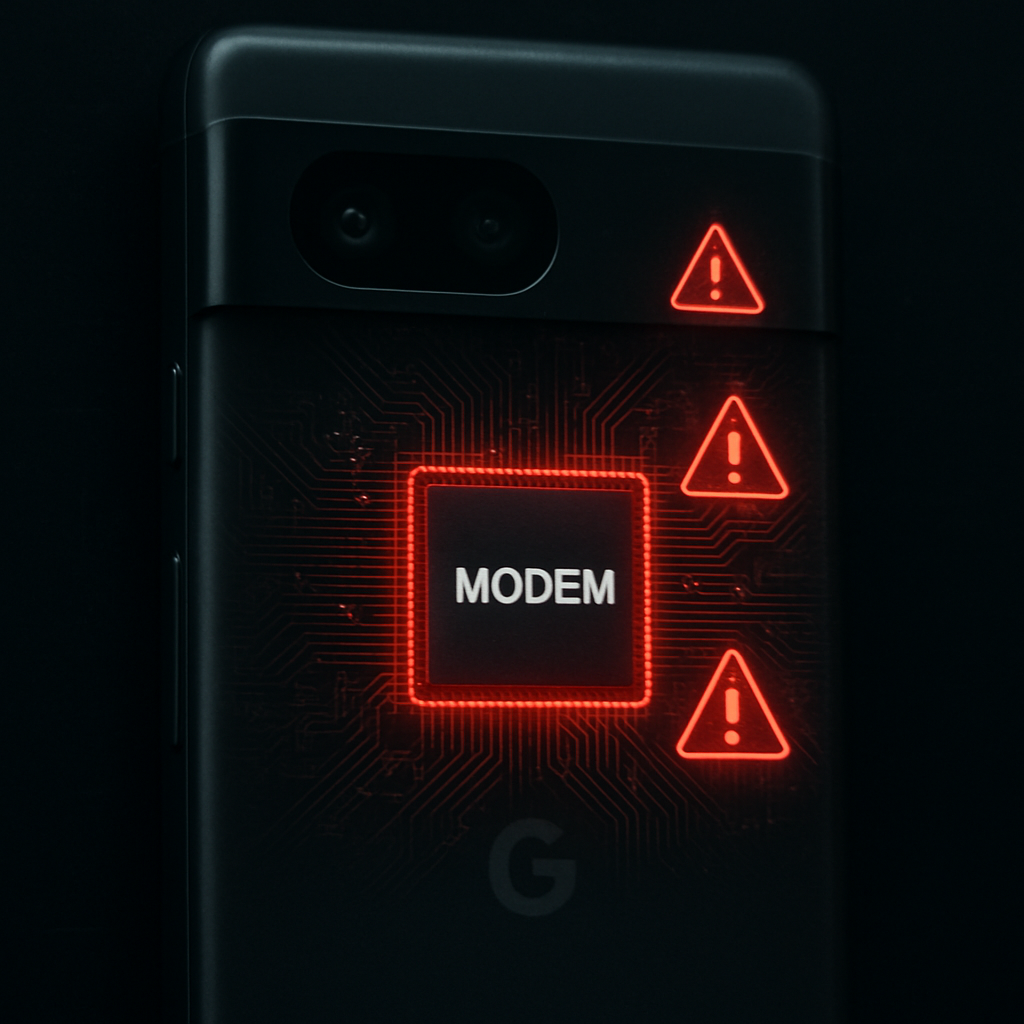
Google has disclosed that a small number of Pixel phones were compromised in a **targeted “zero-day” attack** exploiting a serious bug in the device modem. This vulnerability, identified as CVE-2026-58704, was patched in the September 2026 security update released by the company. The exploit allowed attackers to bypass permissions without any user interaction.
The flaw exists in the cellular modem’s logic: a permission bypass due to coding error could let nearby or adjacent attackers escalate privileges remotely. Since no additional execution permissions or user involvement are required, the risk is elevated—even more so because one or more of the affected devices have been exploited “in the wild.”
Details of the Exploit and Impacted Devices
Google’s security bulletin reveals that the modem vulnerability has been designated as a “known exploited vulnerability” by U.S. authorities. It specifically impacts Pixel phones, though the exact models haven’t been disclosed. The attack in question appears to be narrow in scope—aimed at specific targets, not broadly distributed.
Also notable: there is still uncertainty over how widespread the compromise is. The company has not confirmed which Pixel devices are vulnerable, and public details about how the exploit was carried out are sparse. Cybersecurity agency CISA has underlined that this type of weakness—permission bypass without user interaction—is frequently abused by malicious actors.
Fix and What Users Should Do
The good news for Pixel users is that the September 2026 patch already includes a fix for this problem. Google is rolling out the update immediately, recognizing the severity of the bug and its active exploitation.
If you own a Pixel phone, installing the latest security update is strongly recommended. Even if your device hasn’t shown any signs of compromise, delaying the patch could leave you exposed. Given that the exploit requires no action on your part, updating is the most effective defense.
Zero-click exploits like this represent one of the most dangerous class of vulnerabilities, because they do not require social engineering, phishing, or mistakes by users. In this case, the exploit works via the modem’s logic, a critical component for cellular communication that’s often a weak point for attacks.
This revelation follows recent concerns over how modems and sensors embedded in phones are increasingly becoming targets. It’s part of a broader pattern where attackers look to components once thought too embedded or specialized to be easily manipulated.
What it means:This breach highlights a growing trend in mobile security. When vulnerabilities in low-level hardware like modems are exploited without user interaction, the stakes are high—not just for individual users, but for enterprises and public institutions. Moving forward, expect demand for better transparency from device makers about exploits behind such flaws, and more rapid disclosure of which models are affected. Users should keep devices up to date, and companies should conduct rigorous audits of low-level firmware and modem logic to prevent similar incidents.