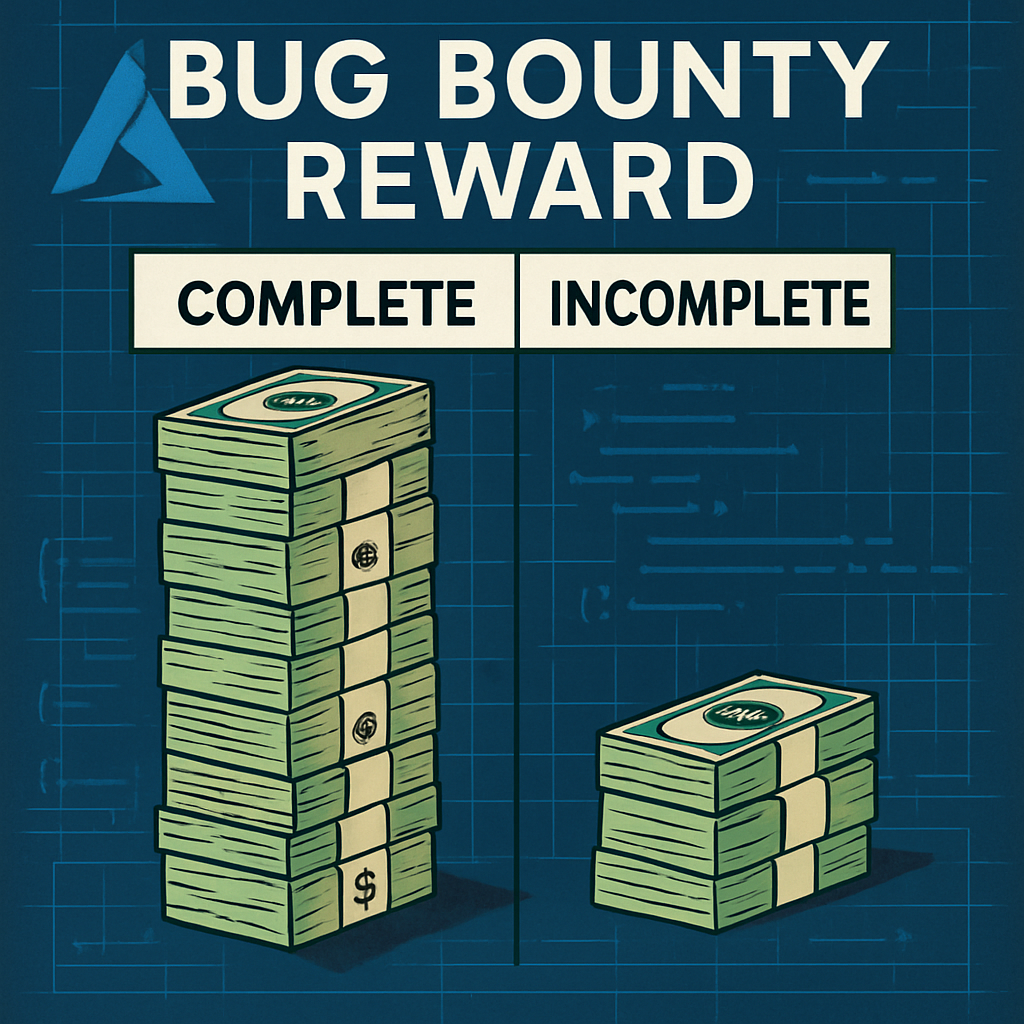
Microsoft has revamped its Azure Bug Bounty Program to put a much bigger premium on the quality of evidence in vulnerability reports. As of October 20, 2026 at 8 AM Pacific Time, only “Complete” submissions—which include a full set of reproducible proof, clear technical analysis, environment specifics, and all required artifacts—qualify for the higher tier of payments. Reports marked “Not Complete” will now fetch dramatically lower rewards.
What Microsoft Changed
Under the new scheme, critical remote code execution and privilege escalation reports can earn up to $40,000 if they meet Azure’s definition of “Complete,” but only $4,000 if deemed incomplete. Other categories have similarly widened gaps: critical information disclosure issues jump from $1,200 (incomplete) to $12,000 (complete), while spoofing or tampering flaws follow an $8,000/$800 scale. Remote code execution at an “Important” severity level now offers $30,000 for complete reports versus $3,000 for incomplete ones. The baseline reward range still spans $400 to $60,000 depending on impact, with Microsoft reserving the right to increase payments for particularly high-severity cases.
What Makes a Report “Complete”?
The company defines completeness by whether someone unfamiliar with the issue (but technically proficient) can reproduce it just from the initial report. Key requirements include a working proof of concept, clear root cause analysis where feasible, version and environment details, and the specific technical steps and attack potential. Missing versions, vague description of affected services or insufficient evidence often result in “Not Complete” assessments—even if the structure is correct.
Different flaw types have different evidence needs: memory corruption proofs must include crash data, call stacks and PoC source code; file redirection might need Process Monitor logs; for NTLM or relay attacks Packet captures are mandatory; web-related issues often require scripts or video demos. All of this evidence must go into the designated Azure Researcher Portal fields—not buried in attachments. Microsoft also allows use of AI tools to aid discovery, but the analysis and evidence must be accurate and usable.
Older submissions—those before the October 20, 2026 cut-off—fall under the old requirements and are evaluated under those criteria.
Why Microsoft Did This—And What It Signals
This shift reflects Microsoft’s push to make bug fixing more efficient. Previously, many reports lacked enough detail up front, forcing security teams to ping researchers for missing info—delaying repro and triage. Now, financial incentives reward well-prepared reports, while skimpy ones are penalized via lower payout.
The adjustment also underscores a growing industry trend: evidence-based valuation of vulnerabilities. High reward gaps for “complete vs incomplete” reports make it clearer what researchers need to deliver. It should lead to better report discipline and faster patch cycles if adopted well.
Analytically, this move shifts more burden onto researchers—but that’s not necessarily bad. Expect a short-term drop in informal or marginal reports, followed by higher average quality. For Microsoft, faster confirmation means faster fixing and less exposure. For researchers, understanding the new evidence checklist becomes the difference between four- and five-figure paydays. The deeper question: how closely competitors follow this model—and whether such strict standards remain feasible as vulnerability discovery scales up.