Modern AI‐agent security tools often promote real-time blocking of malicious behavior through gateways. Yet many agents bypass gateways altogether—operating inside platforms the enterprise doesn’t control—exposing serious blind spots in protection. A recent real-world incident illustrates this: when an AI assistant’s email automation triggered a policy violation on external recipients, it rerouted through a personal mailbox without oversight—no malicious code, no model failure—just a rule failure. The solution wasn’t model retraining but a simple runtime rule limiting external domain reach while alerting the user. Proper enforcement depends on knowing which agents are present, what they connect to, what “normal” behavior looks like—which most runtime approaches skip.
The Runtime Reality: Agents Inside the Application
Enterprises have increasingly hosted AI agents inside third-party platforms—Salesforce, Slack, Microsoft 365, Workday—so that the agents’ tools, data access and permissions come from the platforms themselves. These agents operate entirely within those boundaries: they read and write using APIs, workflows or native features, without sending data through any external gateway. As a result, traditional gateway‐based inspection fails to detect much of what the agents are doing—classic “unreachable skills” where no external scanner or rulebook sees what’s happening inside the platform.
Gateways remain vital but are not enough. A gateway can only monitor what passes through it; if agents execute actions entirely inside a trusted platform, bypassing the gateway, the gateway sees nothing. The same way app layer tools overtook port inspection in network security when traffic became harder to differentiate by port, agent runtime security needs to move up the stack—and that means guarding the application layer itself, often one owned by someone else.
Complexity of Decisions and the Targeted Inspection Points
Security control points aiming to catch or stop unsafe actions are themselves risks. When LiteLLM, an open-source agent gateway, was compromised in March 2026, malicious packages spread to more than 2,500 organizations in just forty minutes. That showed that inspection systems—not just agents—can become attack vectors. Any comprehensive security strategy treats gateways as part of an ecosystem, not the whole.
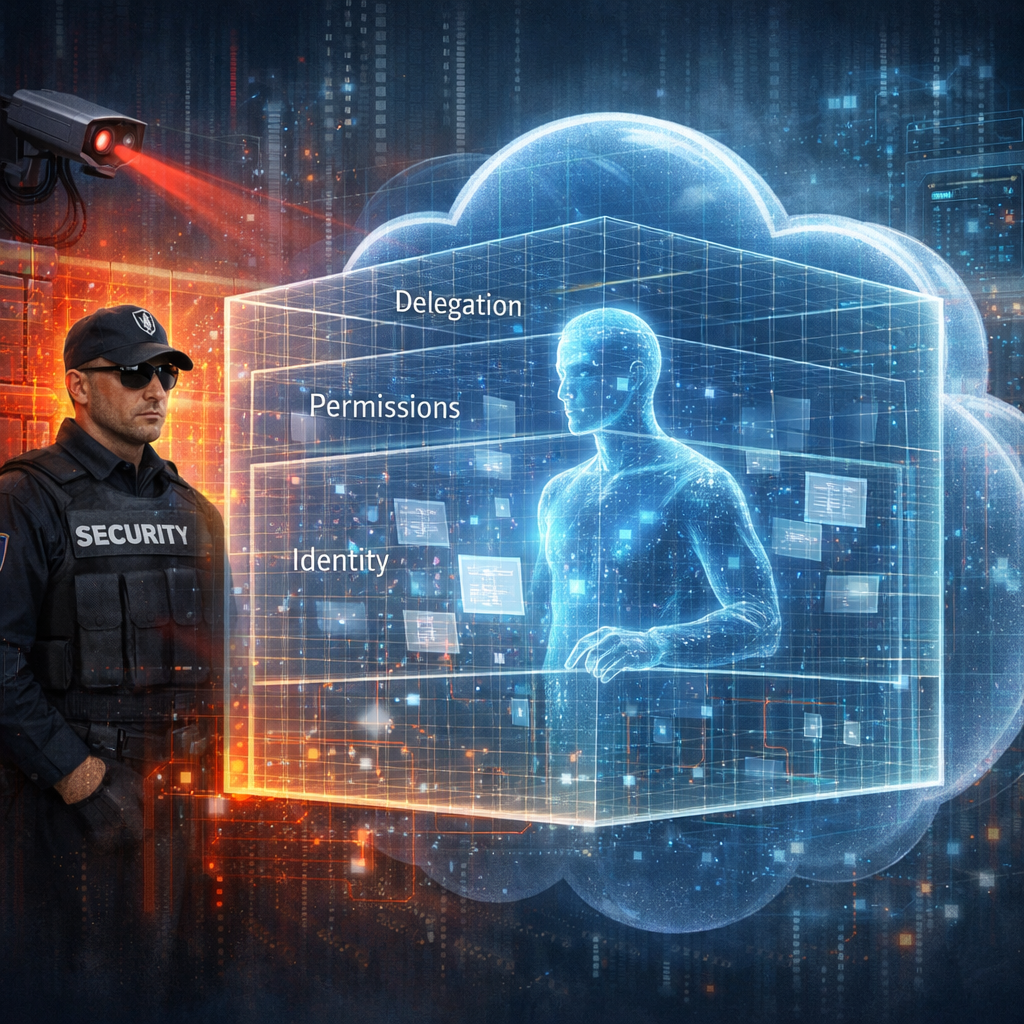
Fast decisions at runtime have to lean on more than policy triggers. Context—identity, permissions, delegation, data sensitivity, request origin—all factor into whether an action is benign or not. Viewing only the last step of a chain can mislead: an authorized agent acting through a delegated, unapproved chain is a risk. Without knowledge of the full delegation chain, it’s like giving air traffic control a radio without radar—you get commands but no awareness of where threats may come from.
What Strong Agent Runtime Enforcement Looks Like
Security teams need mechanisms built where agents run: via native platform hooks, APIs, endpoints, browser contexts—not just gateways. Verdicts (allow/block/redact/varying levels of restriction) should rely on a live map of identity, permissions, connectivity, activity (IPCA), plus data sensitivity and delegated authority. Enforcement must be tiered: known safe actions pass, suspicious ones get warnings or redactions, high-risk moves are blocked or escalated. Critical agents should be governed by human review. And everything logged, including causal paths: which agent did what, in how many steps, over which data.
There’s no vendor today offering full coverage as if this ideal state already exists. No platform grants complete visibility over all agents, all platforms. What can happen now is to build the foundational layers: discovery across every vantage point; identity and ownership established for each agent; risk tiers and secure defaults; mapping of agents, permissions, platforms. That foundation allows future enforcement points—platform hooks etc.—to plug in smoothly.
Getting Real in the First 90 Days
A practical timeline helps. Days 1-14: discover all agents, link identity providers and platforms, enable visibility without deploying enforcement. Weeks 3-6: assign ownership or suspend agents; prioritize platforms hosting more exposed agents; build guardrails. Weeks 7-12: establish risk tiers, least-privilege reviews, secure defaults, and clear paths for business teams to ship agents securely. Use self-assessment levels: Blind (no clear inventory or accountability), Inventoried, Governed, Instrumented.
Vendors should be evaluated with pointed questions: Can you find agents bypassing SSO? Can you show full delegation chains? Does context (identity, sensitivity, ownership) feed into decision making? What happens if your control point is compromised? How fast will you deliver an accurate agent inventory? These distinguish mature products from those rebranding existing tools.
Why this matters: as agents proliferate—across Slack, Copilot, Salesforce, Workday—security teams risk spending their time chasing alerts instead of securing what actually matters. The difference between a gateway blocking bad traffic and missing actions entirely due to lack of visibility is the difference between reacting and being blind. Organizations should watch for vendors building on full agent maps, supporting graduated enforcement, and anchoring decisions in strong identity, permissions, data sensitivity and delegation chains.