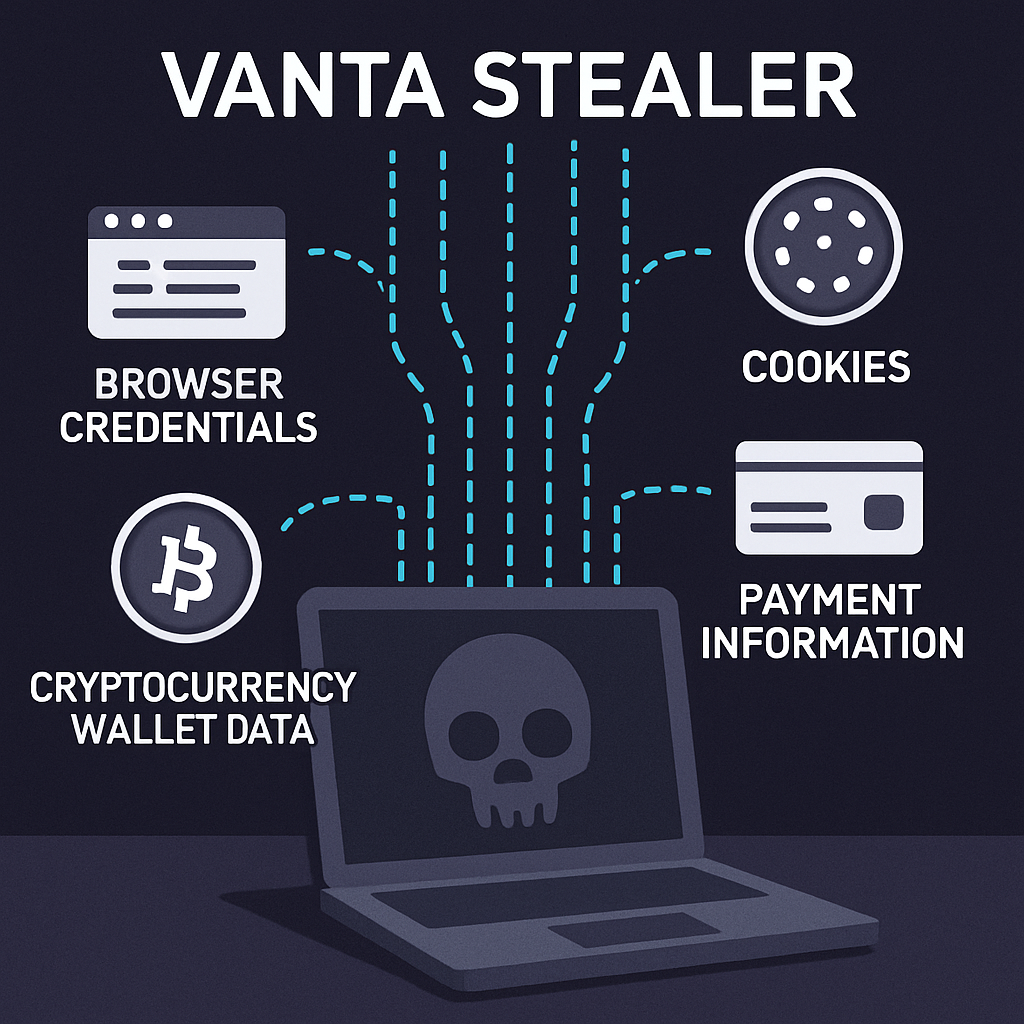
Vanta Stealer is a newly identified information-stealing malware designed to rapidly extract a wide array of sensitive data from infected Windows systems. This includes browser credentials, cookies, payment information, account tokens, cryptocurrency wallet files, and private documents. The malware’s comprehensive data theft capabilities pose significant risks to users who store extensive personal and financial information on their devices.
Upon successful infection, Vanta Stealer can compromise browser sessions, cryptocurrency recovery data, gaming accounts, and messaging profiles. This multifaceted approach enables cybercriminals to gain unauthorized access to various services, potentially leading to financial theft and identity fraud. The malware’s ability to target multiple data sources simultaneously elevates the threat level for everyday users, gamers, and individuals managing digital assets.
Technical Analysis and Distribution Methods
Security researchers at Point Wild have analyzed Vanta Stealer, identifying it as a Python-based malware packaged using PyInstaller and protected with multiple layers of PyArmor. This sophisticated packaging makes the malware more challenging to detect and analyze, while allowing its operators to update individual theft modules efficiently.
Although the initial delivery method of Vanta Stealer was not identified in the analyzed sample, it is likely distributed through common vectors such as phishing emails, fake software installers, game cheats, compromised code repositories, fraudulent updates, and malicious search advertisements. These methods are consistent with tactics used in previous malware campaigns, where attackers exploit user trust and curiosity to initiate infections.
Data Collection and Exfiltration Mechanisms
Vanta Stealer employs a modular approach to data collection, targeting Chromium-based browsers to extract passwords, cookies, and stored payment information. It downloads a dedicated browser extractor during execution, enabling operators to update browser theft tools without modifying the core malware. This method mirrors techniques observed in other information stealers like Vidar, which have been known to employ similar modular strategies.
Beyond browser data, Vanta Stealer collects Discord tokens and verifies them against the service’s API to obtain account details, linked payment information, and server privileges. This process enhances the value of stolen tokens by providing a comprehensive profile of the victim’s Discord account, facilitating further exploitation.
The malware’s reach extends to gaming platforms and communication tools, including Steam, Roblox, Riot Games, Valorant, Minecraft, Telegram Desktop, and Mullvad VPN configurations. It specifically targets wallet files and documents containing recovery phrases or private keys, posing a significant threat to cryptocurrency holders. Additionally, Vanta Stealer captures screenshots and webcam images, adding context to the stolen data and potentially increasing its utility for malicious actors.
After gathering the targeted information, Vanta Stealer compiles a summary file and creates a compressed archive containing the stolen data. This archive, along with victim-specific metadata such as user identifiers and execution modes, is then transmitted to a predefined command-and-control server via an HTTP POST request.
The emergence of Vanta Stealer underscores the evolving sophistication of information-stealing malware. Its comprehensive data collection capabilities and modular design make it a formidable threat to users who store sensitive information on their devices. To mitigate the risk of infection, users should exercise caution when downloading software from untrusted sources, remain vigilant against phishing attempts, and ensure their systems are equipped with up-to-date security measures. Regular monitoring of accounts for unauthorized activity is also crucial in detecting and responding to potential compromises promptly.