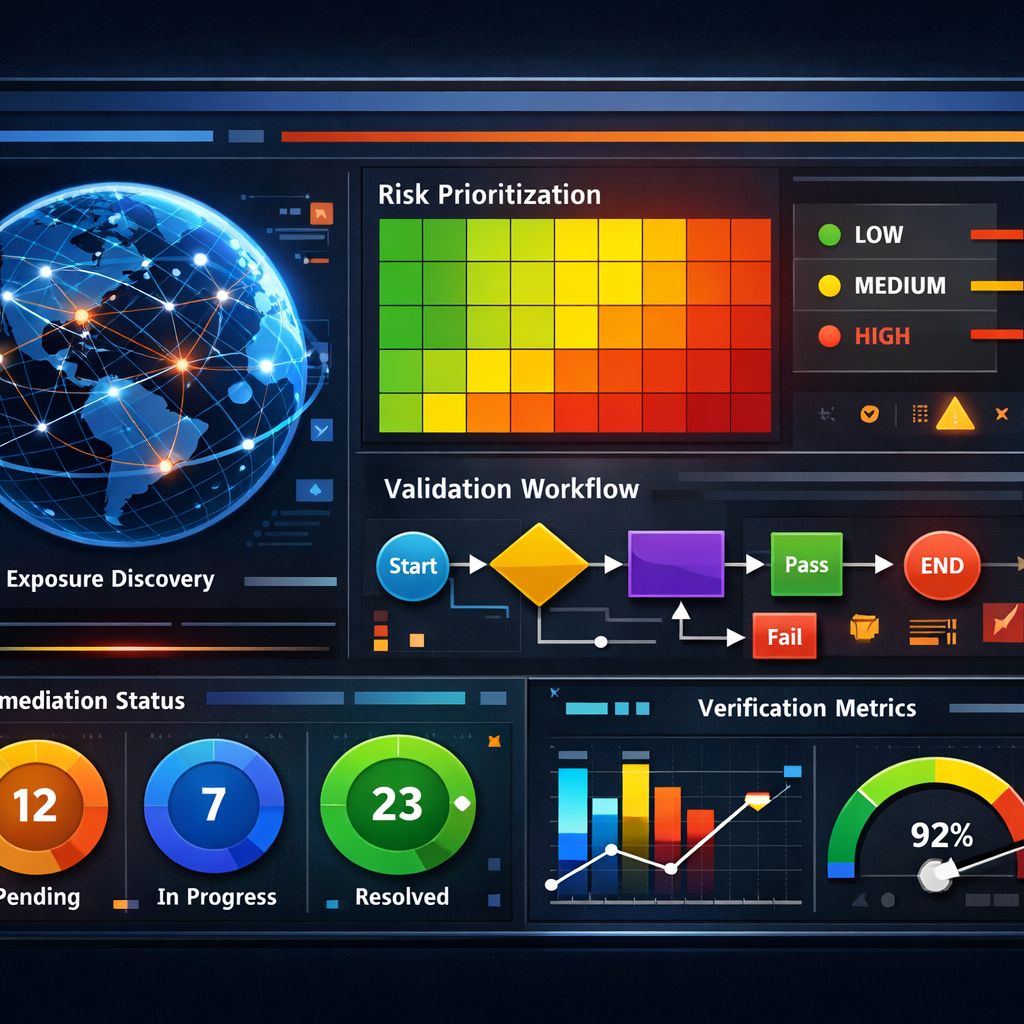
Modern exposure management platforms promise comprehensive visibility and faster fixes—but many still leave critical gaps. To assess whether a platform truly supports Continuous Threat Exposure Management (CTEM), test it against five essential capabilities spanning discovery, prioritization, validation, remediation, and verification. These benchmarks help identify tools that move from generating alerts to reducing real risk.
1. Rich, Unified Discovery That Closes Blind Spots
A credible platform must integrate internal and external asset discovery. Internally, it should reconcile data from inventories, endpoints, cloud infrastructure, and identity systems to reveal missing ownership, stale assets, and protection gaps. Externally, it should pick up forgotten subdomains, exposed services, brand impersonation, and phishing threats—elements attackers frequently exploit.
2. Risk Prioritization Beyond Severity Scores
Alerts without context often bottleneck response. A useful exposure management solution weighs real-world risk signals: reachability, whether exploits are actively used in the threat landscape, business impact, and existing protections. Severity metrics like CVSS are a starting point, but without control context and threat intelligence, they provide an incomplete picture.
3. Validation That Confirms Exposure and Feasible Response
Before action, exposure must be proved. Can the vulnerability or exposed asset actually be accessed? Which existing controls might stop or limit attackers? A platform should differentiate between observed evidence and assumptions, including distinguishing unproven attack paths, enabling safer testing modes, and clarifying what parts of the fix may disrupt operations or generate false positives.
4. Safe Remediation That Fits Workflows and Scale
Knowing what to fix first only matters if fixes happen. Effective tools automatically map ownership, suggest safe interim protections (e.g., virtual patches, IPS rules, impersonation takedowns), and integrate with organizational workflows for change approval and ticketing. Importantly, each fix should be verified—both temporarily (edge controls) and permanently (patches, configuration changes).
5. Evidence of Change—What Got Fixed, What’s Still at Risk
After remediation actions are marked complete, the platform must clearly show what changed and whether vulnerabilities truly closed. Tracking must include what’s removed, what’s mitigated, and what remains or was intentionally deferred. Measurements like mean time to remediate (MTTR), recurring findings, failed actions, and aging mitigations are crucial for understanding ongoing exposure.
Platforms differ in how they fulfill these tests. The most advanced combine internal asset intelligence, external discovery, threat intelligence, and brand protection; they then bring that security context into prioritization, exploitability validation, and remediation. They not only flag exposures but confirm which ones matter now, propose safe fixes, and verify impact after deployment.
What this means is simple: exposure management isn’t a set-and-forget tool—it’s a cycle. Organizations should adopt tools proven across all five stages, not just good dashboards or isolated components. The test is whether findings translate into defensible, measured reduction in risk—not just more alerts.
Why it matters: attackers move quickly, chaining exploits and external exposure in hours while defenders often lag. By applying these five benchmarks you gain clarity on what your exposure management platform *actually* protects—and what it doesn’t. Going forward, demand products that don’t just let you observe risk—but let you responsibly act and show results.