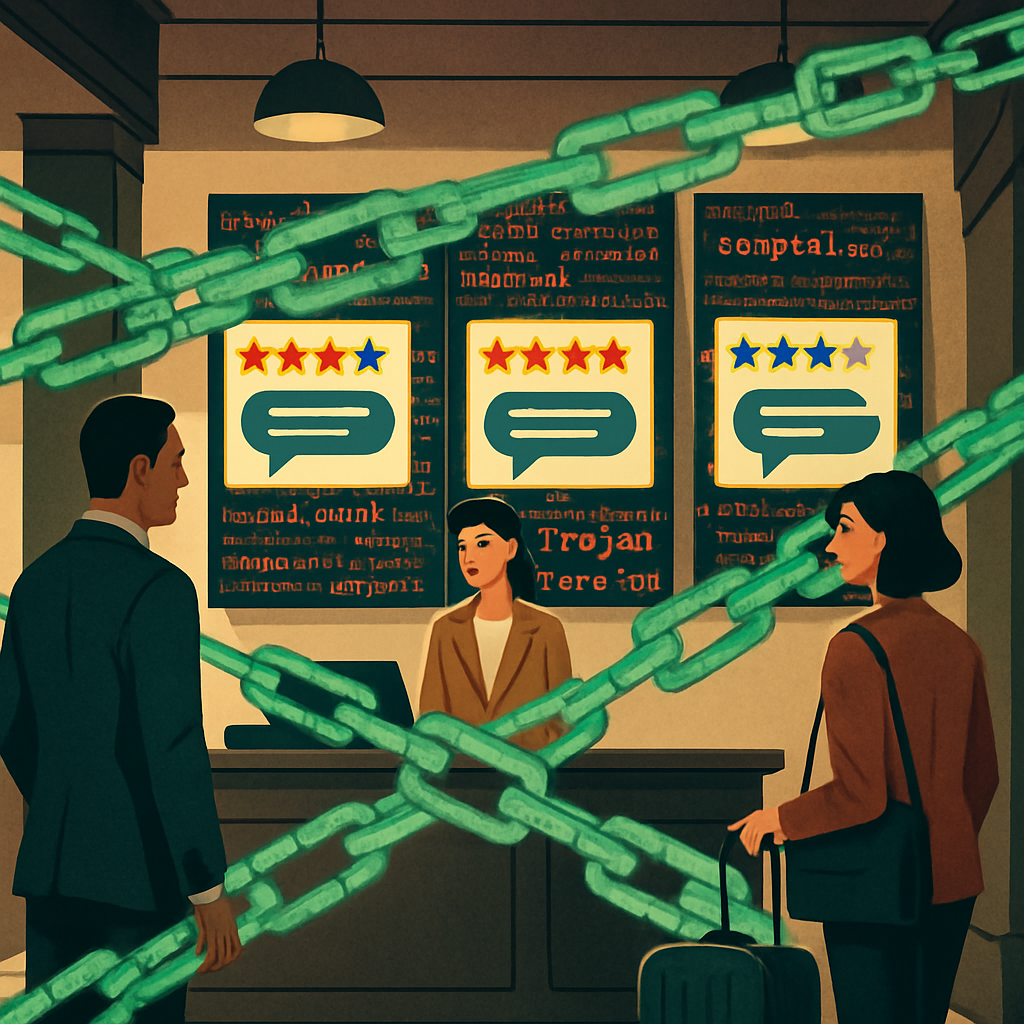
Attackers are now exploiting hotels with fake negative reviews, tricking staff into downloading malware masked as customer photos or documents. This new strategy involves disparaging messages—claims of unclean rooms, disputes with employees, or threats of lawsuits—with links to what appear to be multimedia files. These links instead deliver malware that conceals its control infrastructure on public blockchains. The malicious families involved are EtherRAT and TONResolver.
From Phishing Emails to Blockchain-Backed C2 Servers
Targeted teams typically include front desk, reservations, and guest relations—roles where dealing with guest complaints is standard. In recent attacks, emails lure staff with an archive supposedly containing images or videos supporting a negative review. Instead, the archive holds a Windows shortcut file (.LNK) disguised as a photo. When opened, it executes code that installs malware using Node.js. A dummy MP4 file inside may alter its hash with each download to evade fixed signature detection.
EtherRAT and TONResolver don’t hardcode command-and-control (C2) addresses into malware binaries. Instead, they retrieve addresses dynamically via public blockchain smart contracts. EtherRAT reads data from an Ethereum contract using JSON-RPC calls, decodes it, and extracts the C2 address. TONResolver follows a parallel technique on the TON blockchain. That means infected hosts can discover new servers if old domains are taken down—without needing updated malware.
Risks and Recommendations
This stealthy architecture helps attackers sidestep traditional takedowns. Blockchain records are immutable, so even after domains or servers are blocked, the instructions leading to replacement infrastructure remain online. Because communication via blockchain APIs resembles legitimate wallet traffic, it can be hard to distinguish benign from malicious behavior. Blocking access to Ethereum endpoints may still leave TON attacks viable.
To protect against this type of campaign, hotels should treat unsolicited complaint emails with the same critical eye as other phishing attempts. Staff training is essential—it’s not enough to rely on static email patterns or file hashes. Monitoring computer systems for unusual Node.js processes and cross-referencing endpoint behavior with email triggers are also advised. Public-facing inboxes in departments like customer support or sales may be especially vulnerable.
Indicators of compromise already identified include specific Ethereum and TON smart contracts, plus various C2 URLs with defanged domain names to prevent accidental clicks. Security teams and intrusion analysts should incorporate these IoCs into their detection systems.
Why this matters: this campaign demonstrates how threat actors are evolving. By combining social engineering, blockchain technology, and malware, they’re making attacks more adaptable and harder to shut down through traditional defenses. For hotels—and any organization handling customer feedback—this is a wake-up call. Watch for tech-enabled phishing using multimedia lures, consider the role of Node.js in unexpected contexts, and factor blockchain-based C2 resolution into your threat model.