An espionage group labelled FamousSparrow is exploiting internet-facing Microsoft Exchange servers to install a newly observed backdoor called SparroWocky. It’s been used since mid-2025, and is now the group’s primary implant tool, replacing SparrowDoor. Its stealth techniques are raising alarm among government IT agencies across Latin America.
How the breach unfolds
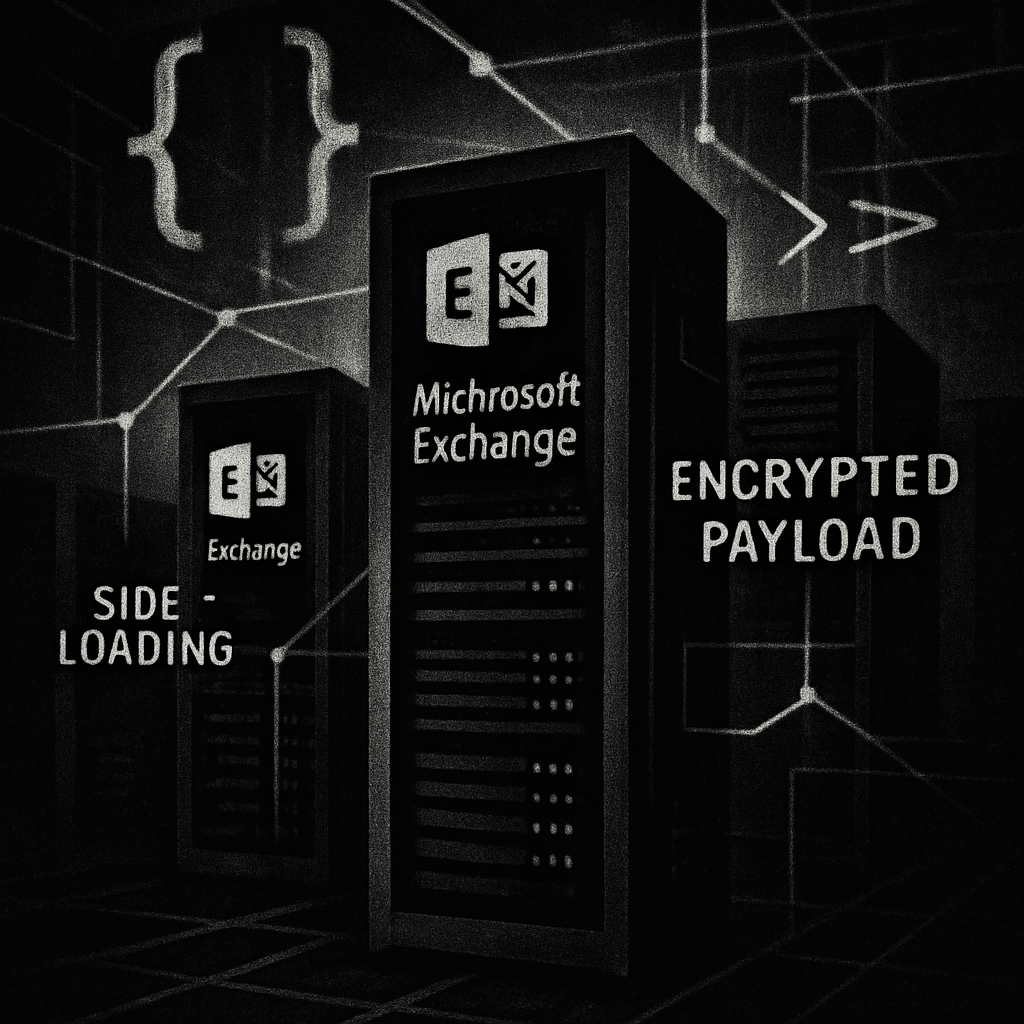
The group gains entry through exposed Exchange servers, taking advantage of flaws in on-premises email infrastructure. Once inside, they deploy a three-part loader consisting of a legitimate executable, a malicious dynamic-link library (DLL), and an encrypted payload.
The executable uses DLL side-loading to trick the system into loading the fake library under the guise of a trusted one. The encrypted payload never gets saved to disk; instead, once decrypted it’s mapped directly into memory. To establish persistence, the backdoor leverages a Windows service or modifies Registry Run keys, and gathers basic system information such as machine name, OS version, user and domain details, and network-interface configurations.
Capabilities and stealth
SparroWocky supports file operations, screenshot capture, remote command execution, data exfiltration, and can serve as a TCP proxy. It communicates using TLS and encrypts transferred data with RC4. Operators can deploy Beacon Object Files—compact modules commonly used in red-team operations—to expand functionality without touching disk with full-sized binaries.
To evade detection, SparroWocky uses advanced stealth tactics: obscuring call stacks, dynamically resolving Windows API functions, hiding thread start addresses, and faking module load records. Such tactics complicate usual security monitoring, pushing defenders toward memory- and behavior-based threat detection.
Regional focus, timeline & targets
Since mid-2025, FamousSparrow has concentrated the campaign on Latin America—targeting government bodies in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela. Roughly 90% of its known targets over that period come from those countries, marking a departure from its earlier, more global focus.
The group’s known activity stretches back to at least 2019, and includes prior use of proxy-related vulnerabilities such as ProxyLogon in its Exchange-based operations. In one noted case, they breached an energy-sector entity via Exchange server exposure.
Responding to the threat
Defensive advice centers on patching public-facing Exchange servers promptly, restricting unnecessary external access, and keeping servers on supported software versions. Monitoring should include hunting for unexpected DLL side-loading, new Windows services or Registry Run entries, unusual .dat payload files, and outbound TLS sessions directed at known command-and-control infrastructure.
Security teams are also urged to audit Exchange and IIS logs for anomalies, isolate suspicious systems, preserve memory for forensic purposes, rotate credentials that may have been exposed, and review network neighbors for lateral movement.
Indicators of compromise have already been detailed, including specific SHA-1 hashes associated with loader DLLs and in-memory samples, plus a list of IP addresses tied to command-and-control servers first seen throughout early 2026 and late 2025.
FamousSparrow’s shift toward a modular, custom backdoor tailored for stealth and control signals both a maturing operation and a growing risk to enterprises relying on on-premises Exchange infrastructure.
Analytical view: This campaign underscores a serious threat vector—public-facing Exchange servers continue to be a high value target for advanced persistent threat actors. SparroWocky’s design shows FamousSparrow is investing heavily in operational stealth, not brute force. Organizations that still host their own Exchange servers must treat exposure as urgent, adopt robust detection beyond signature-based tools, and prepare incident-response plans geared for advanced backdoors that rarely leave artifacts on disk.