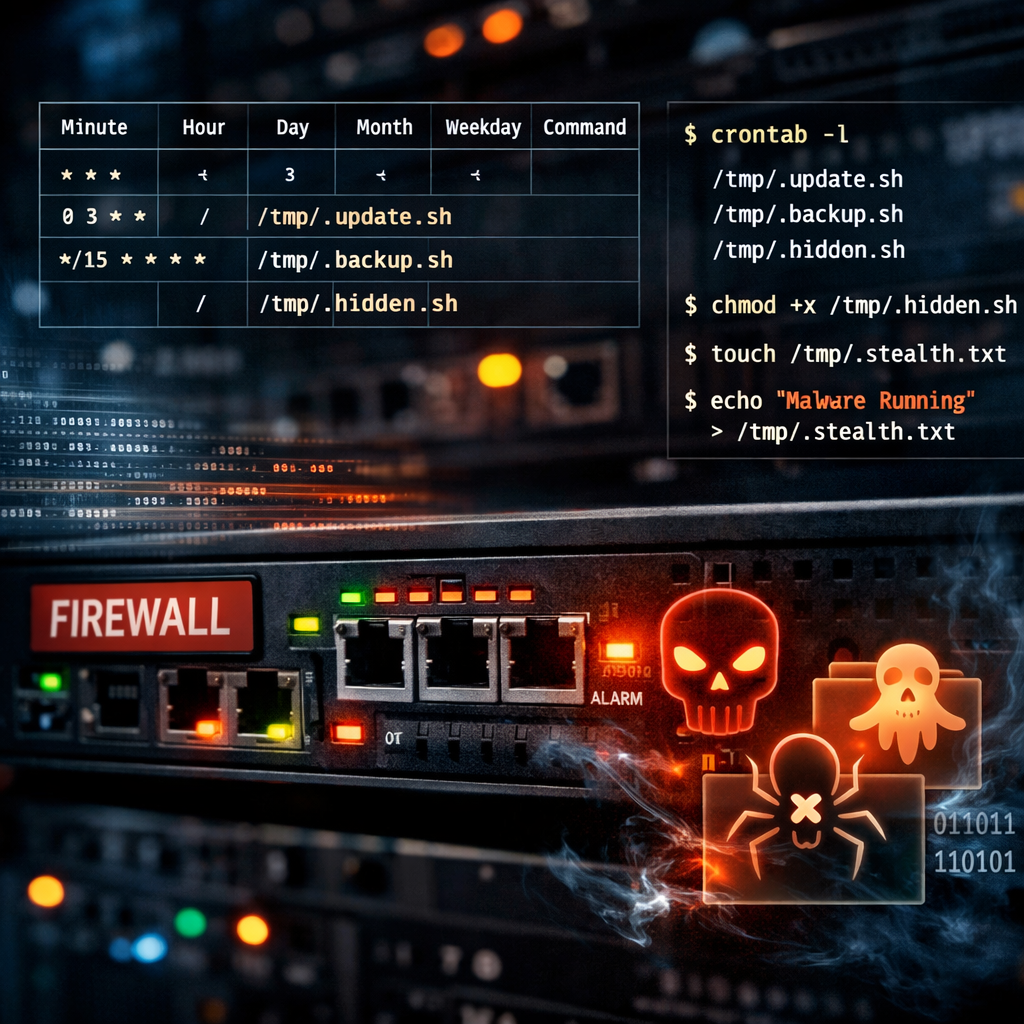
Enterprise firewalls, routers, and switches are being targeted by a new Linux-based botnet named Evooo1Bot, which employs stealthy techniques to reinstall malware on compromised devices every five minutes. Discovered by FortiGuard Labs in August 2026 and detailed more recently by researchers at Eclypsium, this threat shows how attackers are pushing deeper into network edge infrastructure. Despite efforts to kill infected processes and remove malicious files, a hidden cron job embedded on the device simply downloads and re-executes the malware script, undeterred by usual cleanup steps.
Evooo1Bot Using Hidden Cron Jobs to Persist on Firewalls Every 5 Minutes