On October 20, 2026, Google’s Chrome Root Program and Mozilla confirmed that private keys belonging to eight intermediate certificate authority (CA) certificates from India’s eMudhra (under its emSign brand) have been compromised. These keys are responsible for signing TLS and code-signing certificates, meaning whoever holds them could issue certificates trusted by major browsers. The incident has triggered urgent security patches and certificate revocations across browsers, trust stores, and programming libraries.
What Breached & How It’s Being Mitigated
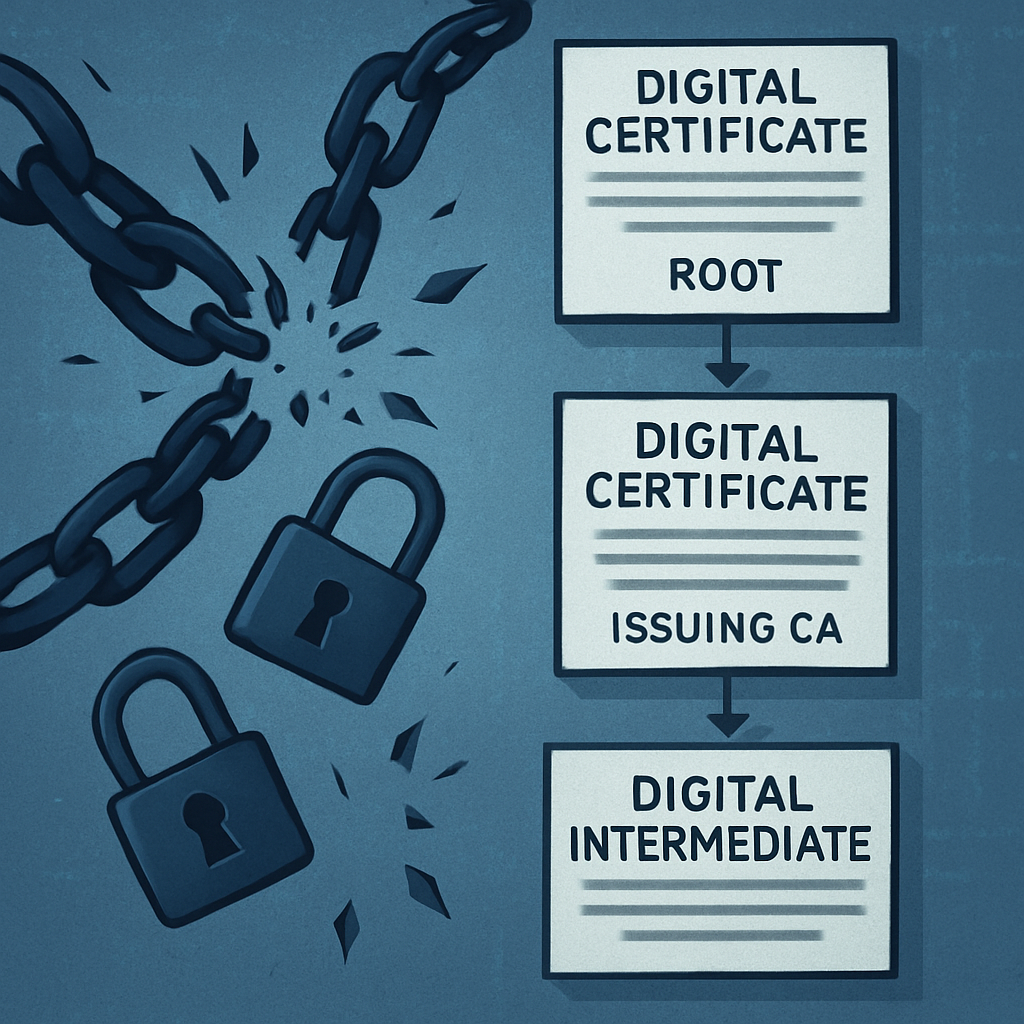
The compromised certificates include six TLS intermediates — covering domain-validated, organization-validated, and extended validation certificates — plus two code-signing intermediates. The affected certificates were issued under emSign Root TLS CA-G3, which chains up to emSign ECC Root CA-G3, a root present in Chrome, Apple, and until now, Mozilla stores. Cross-signed variants of the compromised intermediates under Sectigo’s AAA Certificate Services also exist.
Following the discovery, Chrome and Firefox pushed revocation blocks. Chrome deployed a CRLSet block for the six TLS intermediates by around 19:45 UTC on October 17. Mozilla followed with a OneCRL block for Firefox installations two hours later in the evening. Apple blocked the affected certs on October 19, Microsoft on October 20. The CA, eMudhra, has revoked the certificates and is under investigation.
Broader Impact & Technical Fallout
The compromise means that without these fixes, clients and servers using software that doesn’t reliably check for revocation could still accept connections or trust certificates signed with the compromised keys. Browsers like Chrome and Firefox already reject chains containing those intermediates. Other components — such as programming language cert bundles and operating-system trust stores — have begun dropping trust in emSign ECC Root CA-G3 and related roots.
Here’s how key software has responded:
- Go has released versions 1.27.3 and 1.26.10 that reject any certificate chains containing the eight compromised keys (with fixes in its standard library). Existing applications must be rebuilt using those Go versions.
- Firefox issued updates (158.0.1, ESR 115.43.1, ESR 153.5.1) that include the block list via OneCRL for setups without Remote Settings.
- Trust-store and library vendors including NSS, Python’s certifi bundle, Rust’s webpki-roots, and Homebrew ca-certificates have removed emSign ECC Root CA-G3 from their lists. Some also dropped related roots to prevent potential exposures. Node.js and Composer both have proposed patches in progress.
Root Store Removal & Questions Remaining
Mozilla removed emSign ECC Root CA-G3 from its NSS trust store on October 20. Chrome plans to remove the same root in its root store’s upcoming version (version 43) and is reviewing eMudhra’s other root (“emSign Root CA-G1”) for continued trust. Meanwhile, the exact timeline of when the keys were exfiltrated, how, and by whom remains unclear.
Researchers noted that no TLS certificates chaining to the six TLS intermediates had been logged in Certificate Transparency (CT) before the blocks — suggesting no misuse had been detected in public logs. That said, abuse could still have occurred if private, unlogged certificates were issued.
Countries and orgs operating software that doesn’t auto-fetch revocation lists (or where such checks are disabled) are urged to take proactive steps: remove trust in the affected roots, apply patches promptly, and monitor for any signs of misuse.
This breach underscores the systemic risk posed by intermediate CA key compromises. The integrity of TLS and code signing security hinges on each trusted CA acting responsibly — but downstream systems, libraries and trust stores must act fast when that trust is broken. What to watch: whether eMudhra publishes a detailed root cause analysis, whether unlogged misuse emerges, and how trust store policies evolve to better detect or prevent similar threats in the future.