Ruby developers have patched a grave memory corruption vulnerability in Ruby’s string case conversion logic, dubbed “ruby2ßhell”, that permits remote code execution (RCE) under certain conditions. The issue, identified as GHSA-34m4-m9fh-gqp5 and disclosed by Veria Labs, stems from how Ruby handles certain one-byte legacy encodings during transformations like uppercasing and case comparisons. UNIX UTF-8 strings are not affected.
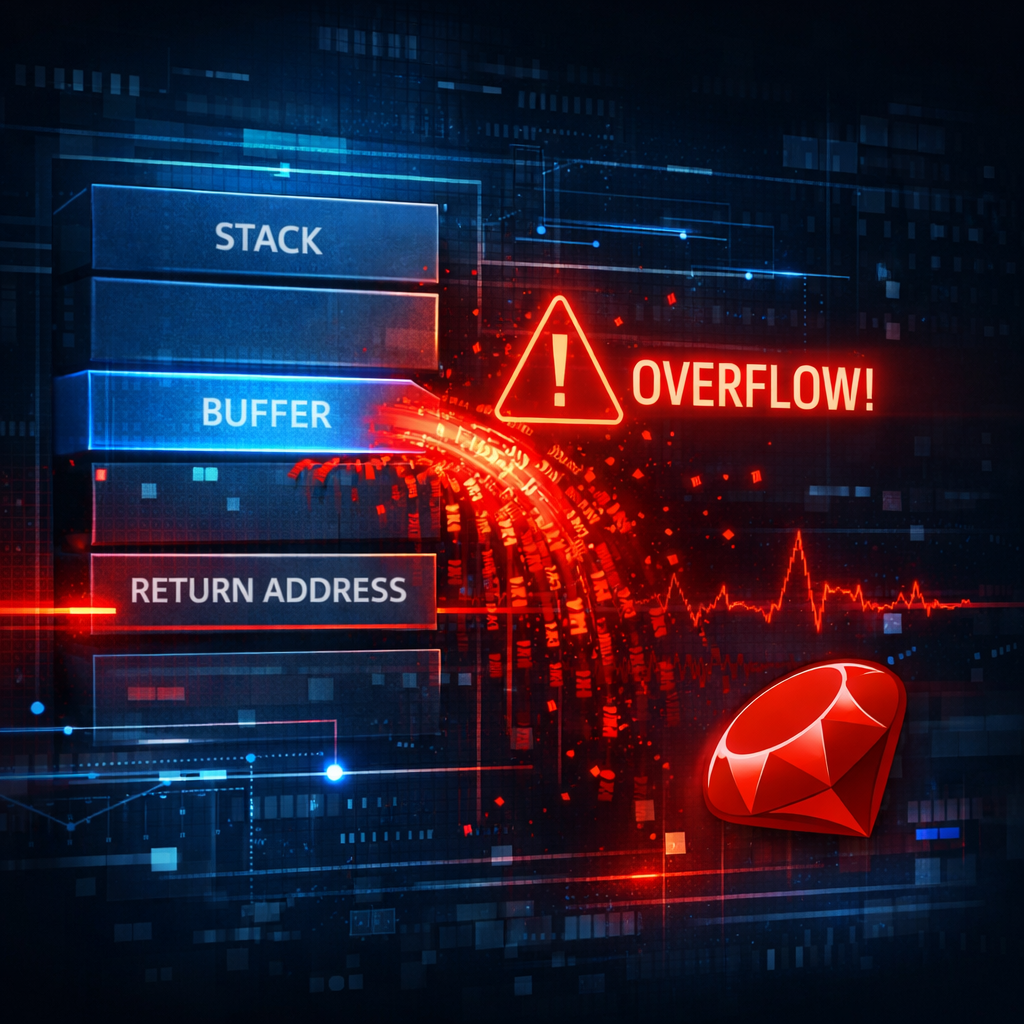
The flaw arises specifically when converting the German lowercase letter “ß” (in single-byte encodings such as ISO-8859 or Windows-125x) to uppercase “SS”. In these encodings, a single input byte may result in two output bytes. Unfortunately, the conversion loop only checks for space for one byte. If only one byte remains in the output buffer, and two are written, the second byte overflows past the buffer boundary. This creates a one-byte heap overflow and potentially even an out-of-bounds read.
Who’s at Risk
The vulnerability is present in Ruby versions dating back to 2.4.0, and affects all supported branches up to 3.3.13, 3.4.12, and 4.0.9. Earlier branches such as Ruby 3.2 and below are out of support and thus will not receive patches. Case conversion methods exposed to this vulnerability include upcase, swapcase, downcase(:fold), and casecmp?. The bug does not affect strings encoded in UTF-8 due to different processing paths.
Web frameworks like Ruby on Rails and classic Sinatra (in default configuration) expose this flaw because they use these string case conversion routines potentially on untrusted data. Other environments like plain Rack are not exposed by default, unless application code explicitly processes untrusted input using the affected routines and single-byte encodings.
Products & Fixes
Several self-hosted apps with bundled Ruby runtimes are confirmed vulnerable, including GitLab 19.6.0 (Ruby 3.3.13), GitHub Enterprise Server 3.22.5 (4.0.9), Mastodon 4.7.5 (4.0.9), OpenProject 17.9.7 (4.0.9), Discourse 2026.10.1 (3.4.7), and Chatwoot 4.20.0 (3.4.4). Administrators should verify the runtime version embedded in the deployment, since replacing the system Ruby doesn’t necessarily update Ruby included in containers or vendor-bundled apps.
At the time of public disclosure, proof-of-concept exploits already demonstrate that in certain scenarios, the overflow can be turned into remote code execution. Not every possible overflow will lead to full compromise, but risk is non-trivial in exposed setups.
Remediation Steps
The Ruby project released patched versions 3.3.14, 3.4.13, and 4.0.10 on November 18, 2026, which resolve this and several other security flaws in string conversion and regular expression handling. Users on older branches must upgrade to a supported version to receive fixes. Self-hosted product maintainers need to ensure their runtime—or that of underlying services—is updated to the fixed version or replaced with a version not affected. Prioritize internet-facing endpoints where vulnerable code paths can be triggered without authentication.
Veria Labs have mapped out affected products, versions, and vendor patches. They intend to publish a full proof-of-concept roughly one week after the initial disclosure.
This vulnerability does not appear to have been detected in the wild yet, and is separate from other recent exposure such as the GitLab CI/CD regex flaw CVE-2026-97229.
Why this matters: Case conversion functions are so fundamental and seemingly innocuous that they often go uninspected. Yet they’re part of everyday string handling throughout frameworks and libraries. This discovery shows how some legacy encoding support still lurks behind dangerous edge cases. The fact that an RCE is possible from default web apps means many servers are exposed today. What to watch: vendor advisories to ensure patch uptake, scans of apps that bundle Ruby runtimes, and tracking whether proof-of-concept code leads to real world attacks.