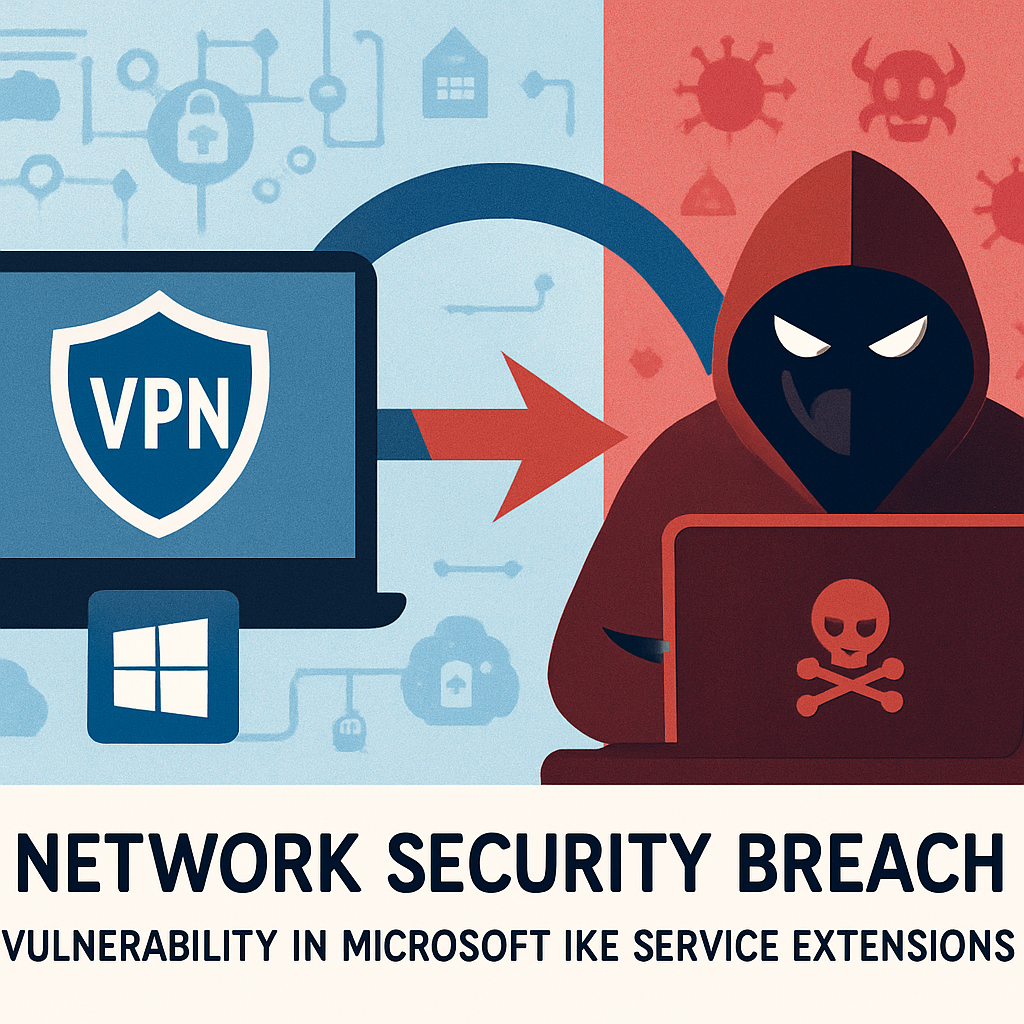
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently added a critical vulnerability in Microsoft’s Internet Key Exchange (IKE) Service Extensions, identified as CVE-2026-33824, to its Known Exploited Vulnerabilities catalog. This move follows confirmed reports of the flaw being actively exploited in the wild.
CVE-2026-33824 is characterized as a double-free vulnerability within the IKE Service Extensions. In software terms, a double-free condition arises when a program attempts to release the same memory space more than once, leading to potential memory corruption. Such corruption can be manipulated by attackers to crash services, leak sensitive information, or execute arbitrary code on the affected system.
Given the critical nature of this vulnerability, CISA has set a remediation deadline of August 21, 2026, for organizations governed by Binding Operational Directive 26-04. This tight timeframe underscores the urgency and the potential risk posed by unpatched systems.
IKE plays a pivotal role in Internet Protocol Security (IPsec) deployments, facilitating the negotiation of security associations and cryptographic keys essential for Virtual Private Network (VPN) connections. A successful exploitation of this vulnerability could grant attackers unauthorized access to systems, particularly those that expose IKE-related services to the internet.
While there is no current evidence linking this vulnerability to specific ransomware operations, the nature of remote code execution flaws in externally accessible services makes them attractive targets for various threat actors, including initial-access brokers and espionage groups.
Organizations are strongly advised to apply the security updates provided by Microsoft without delay. Additionally, it’s prudent to review network configurations to ensure that IKE services are not unnecessarily exposed to untrusted networks. Monitoring system logs for unusual activities related to IKE services can also aid in early detection of potential exploitation attempts.
In scenarios where immediate patching isn’t feasible, temporary measures such as restricting IKE traffic to trusted networks or limiting UDP ports 500 and 4500 at perimeter firewalls can be considered. However, these should be viewed as interim solutions, with the primary focus remaining on deploying the official security patches as soon as possible.
Given the criticality of this vulnerability and its active exploitation, organizations must prioritize remediation efforts to safeguard their systems and data from potential compromise.