A serious vulnerability in Amazon Web Services’ MCP (Model Context Protocol) Gateway has been patched after it was discovered that certain authenticated users could exploit it to access internal services and possibly cloud credentials.
What the Flaw Is
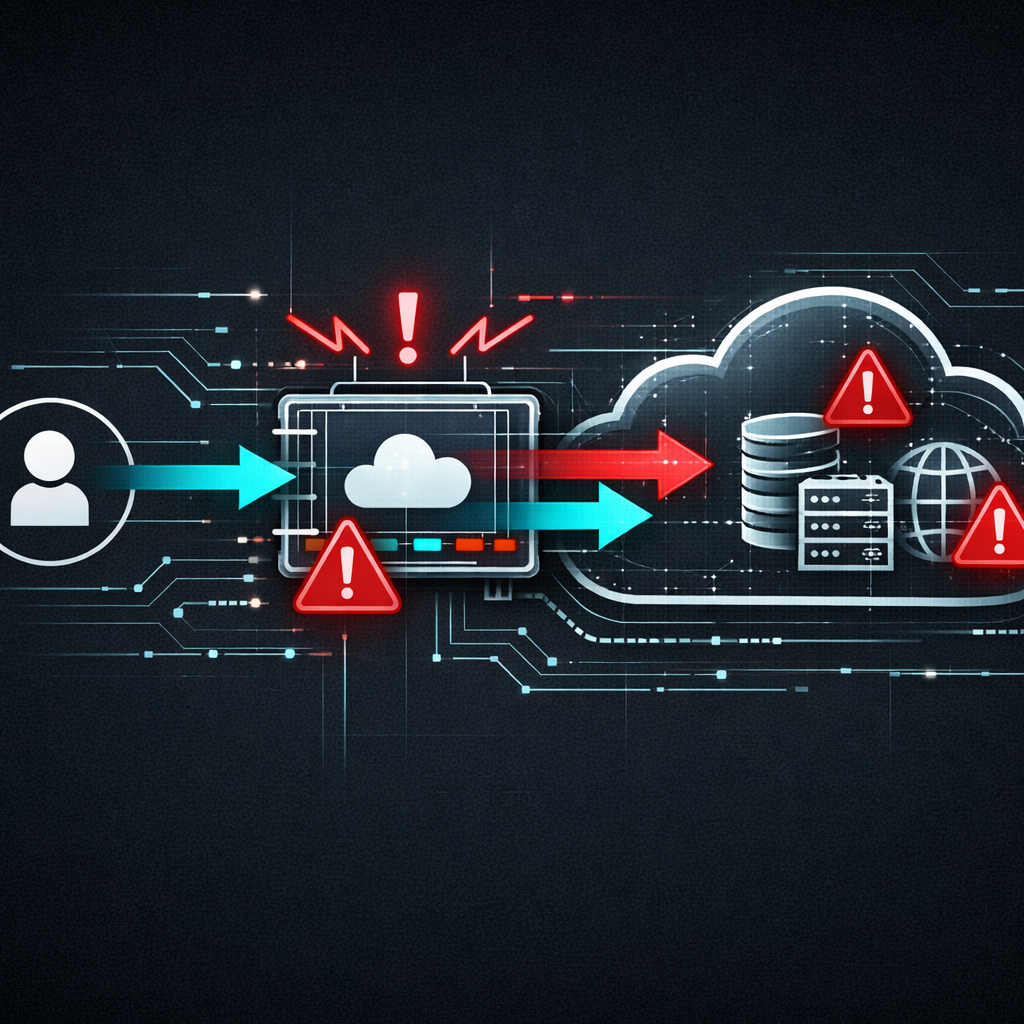
The weakness, known as CVE-2026-125926, exists in AWS MCP’s mcp-gateway-registry versions from 1.0.3 through 1.34.0. In these versions, when users with server registration or update permissions submit an “upstream address,” the gateway fails to properly verify that the address is safe. That allows someone with permissions to point the gateway at internal services within the deployment’s network. Sometimes the gateway returns responses from those services, granting users access to data they shouldn’t normally reach.
Risks Involved
The core risk arises when the gateway runs with an attached cloud role. If attackers can coerce the gateway into accessing internal endpoints—such as metadata services exposed only to cloud infrastructure—they might retrieve temporary credentials. This type of issue is similar to previously known metadata-based attacks.
Fixes and Mitigation
The vulnerability was disclosed on November 11, 2026. AWS released version 1.35.0 of mcp-gateway-registry with an upstream address validation update. But administrators should know that the fix does not automatically purge existing upstream addresses—stored misconfigured entries must be reviewed and cleaned up manually.
Workarounds Until You Can Upgrade
- Restrict permissions: Limit who can register or modify servers to tightly controlled, trusted accounts.
- Control network egress: Block or restrict outbound connections from the registry and auth-server components.
- Require IMDSv2 on EC2 instances, reducing metadata exposure risk.
- Minimize IAM role permissions and rotate credentials if misuse is suspected.
- Audit logs for unexpected server registrations or address modifications that could signal exploitation.
Those running versions 1.25.0 through 1.34.0 must note that earlier fixes—such as the one in 1.25.0 for a separate external API issue—do not cover CVE-2026-125926. Even forks or derived projects of MCP-Gateway need the 1.35.0 patch to fully address the issue.
Your organization may already use MCP-Gateway if deploying AI/ML infrastructure or systems needing context, tool proxying, and server discovery in a managed environment. MCP-Gateway is intended to centralize access control and routing for model context services. That makes this flaw especially dangerous—it turns that centralization into a potential attack vector.
The emergence of this vulnerability underscores how even authenticated parts of cloud systems can be hijacked when safeguards are incomplete. Watch closely for unusual internal connections, clean up misconfigurations, and assume permissions are always a risk until fully locked down. Any delay in applying fixes or reviewing settings may leave sensitive internal services and credentials exposed.