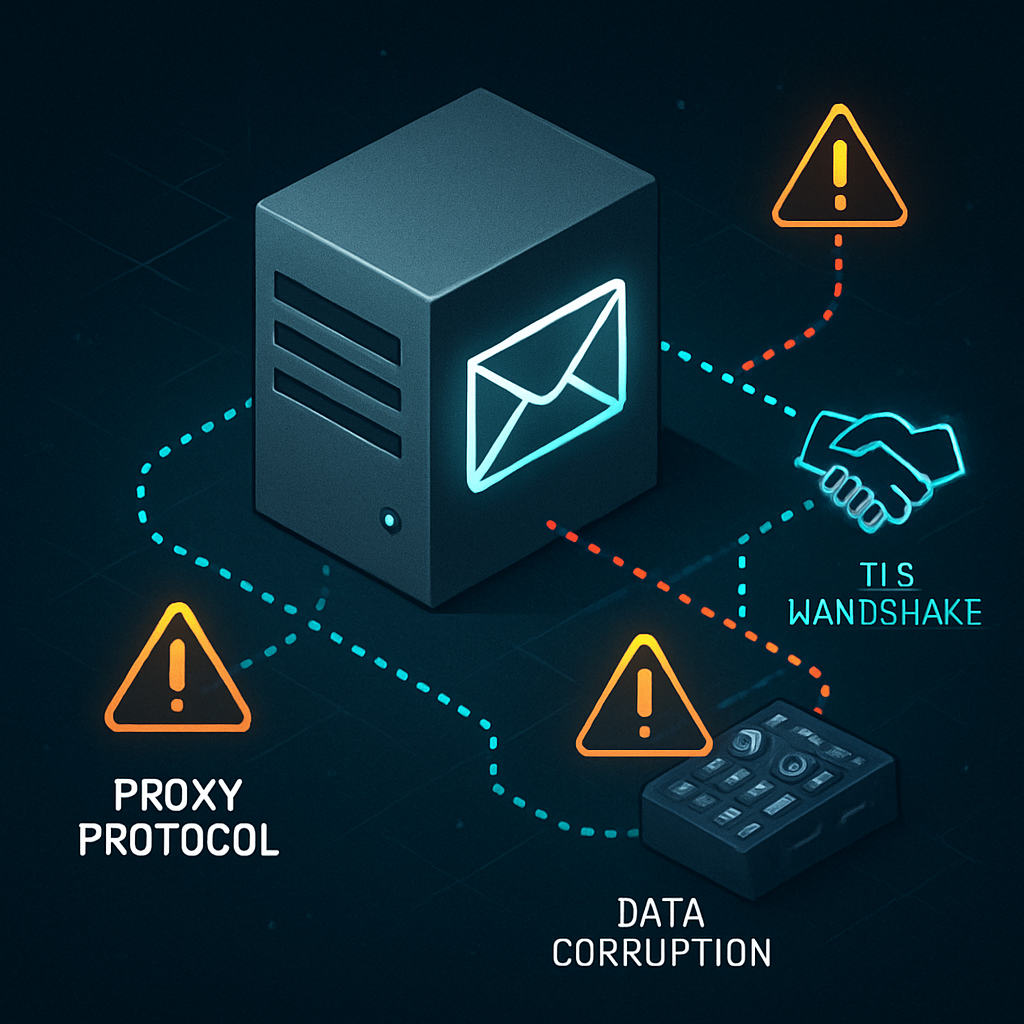
Exim has just released version 4.100.1 to fix four vulnerabilities ranging from medium to high severity, including Proxy Protocol bugs, heap corruption, a GnuTLS use-after-free flaw, and SMTP smuggling. The update, announced September 18, 2026, applies to servers running Exim versions between 4.83 and 4.100 depending on configuration. Administrators are urged to upgrade immediately.
Key Vulnerabilities Addressed
The most critical issue—tracked as GCVE-25-2026-09-50-1—happens when Exim is configured with Proxy Protocol version 1. In this scenario, a remote attacker could force the server to read past the end of a heap allocation by about 230 bytes, ending with a null-byte write. Exploitation requires a misconfigured or malicious proxy. The flaw could lead to heap corruption, unpredictable behavior, or even remote code execution. The update fixes the logic that handles data reads to prevent the out-of-bounds access.
Another high-severity issue, GCVE-25-2026-09-55-1, affects Proxy Protocol version 2. Here, uninitialized stack data may leak when Exim processes proxy headers under certain conditions. The patch ensures Exim repeatedly reads until it has received the full Proxy Protocol header before moving on, closing the gap where partial or malformed headers could cause exposure.
There’s also a GnuTLS issue, GCVE-25-2026-09-51-1, tied to TLS-on-connect behavior. Servers built with GnuTLS 3.6.4 or newer and configured with the non-default setting tls_early_banner_hosts are vulnerable to a use-after-free condition that can crash mail reception processes. Disabling tls_early_banner_hosts provides a mitigation until patching is possible. The new release changes control flow to avoid accessing memory after it’s freed.
SMTP Smuggling & Broader Impacts
The fourth flaw, GCVE-25-2026-09-56-1, is a medium-severity SMTP smuggling vulnerability present in all Exim versions up to and including 4.100. It allows attackers who have their messages rejected during the SMTP DATA phase to send specially crafted content afterward. This content may be processed and delivered, yet not show up in server logs or match the sender’s original submission. Exim 4.100.1 corrects this by ensuring proper detection of the end of the DATA phase even after a rejection.
Exim deployments with Proxy Protocol enabled are especially at risk. Servers using versions from 4.83 to 4.100 are affected for Proxy Protocol flaws; GnuTLS-related vulnerability applies to versions 4.98-4.100 with specific settings. All administrators should obtain the signed 4.100.1 release via official channels, verify signatures and checksums, and update exposed systems immediately.
The threats include possible crash exploitation, leaked data, or undetected tampering. SMTP smuggling undermines integrity and auditing by creating discrepancies between submitted vs processed email content. Proxy Protocol flaws open dangerous windows for remote attacks if proxies are compromised or misconfigured.
Why this matters: Exim remains a cornerstone of email infrastructure on Unix-like systems. Its security and configuration shape how safely organizations handle incoming mail. These recent fixes demonstrate how important it is to harden protocol handling and reject paths to prevent subtle but exploitable vulnerabilities. Administrators should also scrutinize proxy setups and TLS configuration to minimize exposure. Keep an eye on any related advisories, and test updates carefully—especially where custom Proxy Protocol or GnuTLS configurations are in play.