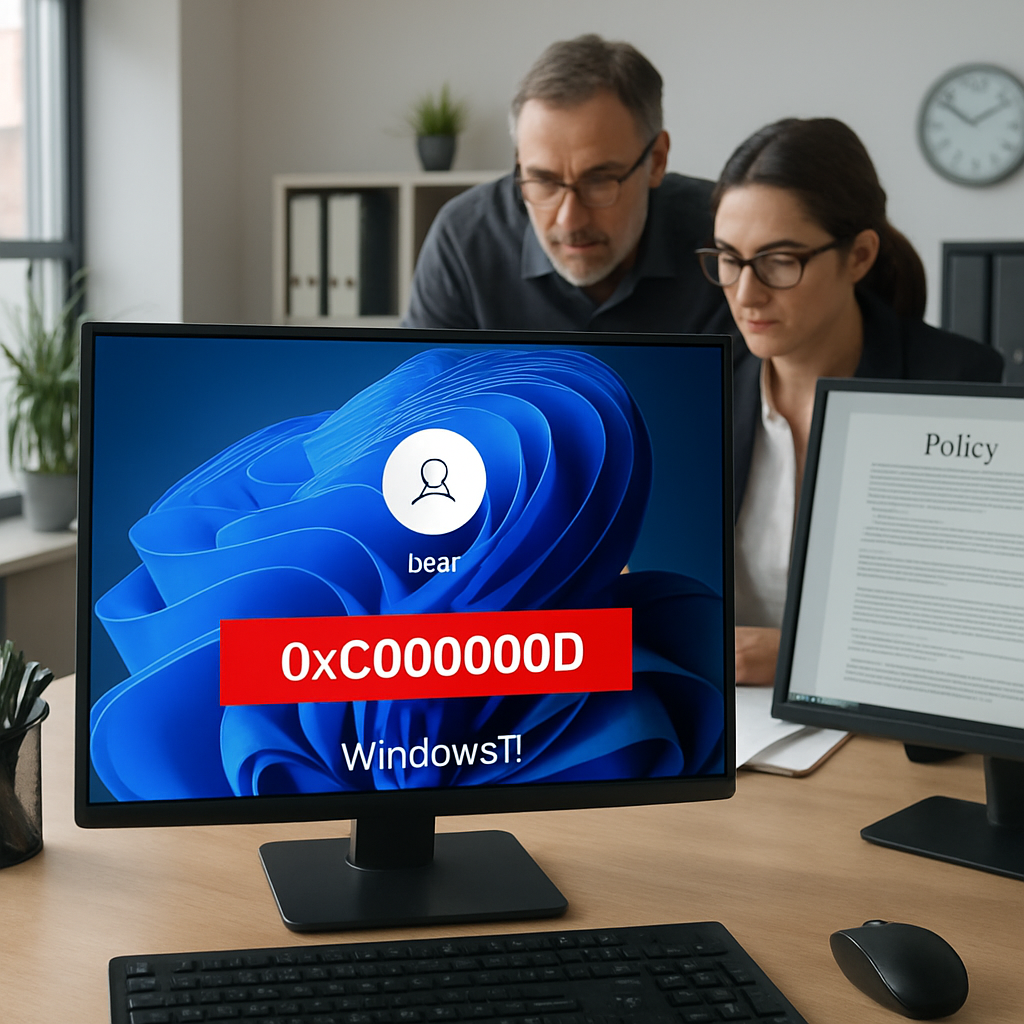
Microsoft has acknowledged a disruptive issue in Windows 11 caused by a non-security preview update released on September 22, 2026 (KB5124010). The patch breaks Remote Desktop Services for users whose computers are configured as remote hosts with Administrator protection enabled, specifically blocking non-admin users from accessing them. Connection attempts fail with error code 0xC000000Dand display a message about an invalid token. This problem does not affect Windows Server.
Which Systems Are Impacted?
The issue spans several Windows 11 versions: 24H2, 25H2, 26H1, and 26H2. Any remote host that has Administrator protection enabled, regardless of how the setting was modified, may block remote connections from non-admin accounts. Microsoft first reported the problem publicly on October 13 and labeled it “Mitigated” later that same day. It clarified that fixes issued for earlier credential prompt failures won’t resolve this particular bug.
What You Can Do Now
While Microsoft works toward a permanent resolution via a future update, IT teams have a temporary workaround. Organizations can disable Administrator protection on affected Remote Desktop hosts using Group Policy or Microsoft Intune by adjusting the “User Account Control Type Of Admin Approval Mode” policy. Doing so restores connectivity for non-admin users. Administrators are cautioned to apply this only to impacted machines and to document these changes carefully, as it involves removing an added security control.
This problem is especially painful in enterprise environments, where Remote Desktop hosts under central management often rely on strict administrative controls for security compliance. The broken functionality frustrates end users who need remote access and imposes additional burdens on IT support teams to triage and temporarily loosen security settings without exposing systems to elevated risk.
Microsoft advises organizations to check which updates are installed, verify whether Administrator protection is active on remote hosts, and inspect logs for the 0xC000000D error to identify affected systems. For affected devices, disable Administrator protection only as a stopgap measure, apply strict oversight, and await the promised fix in an upcoming Windows update.
Analysis:In its goal to improve OS security, Microsoft introduced Administrator protection to limit elevated permissions. But this builds tension: tightening security often means new regressions emerge—as is the case here. For organizations that prioritize both secure default settings and reliable remote access—especially hybrid or remote-first workplaces—this issue underscores the challenge in balancing protection with usability. Going forward, what to watch for is how swiftly Microsoft delivers the permanent patch, and whether its new change appears in accepted baselines without breaking core admin workflows again. Administrators should also monitor for similar side effects anytime complex policies like Administrator protection are enabled systemwide.