Researchers have uncovered a new zero-day vulnerability in Windows 11, dubbed “FastUnlock,” that enables someone with physical access to a PC to run code without signing in. Although BitLocker encryption remains intact and protected when the device is powered off, FastUnlock circumvents protections while the system is running and unlocked. This affects Windows 11 version 26H2 with the November 2026 security updates applied.
How FastUnlock Works and What’s at Risk
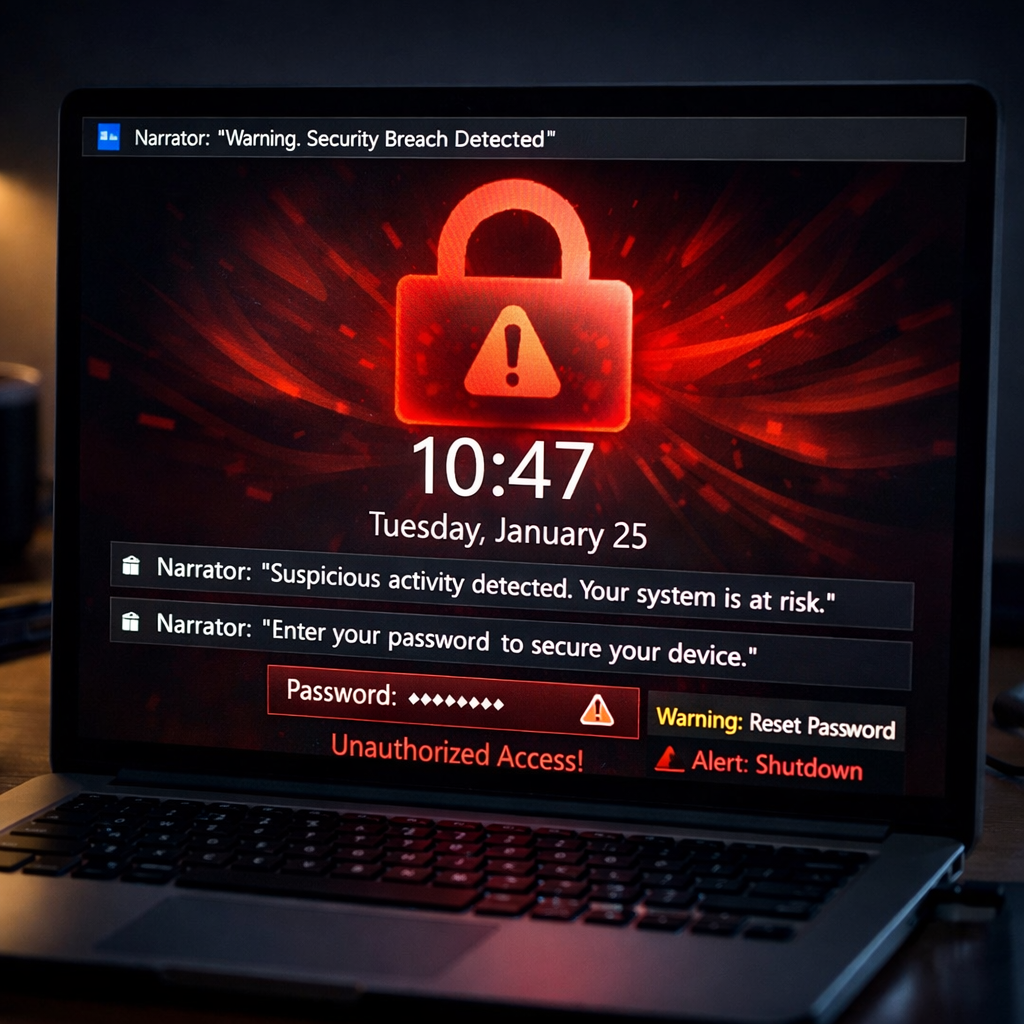
FastUnlock exploits Microsoft’s Narrator, the built-in screen reader that’s permitted at the lock screen. The issue arises during the account recovery interface, where Narrator is able to reach beyond the lock screen boundary and access elements that should remain restricted until a user signs in. That ability allows the attacker to execute code under the WsiAccount, a Windows account available at the lock screen. This account isn’t privileged, but the breach still allows code execution without authentication.
The vulnerability doesn’t allow decrypting BitLocker-protected drives or gaining full admin control—at least not directly. The flaw matters once the system drive is unlocked during normal operation. With BitLocker securing data at rest, Windows permissions and the lock screen become the next line of defense. FastUnlock undermines that shield by letting attackers bypass some lock screen controls, though it does not break BitLocker encryption itself.
Who’s Affected & Workarounds
FastUnlock requires physical access and at least one user account linked to a Microsoft online account. So if your Windows 11 PC is shut down, FastUnlock won’t help an attacker decrypt data—BitLocker remains effective there. However, devices in sleep, hibernation (without a startup PIN), or those left running and locked are vulnerable.
Microsoft’s existing guidance includes pairing the Trusted Platform Module (TPM) with a startup PIN. That setup ensures that BitLocker-protected drives remain locked until the PIN is entered—protecting devices that power on or resume from hibernation. Device owners are also advised to shut down systems completely when unattended, rather than relying on sleep, which doesn’t enforce a startup PIN and retains unlocked drives in memory.
As of November 20, 2026, Microsoft has not released a specific advisory, fix, or CVE for FastUnlock. No attacks exploiting this flaw have been publicly documented yet. Until a patch arrives, limiting physical access to unlocked devices is the most practical protection.
BitLocker has previously been bypassed by other flaws, including CVE-2026-97015 and CVE-2026-119832, but these are separate and unrelated to FastUnlock. FastUnlock’s novelty lies in its targeting of the already unlocked system, not the startup or recovery environments that past vulnerabilities attacked.
This discovery highlights ongoing challenges in locking down physical access attacks in Windows. Even with disk encryption in place, the system’s interface layers—lock screen, screen reader tools, recovery workflows—can open unexpected paths for exploitation. This vulnerability underlines the risk of relying solely on encryption without considering what happens once the system boots and resumes operation. Administrators, security teams, and users should follow Microsoft’s best practices—use startup PINs, fully shut down machines, avoid relying on sleep mode—and watch closely for the upcoming patch or advisory.