Cyber Asset Attack Surface Management (CAASM) tools are emerging as a critical defense layer. With every security tool owning its own notion of “asset,” organizations often struggle with inconsistent inventories. CAASM platforms aggregate data across EDR, MDM, cloud, identity, scanning tools—merge duplicates, surface what’s missing, and enable gap-based queries like “internet-exposed hosts missing EDR.” The 2026 CAASM rankings spotlight which platforms lead and in what areas.
Top Performers & What They Excel At
1. Axonius earns the top spot for connector-aggregation, setting the standard with hundreds of integrations, strong deduplication, fast gap-query responses, and workflows that turn findings into actions. Its merge accuracy and enforcement pipeline stand out, though prices reflect its premium positioning. The platform misses only when your connector mix diverges from its catalog.
2. JupiterOne shines for its graph-based asset model. It treats your environment—assets, policies, identity, relationships—as a graph, enabling powerful queries that dig into how hosts, data, and controls interrelate. Excellent for cloud-native estates; the graph approach can require organizational buy-in and learning curve.
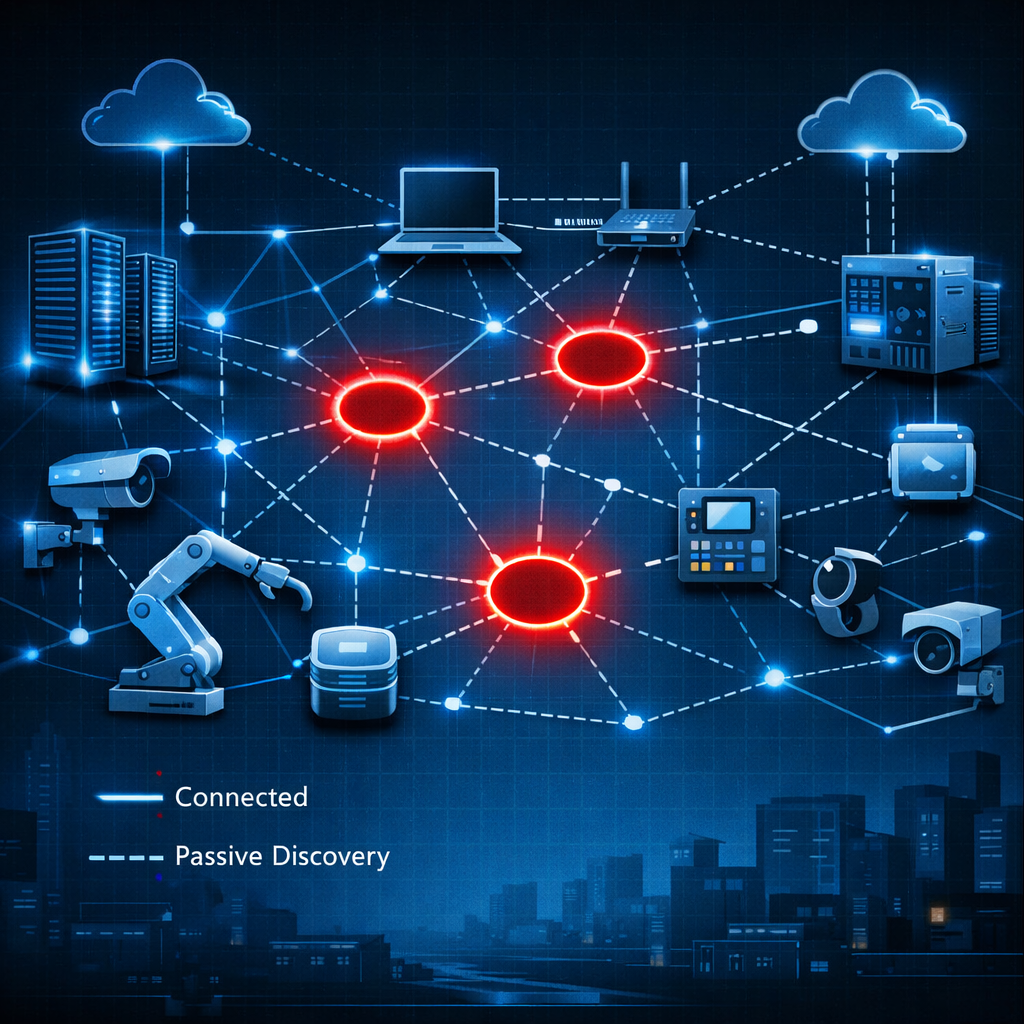
3. runZero leads in discovery-native truth. Where connectors and existing tools leave gaps, runZero’s mix of active and passive network discovery uncovers unmanaged, unagented, or forgotten assets. Especially valuable in complex environments with legacy or OT/IoT devices.
4. Armis focuses on unmanaged/IoT/OT risk. It excels at passive device intelligence, behavioral profiling, and bringing visibility to medical or industrial fleets where agents reach only so far.
5. Sevco Security emphasizes transparency in correlation: every merged asset carries traceability back to source tools, verification of coverage gaps comes with evidence—appealing for teams that distrust black-box merging.
6. Qualys CSAM utilizes its own sensor and scanning tools to build an asset inventory, making it compelling for organizations already invested in the Qualys ecosystem. It offers cleanup of unmanaged assets and merges external surface visibility—but its strength hinges on internal sensor reach.
7. Lansweeper remains a favorite for mid-market budgets. A mature IT discovery platform with agentless scanning, it balances depth and cost. Its emerging OT modules and longstanding hardware/software inventory capabilities make it a value lane choice.
8. Panaseer takes a specialized direction: controls-assurance metrics. Rather than just what assets exist, it shows what percentage of estate controls are implemented, tracking evidence over time for audits, board reports, and regulatory compliance.
9. Noetic Cyber marries graph-modeling with automation. It doesn’t just map relationships—it builds tickets or remediation workflows when gaps emerge, leveling up from visibility toward active resolution automation.
10. Balbix integrates risk quantification into its asset view. Every asset is paired with likelihood-to-breach and business-criticality weight, putting exposure into monetary terms. Not all operational queries are as strong, but its value comes in risk-aware prioritization.
How to Choose the Right CAASM Tool
Tools in this space tend to fall into two camps: connector-aggregators (e.g. Axonius, JupiterOne, Sevco) that combine what existing systems know, and discovery-native engines (e.g. runZero, Armis, Lansweeper) that find what tools miss. Most organizations need elements of both to close visibility gaps.
Evaluation pilots should begin with your own data exports. Test merge accuracy with real asset examples, look for over-merging and under-merging, and assess whether gap queries return correct results. Define high-value queries upfront—such as unencrypted devices in production, or hosts no EDR—and run them across candidates to compare.
Connector availability matters; getting read access to EDR, identity, MDM, and cloud tools often means navigating internal approvals. Prioritize connectors by value. Also, clarify whether the CAASM tool becomes your operational master inventory (CMDB-adjacent or replacing), and establish internal workflows to route gaps as owned tickets with SLA goals. Metrics like “coverage-gap count” trending downward quarter after quarter make renewal decisions easier.
In summary, deciding which CAASM tool fits comes down to what your tools already cover, what they miss, how much automation you want, and what you value most: transparency, metrics, risk, or discovery. These rankings reveal the current leaders, but the right choice depends on your environment and priorities.
What This Means Going Forward
This year’s rankings sharpen the distinction between surface visibility and relationship intelligence, risk awareness, and control assurance. CAASM is maturing beyond just collecting asset lists—it’s about closing visibility gaps fast, building trust in merged data, and empowering security teams to act rather than just observe. Expect greater emphasis on automated remediation, completeness of IoT/OT discovery, and tools that can quantify exposure financially. Going into 2027, organizations that adopt CAASM with clarity around what counts as “truth” will step ahead in cybersecurity resilience.