A sophisticated cyber-espionage campaign tied to Chinese-linked threat actors is abusing popular websites to deceive users into installing a backdoor dubbed Sparrow via fake Chrome SSL certificate warnings. The operation, named SilentDelivery, targets high-profile organizations across Europe and Asia, including government, shipping, research, and IT sectors, using social engineering and site compromise instead of exploiting browser vulnerabilities.
How SilentDelivery Works
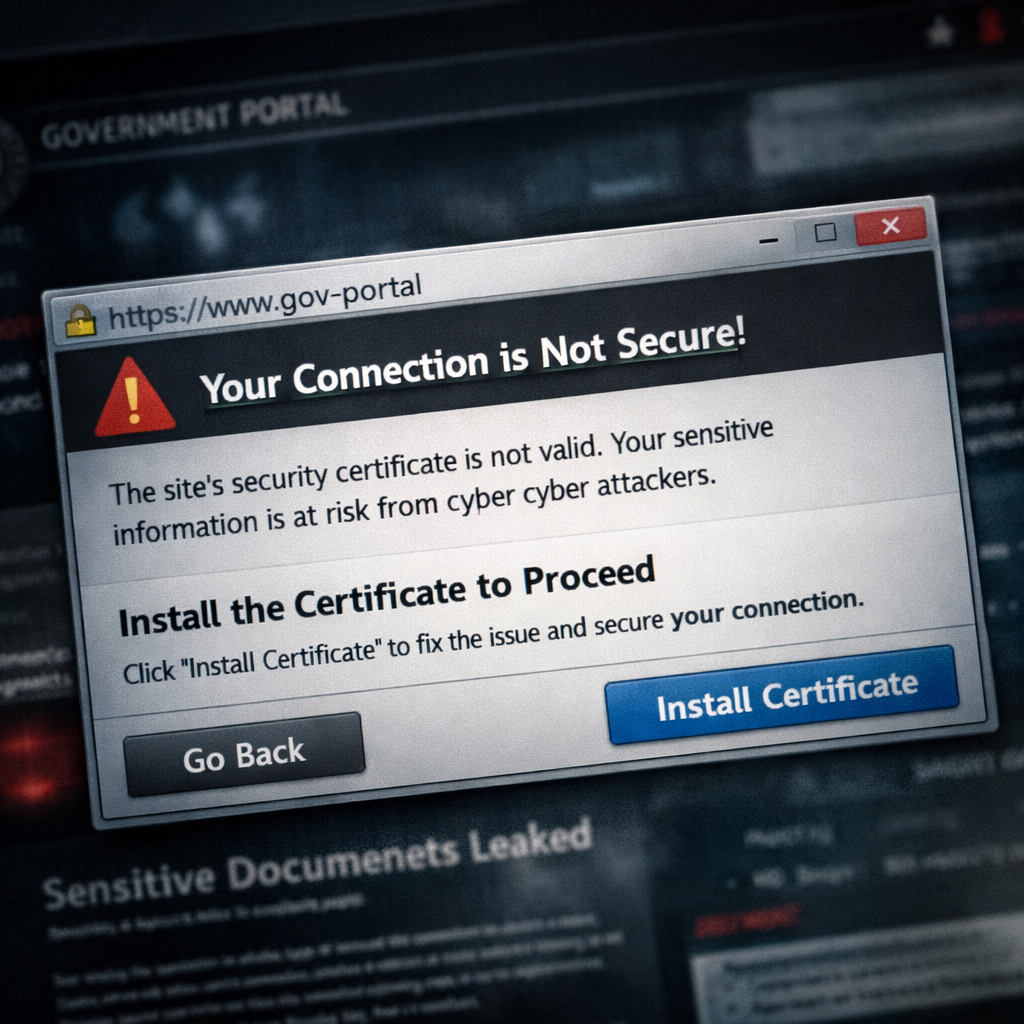
Visitors to compromised sites are confronted with a forged Chrome SSL certificate warning, crafted in their language. The false alert urges them to click “Install certificate,” claiming it will repair the connection—when in reality it launches a malicious Windows Installer package. This installer deploys a backdoor called SquadC, previously undocumented, and at times employs a variant of SparrowDoor. These tactics echo earlier malware distribution campaigns disguised as browser updates, but this one frames itself as certificate repair. SilentDelivery incorporates geo- and OS-based checks, custom to each target, to ensure the fake warning only appears to selected visitors. Once the backdoor installs successfully, subsequent visits load the legitimate page, reinforcing the illusion that everything’s been restored.
The Broader Malware Ecosystem
Researchers link SilentDelivery to a wider set of espionage tools collectively referred to as the Sparrow framework, which includes malware like SparrowDoor, SparrowShell, and clusters tied to names like FamousSparrow, Earth Estries, TropicTrooper, and UAT-9244. A central entity known as CopperDragon appears to supply these tools to various operators. Overlaps in code, reused certificates, and shared infrastructure suggest cooperation or shared resources rather than a single monolithic group. The campaign isn’t limited to Windows; Linux systems have been caught up in related clusters, for example via SparrowShell, where attackers focused initially on Linux hosts before shifting to Windows in certain cases.
Indicators & Recommendations
The attack chain involves several telltale signs. JavaScript injected into compromised sites uses services like jsjiami to obfuscate its true purpose, and backdoor loaders run multi-stage processes designed to avoid detection. Observed behavior includes fingerprinting visitors’ operating system, checking for virtual machine artifacts, and only delivering the malicious content if the visitor matches criteria. Enumerated Indicators of Compromise (IoCs) include multiple SHA-256 hashes for installer and loader binaries, as well as domains and IP addresses linked to the campaign.
Defenders are being warned to treat unexpected certificate-repair offers as serious risks, not browser branding. There’s no evidence of vulnerabilities in Chrome itself so far—this is a social engineering attack. Investigations should look for related phishing vectors too: in one case attackers delivered SquadC using a malicious shortcut inside an archive. Cross referencing the published IoCs can help in detection.
This is a refined campaign combining selective targeting, infrastructure reuse, and deception to break into sensitive environments. You should verify any certificate fix prompt, check URLs carefully, and ensure endpoint protection tools inspect unexpected executable downloads. Monitoring downloads, memory processes, and network activity tied to the listed domains and IPs gives security teams the best chance at catching the intrusion early.
Analysis: Why This Matters
SilentDelivery illustrates how far threat actors are willing to go to exploit trust. Rather than relying on zero-day browser flaws, they abuse routine behavior—SSL warnings—to trick users into sieving their own defenses. In high-stakes environments like government or research, that’s especially dangerous: one click can mean full remote access.
The campaign’s structure suggests a growing trend toward modular toolchains and shared services in cyber warfare, where groups like CopperDragon serve as infrastructures and kit providers. That complicates attribution, obfuscates attacker goals, and makes defense harder—because you’re not just defending against one adversary, but a toolkit that multiple groups can use.
What to watch: whether SilentDelivery expands to target other regions or sectors, how the Sparrow clusters evolve (especially for Linux vs Windows), and whether security vendors spot new variants that bypass current detections. For organizations, vigilance over certificate prompts, downloads, and domain name threats isn’t optional—it’s imperative.