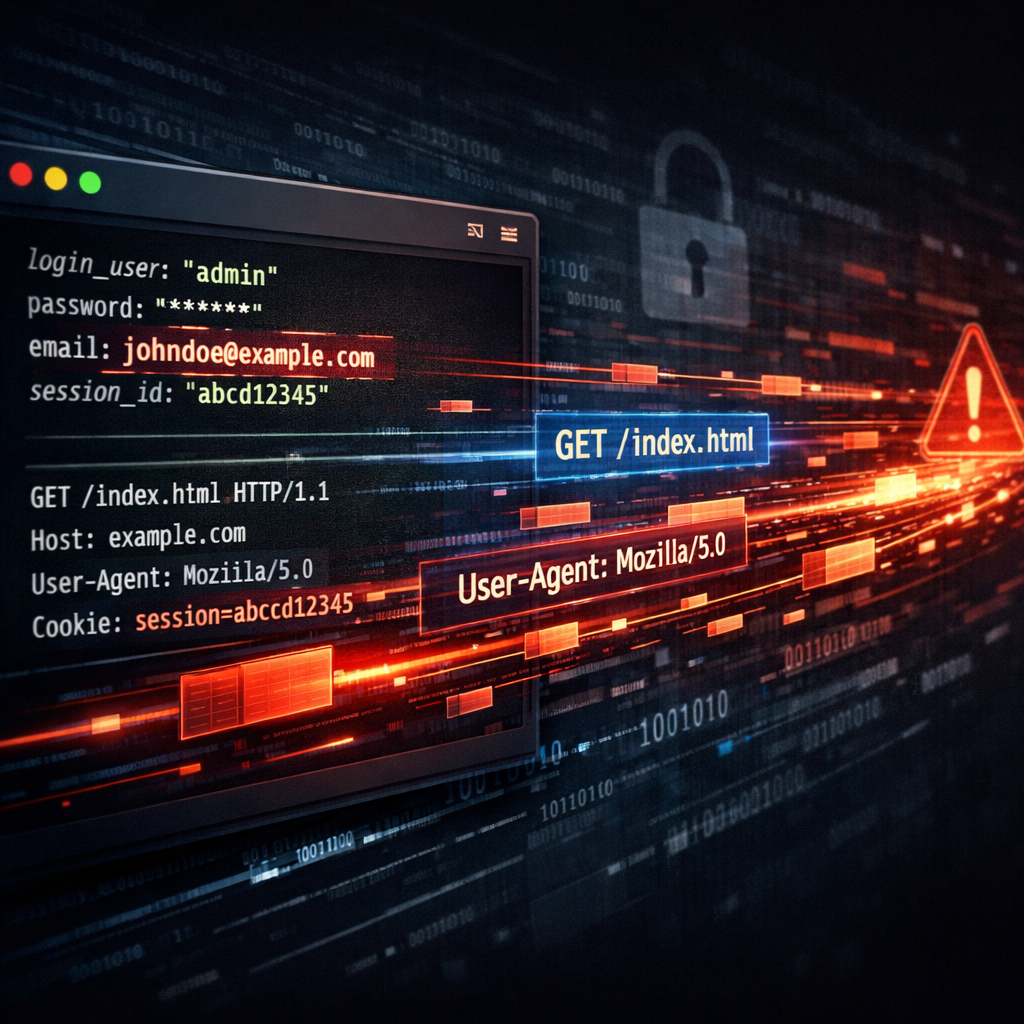
Anthropic’s code-writing assistant, Claude Code, has come under scrutiny after reports revealed it might leak users’ email addresses to external websites via HTTP User-Agent headers. A GitHub issue opened November 5, 2026 claims that while performing web searches, Claude Code version 2.1.318 running on macOS inside tmux sent the user’s email within the User-Agent header—information that may be accessible to the sites being queried.
The report was filed by a GitHub user going by taylor-edwards. The user said that after using Claude Code, they began receiving dozens of phishing or scam emails daily. While they believe these messages are tied to the alleged leak, the issue does not include a captured HTTP request, full examples of headers, or definitive reproduction steps. Additional users chimed in, saying they noticed similar patterns, though no conclusive evidence shows every user is affected.
What Went Wrong
The core problem lies in how HTTP User-Agent headers work: they tell a website what software is making the request. In this case, because Claude Code was instructed (possibly by its internal model logic) to write commands like “curl,” it used an email address found in its internal context as the “contact” part of the User-Agent. That means when connecting to third-party sites, the user’s email could be included, even if users didn’t explicitly ask for that.
Anthropic appears to have introduced a mitigation in versions 2.1.317 and later: a module called cc-plugin-privacy, which is enabled by default and meant to block inclusion of email addresses in User-Agent headers. But users report mixed experiences. Some didn’t find the module at all; others ran simple local tests feeding their own email via model context and saw User-Agent output including it, with no blocking. Whether that means the module isn’t working correctly, or that not all leaks are stopped, remains unclear.
What’s Being Done—and What Remains Risky
A representative from Anthropic reportedly acknowledged that account-linked email addresses would be removed from model context in a forthcoming update, admitting that current protections are imperfect. Meanwhile, the GitHub issue remains open as of November 6, 2026, suggesting don’t-yet resolved concerns.
The incident adds to a growing body of evidence that AI agents—and coding assistants in particular—may fail to adequately protect sensitive user data when automating web or network operations. Earlier leaks and bypasses of security rules in Claude Code have raised similar red flags, especially around how model behavior is constrained in theory versus practice.
What Users Should Do Now
Anyone using Claude Code—or similar tools—should audit any agent-written network commands that might expose data. Disable or verify the behavior of privacy-related plugins, and avoid placing personal information in contexts that get passed to lower-level operations like HTTP requests. Ultimately, users should ensure that safeguards are more than configuration flags—they need to be demonstrably effective.
Final Thoughts
This isn’t just a software bug—it’s a governance issue. AI assistants are becoming more deeply integrated into development workflows, handling code, networking, and potentially private data in automated ways. If users cannot trust that their tools won’t “leak” identifying information because of hidden behaviors or defaults, adoption could be slowed, and users could be exposed to phishing, data theft, and loss of trust.