Microsoft is set to introduce a new Security Detection Report within the Teams admin center, aiming to provide administrators with a centralized tool to monitor and manage messaging-based threats across their organizations.
Consolidated Threat Monitoring
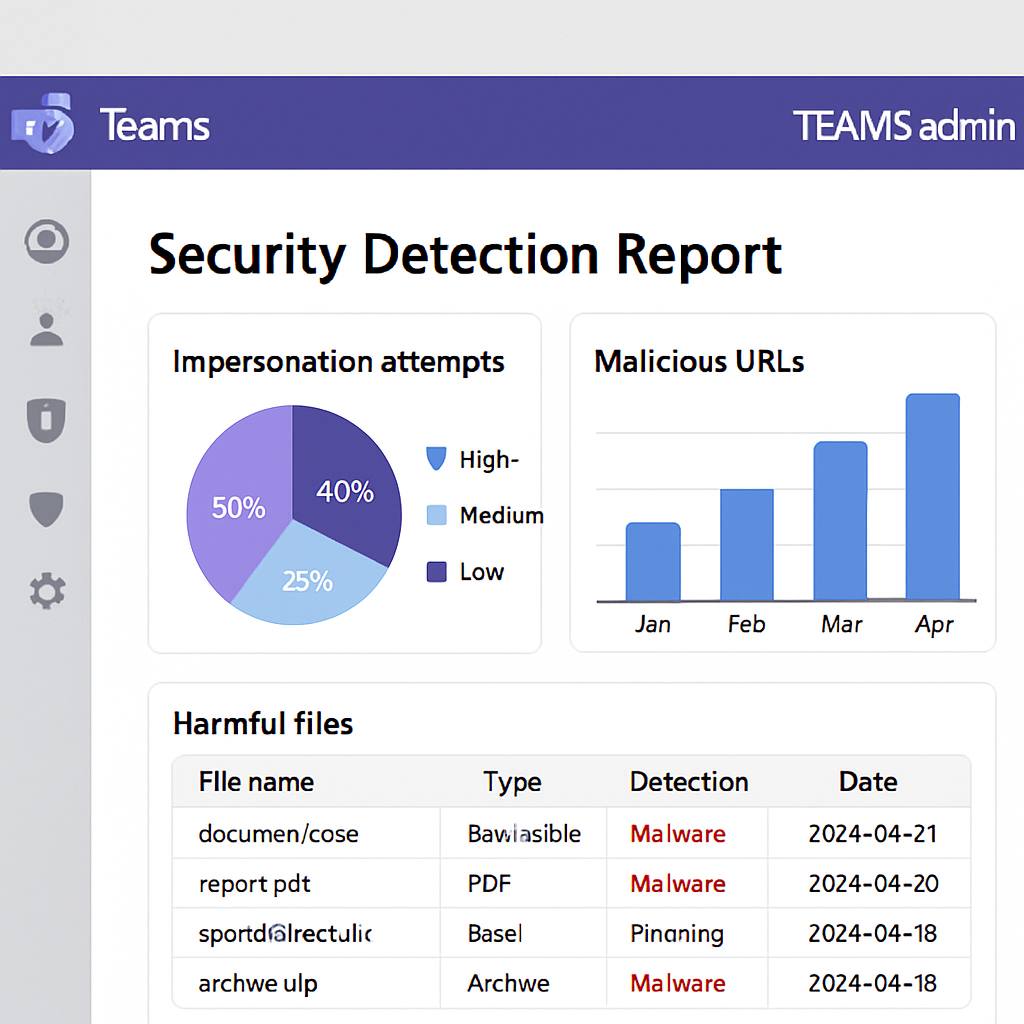
Traditionally, administrators have had to navigate multiple tools to track various threat signals within Teams. The upcoming Security Detection Report addresses this challenge by integrating key threat categories—such as impersonation attempts, malicious URLs, and potentially harmful file types—into a single, comprehensive dashboard. This consolidation is designed to streamline the detection and response process, enabling security teams to identify and mitigate threats more efficiently.
Enhanced Reporting Features
Located under Analytics & Reports > Protection Reports > Security Detections in the Teams admin center, the new report offers both visual and detailed data representations. Administrators will have access to charts displaying detection volumes over specified date ranges, alongside tables that provide in-depth information on individual detections. Each entry includes critical context, such as sender and recipient details, detection types, and thread identifiers, facilitating thorough investigations.
To support further analysis and compliance requirements, the report includes export functionality. Administrators can download summaries and detailed records in CSV format, allowing for integration with broader security information and event management (SIEM) systems or for documentation purposes during audits.
Proactive Threat Mitigation
One notable feature of the Security Detection Report is the ability to take immediate action against identified threats. For instance, administrators can block malicious external users directly from the report via External Access settings. This capability reduces the time between threat detection and containment, enhancing the organization’s overall security posture.
Rollout Timeline and Considerations
The rollout of this feature has experienced several adjustments. Initially slated for mid-July 2026, the release was postponed to late June, with the most recent update indicating general availability starting in late August 2026. A global rollout is expected to conclude by early September 2026 for standard multi-tenant customers. These timeline revisions suggest that Microsoft is diligently refining the detection logic and reporting infrastructure to ensure optimal performance upon release.
Addressing Evolving Threats
As Microsoft Teams continues to be a central platform for enterprise collaboration, it has increasingly become a target for cyber threats, including phishing attacks, malicious link distribution, and file-based malware. The introduction of the Security Detection Report provides administrators with a dedicated tool to monitor and respond to these threats directly within the Teams environment, addressing a previously identified visibility gap.
This development complements other security enhancements, such as user-reported security signals, which allow end users to flag suspicious messages directly within Teams. These reports feed into the Protection Reports section, contributing to a more comprehensive security framework.
Organizations are encouraged to review and enable malicious link and file scanning settings under Messaging Safety. Additionally, updating investigation protocols to incorporate Teams as a primary signal source will be essential once the Security Detection Report becomes widely available.
The introduction of the Security Detection Report signifies Microsoft’s commitment to enhancing the security capabilities of Teams. By providing administrators with a centralized, efficient tool for threat detection and response, organizations can better safeguard their communication channels against evolving cyber threats.