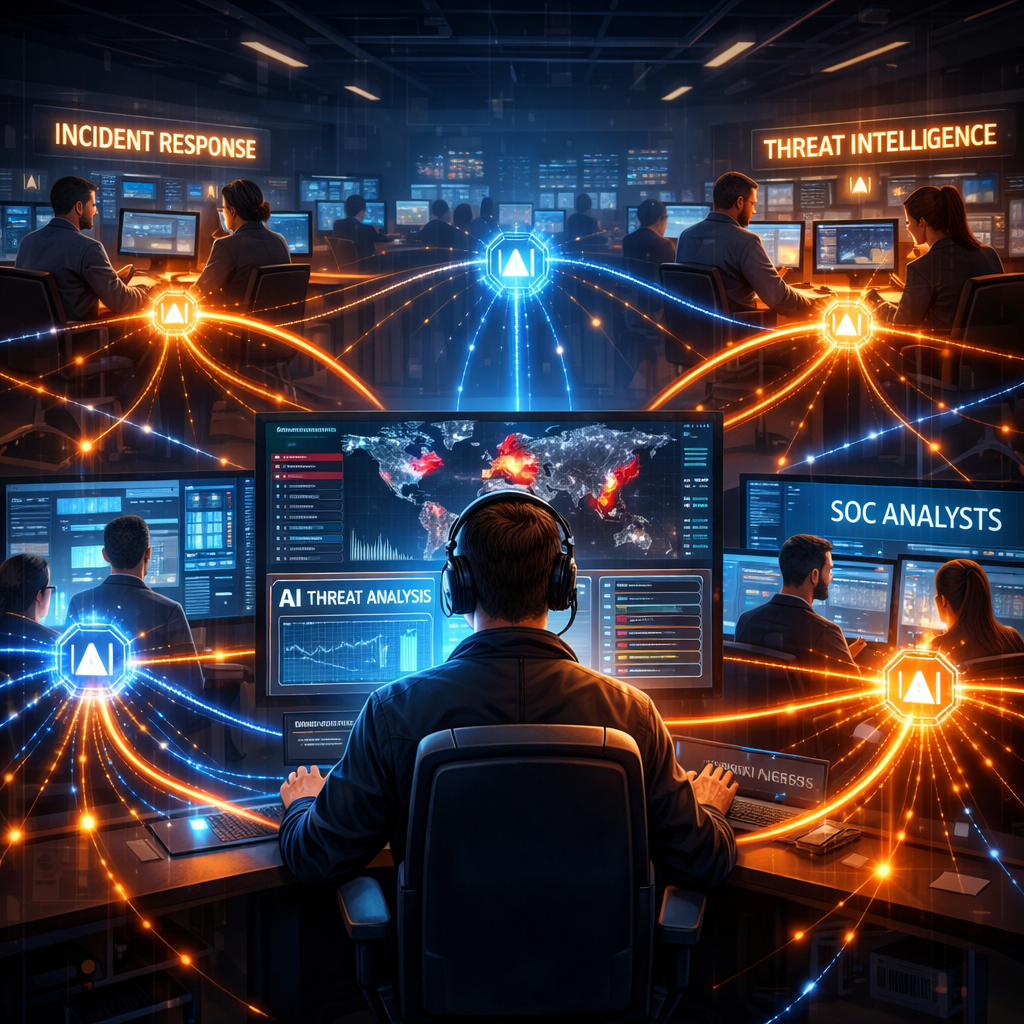
AI is rapidly transforming cybersecurity operations by automating many tasks that once defined the job of security analysts—things like investigating alerts, gathering evidence, correlating across tools, and executing responses. As these AI capabilities mature, Security Operations Centers (SOCs) are preparing for fundamental changes in workflow, decision-making, and job expectations. A new role is emerging: the Threat Operator.
What Is a Threat Operator?
The Threat Operator is envisioned as an AI-native security professional who oversees the defense across the entire security lifecycle. Instead of reacting to individual alerts, this role focuses on high-level priorities—translating business risk into defensive strategy, guiding AI-driven workflows, and applying judgment to the decisions made by automated systems.
Traditionally, SOCs have consisted of specialized teams: threat intelligence researchers, detection engineers, threat hunters, alert analysts, and incident responders. These groups often work in silos, passing tickets and findings between distinct tools and systems. With AI, those workflows can become more cohesive—agents might take intelligence about a new vulnerability, convert it into hypotheses, generate detection rules, monitor for suspicious activity, and even recommend responses—all while maintaining context between stages.
Unlocking New Skillsets and Career Trajectories
As AI automates many of the repetitive, process-driven tasks that junior analysts typically perform, organizations must rethink how they train and grow talent. The classic path—tackling simple alerts, learning investigation tactics, then stepping up to handle complex incidents—may no longer suffice. Unless structured learning and mentorship programs are built, it could become harder to develop seasoned security leaders.
A Threat Operator role allows newer professionals to bypass the narrow tunnel of alert review and instead gain exposure to a wide spectrum of security functions. They’ll learn how threat intelligence informs hunting, how detections are engineered, how investigations close gaps, and how response decisions impact the business. That exposure depends on investment in technical fundamentals—understanding networks, adversarial tactics, OS behaviors—which must be coupled with mentorship in evaluating evidence and making informed decisions when information is incomplete.
Key competencies for this role extend beyond tool-savvy and telemetry parsing. Threat Operators must excel in interpreting business risk, understanding the organization’s architecture and critical assets, knowing adversary behavior, and being able to govern AI workflows—deciding when AI should act autonomously, when to escalate, and how to measure effectiveness of responses.
For example, if an AI agent recommends isolating a compromised server, a Threat Operator has to weigh that recommendation against business impact. If the server supports a critical process, blind isolation could disrupt operations. Understanding those trade-offs is central to the job.
From Junior Roles to Senior Leadership
Early-career Threat Operators will concentrate on reviewing AI-generated findings, validating evidence, adding environmental context, and seeing how decisions ripple across defensive operations. As they progress, they’ll shape strategy—defining defensive priorities, identifying detection gaps, setting escalation paths, and dictating AI autonomy where safety allows.
Senior Threat Operators will handle oversight of AI behavior, establish policies around actions that carry high risk, evaluate reliability of decisions from agents, and measure how well security operations are reducing business exposure. Those moving into this path might come from threat intelligence, incident response, detection engineering, risk roles, or architecture—bringing varied expertise into a role that spans the full security lifecycle.
Organizations should begin preparing now. That means defining which decisions need human approval, establishing oversight and governance models, determining how AI-generated evidence is validated, mapping permissible autonomy, and revising performance metrics. Success will increasingly be measured not just in response times or ticket throughput, but in coverage of threats, risk reduction, and effectiveness of defensive decisions.
This shift won’t happen overnight. Different organizations will adapt at different speeds, depending on maturity, risk profile, and tolerance for automation. But one thing is clear: the SOC of the future won’t just train people to use tools—it will develop practitioners who can operate the defense itself.
Analysis: The emergence of the Threat Operator role is more than a job title—it’s a signal that cybersecurity is entering an age of operational transformation. As agentic AI takes on tactical tasks, strategic thinking, risk understanding, and oversight become the true competitive edge. Organizations that invest in training, governance, and cross-functional mindset now will be better equipped when autonomy—and accountability—becomes non-negotiable.