Researchers have uncovered a sophisticated malware campaign targeting macOS users. The threat comes via a counterfeit Zoom installer that drops a backdoor dubbed CloudSyncD. Designed to steal login passwords and install hidden remote access tools, the malware leverages fake system prompts to trick users into granting elevated permissions. The danger lies not in exploiting OS bugs, but in deceiving users into overriding built-in safeguards. The first sample appeared on September 15, 2026; within days, multiple variants were found suggesting rapid development and planned rollout.
How the Attack Works
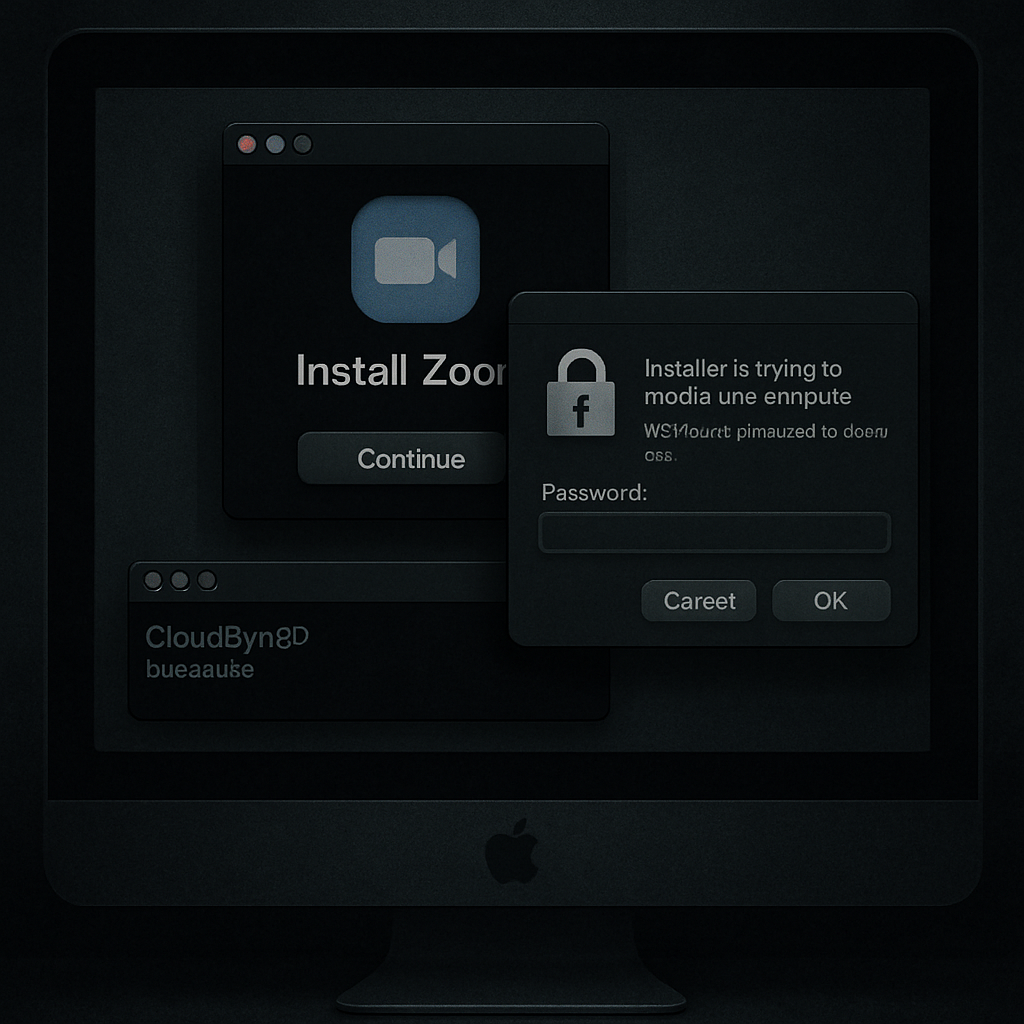
The attack begins with a disk image resembling Zoom’s installer. It shows a familiar layout: an application icon linked with an Applications folder shortcut. Background visuals guide users through a staged process, instructing them to open System Settings, navigate to Privacy & Security, click “Open Anyway,” and enter an administrator password. That sequence allows the malware to bypass Gatekeeper by relying on social engineering rather than technical exploit.
Once launched, a fraudulent authorization dialog requests the user’s password. If entered incorrectly, the prompt reappears until it accepts valid credentials. A fake download progress bar sustains the illusion of legitimate setup. The stolen password isn’t immediately transmitted; instead, it’s hidden in what appears to be a normal settings file. It’s embedded as a base64-encoded string among random content, with zero-width Unicode characters marking its position and length. After the password is captured, the installer attempts to run its backdoor payload. Because direct execution failed, it creates a temporary executable and uses the captured password to elevate privileges.
What CloudSyncD Can Do
The backdoor works on both Intel and Apple silicon Macs. On initial contact with its command-and-control server, it gathers basic system and network data including machine name, hardware identifiers, and operating-system version. Subsequent check-ins occur frequently—every eight to 16 seconds—sending only a hardware ID. The server can then issue encrypted tasks, delivered as standalone executables or compressed archives. These payloads are not run via a remote shell, but rather launched as new programs—a behavior that complicates detection without careful process monitoring.
Intriguingly, traffic to the malware’s command server is disguised to look like a request for a JavaScript library. The malware accepts any presented certificate, loosening potential hindrances. A consistent encryption key shared across live and development versions helps defenders to correlate different samples. Logs on compromised devices are encrypted but can contain device ID, server endpoints, and infection timelines. Researchers also noted that the password entered by the user is exposed in process arguments during local validation—a potential detection vector.
Some limitations were observed. So far, there’s no evidence the malware achieves persistence through reinfection or replaces existing applications. Also, no downstream payloads or confirmed losses have been observed. This suggests that CloudSyncD may still be in its deployment phase.
Defending Against It
To counter this threat, endpoint protection systems and web filters are crucial. Researchers recommend monitoring process arguments and looking for signs such as invisible Unicode characters in config files, unusual temporary payload patterns, or installers that prompt for system password following vague instructions. Blocking malicious domains and reporting similar behavior are also key. Indicators of compromise include specific SHA-256 hashes and command-and-control domains that masquerade as benign endpoints.
Understanding this attack means recognizing that many attacks no longer rely purely on exploits. CloudSyncD demonstrates how threat actors increasingly depend on social engineering and trust abuse—tricking users into bypassing macOS’s defenses. As defenses mature to fight known exploits, malware authors adapt tactics: fake installers, misleading dialogs, and OS configuration tricks to advance to privileged code execution. For Mac users and security teams alike, vigilance around any installer that behaves oddly—requests elevated permissions, prompts for password, or looks “off”—is the new front line. Be cautious before clicking “Open Anyway.”
Ultimately, CloudSyncD is a warning. It’s not about what’s broken in macOS—it’s about what can be twisted. Keeping Gatekeeper enabled, scrutinizing installer behavior, and maintaining strong detection tools will be essential to staying ahead of this type of threat.
What this means going forward: this campaign underlines a shift toward privilege-focused malware that uses deception more than technical exploits. As CloudSyncD may still be expanding, organizations need to update threat detection practices, educate users, and prepare incident response for attacks that don’t look like classic malware—but can be just as damaging.