GitHub Security Lab has uncovered 24 distinct vulnerabilities in Android apps using its Taskflow Agent—an open-source framework that automates security research workflows with AI assistance. Among the flaws are serious risks including covert location-tracking in the popular OsmAnd app and an account-takeover chain in Wikipedia for Android. These findings demonstrate how specialized AI taskflows can surface logic flaws that general scans often miss—though human review remains essential.
How the Taskflow Agent Works
Rather than using broad prompts on massive repos, researchers built Android-specific taskflows that break audits into discrete stages. One phase identifies ‘entry points’ unique to Android—exported activities, services, broadcast receivers, deep links. Next, each entry point is evaluated against known vulnerability categories like insecure intents, confused-deputy issues, unsafe broadcasts, WebView risks, and cross-app scripting. This two-step setup helps the model zero in on relevant code paths in repositories that mix mobile, web, and desktop logic.
Examples of Discovered Vulnerabilities
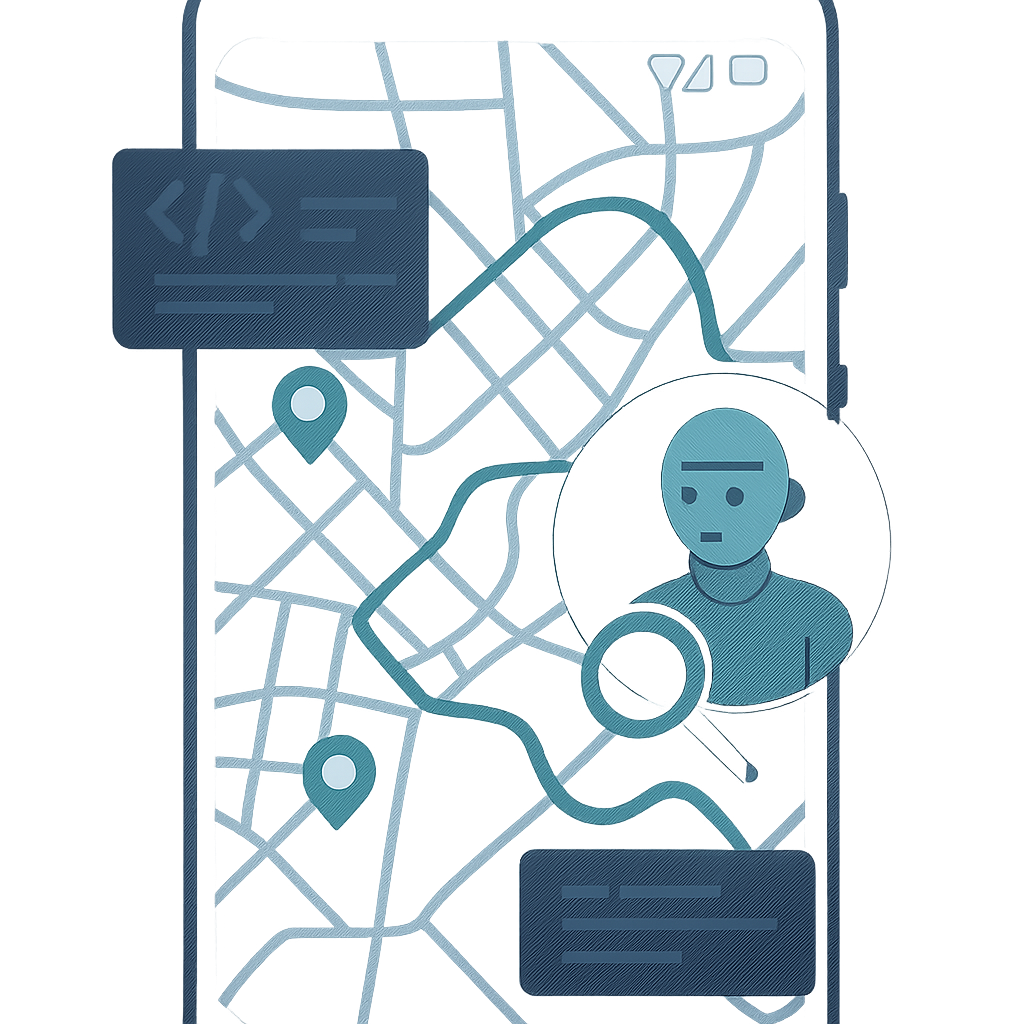
In OsmAnd—an Android navigation app with over 10 million downloads—one vulnerability involves an exported activity that accepts intent extras. Malware could trigger settings imports silently, replace configuration, or swap map tiles without user knowledge. That enables attackers to reroute map requests to controlled servers, log the victim’s location and paths, and even manipulate route origin/destination data, all while the app appears to operate normally.
The Wikipedia Android application was found to harbor an attack chain based on flawed deep-link handling. It uses a handler for “wikipedia://” URIs and validates hostnames via a suffix check—allowing domains ending with “wikipedia.org”, such as malicious “evil-wikipedia.org”, to slip through. Attackers can craft a webpage with such a deep link, getting users to open it, which loads attacker-controlled content into Wikipedia’s WebView. A second bug in cookie domain validation exacerbates the issue, potentially exposing user credentials, long-lived auth tokens, and session cookies. Together, these flaws can allow full account takeover across Wikimedia properties.
Strengths & Limitations
The approach shows clear advantages: it uncovers complex logical vulnerabilities and patterns beyond simple syntactic issues. But GitHub cautions that AI-generated results must be proofed by experts. Models may misjudge the severity of a flaw, fail to consider mitigating code elsewhere in the app, or generate false positives. Having the model produce proof-of-concepts helps with triage, but even then, nuanced human assessment is indispensable.
Also worth noting: running audits this way requires resources. Even medium-sized Android repositories can take an hour or more with many calls to premium-model AI. Output is stored in a SQLite table for researcher review. Use of the Taskflow Agent requires a GitHub Copilot license.
All workflows and the Taskflow Agent setup are publicly available, so developers can inspect or adopt similar auditing methods.
The Android-specific audit and the 24 vulnerabilities show that AI workflows are increasingly capable of rooting out mobile logic flaws that traditional tools often miss. Yet they also underscore that human scrutiny is still necessary. Teams should consider adopting AI taskflows like this—not as replacements for human review but as force multipliers. As more apps run sensitive logic client-side, detecting flaws early through structured workflows like GitHub’s Taskflow Agent could significantly raise the bar for mobile security. Watch whether these methods lead to industry-wide adoption or breed over-reliance that lets serious flaws slip under the radar.