Researchers have uncovered a malicious Zoom installer for macOS that evades Apple’s Gatekeeper protections using a convoluted installer design. It installs the real Zoom application—but slyly embeds an “infostealer” that captures user-entered data and transmits it to cyberattackers as often as every eight seconds.
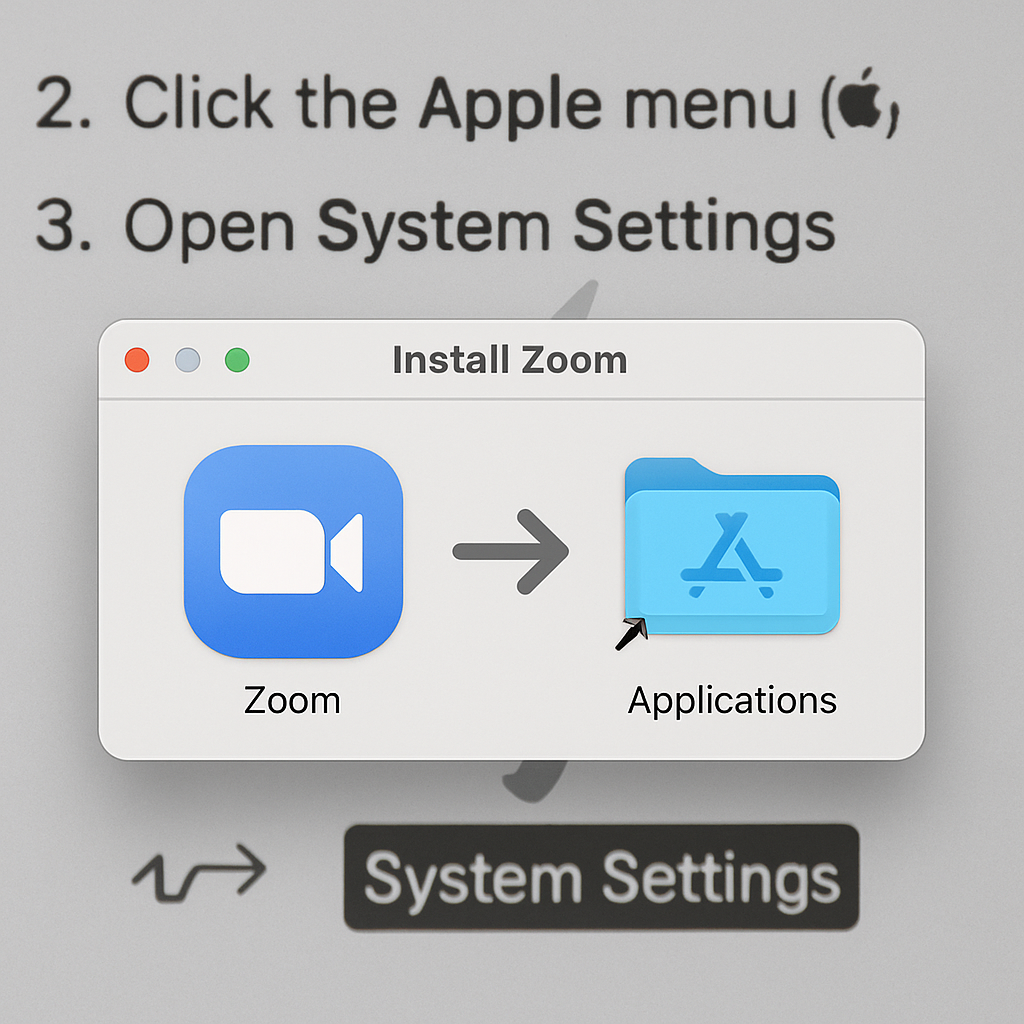
The threat, dubbed “CloudSyncD” by cybersecurity firm Jamf, is packaged as a disk image that poses as an ordinary Zoom installer. Users see a familiar layout: on one side the Zoom icon, on the other an alias pointing to the Applications folder. The catch: the disk image uses a background graphic with step-by-step instructions, urging users to open System Settings → Privacy & Security → scroll to the Security section and click “Open Anyway,” followed by entering an administrator password. These steps effectively allow the installer to bypass Gatekeeper’s default restrictions, which are meant to prevent unnotarized apps from running.
How the Installer Misleads Users
Normally, Gatekeeper blocks apps that haven’t been notarized by Apple. It allows bypasses only through deliberate user action, which typically involves manually overriding security settings. CloudSyncD simplifies this workaround by packaging instructions into its own installer background, making the illicit steps feel official.
Once active, the malware doesn’t just sit idle—it logs keystrokes and other sensitive input and sends data to the attackers’ remote server at high frequency, potentially exposing passwords, credit card numbers, or other private information.
Defensive Steps Mac Users Should Take
To guard against this kind of attack, users are advised to download software only from the official Mac App Store or the developers’ own websites. Users should resist prompts that advise bypassing Gatekeeper, even if they appear within what looks like a legitimate installer. Keeping macOS and all security tools up to date adds layers of protection.
CloudSyncD’s design underscores a bigger trend: malicious actors are becoming more creative in tricking Apple’s built-in protections. The use of UI deception—in the form of installer wallpapers and clear instructions—blurs the line between legitimate and harmful software. It serves as a reminder that many security breaches start with “one click and one password.”