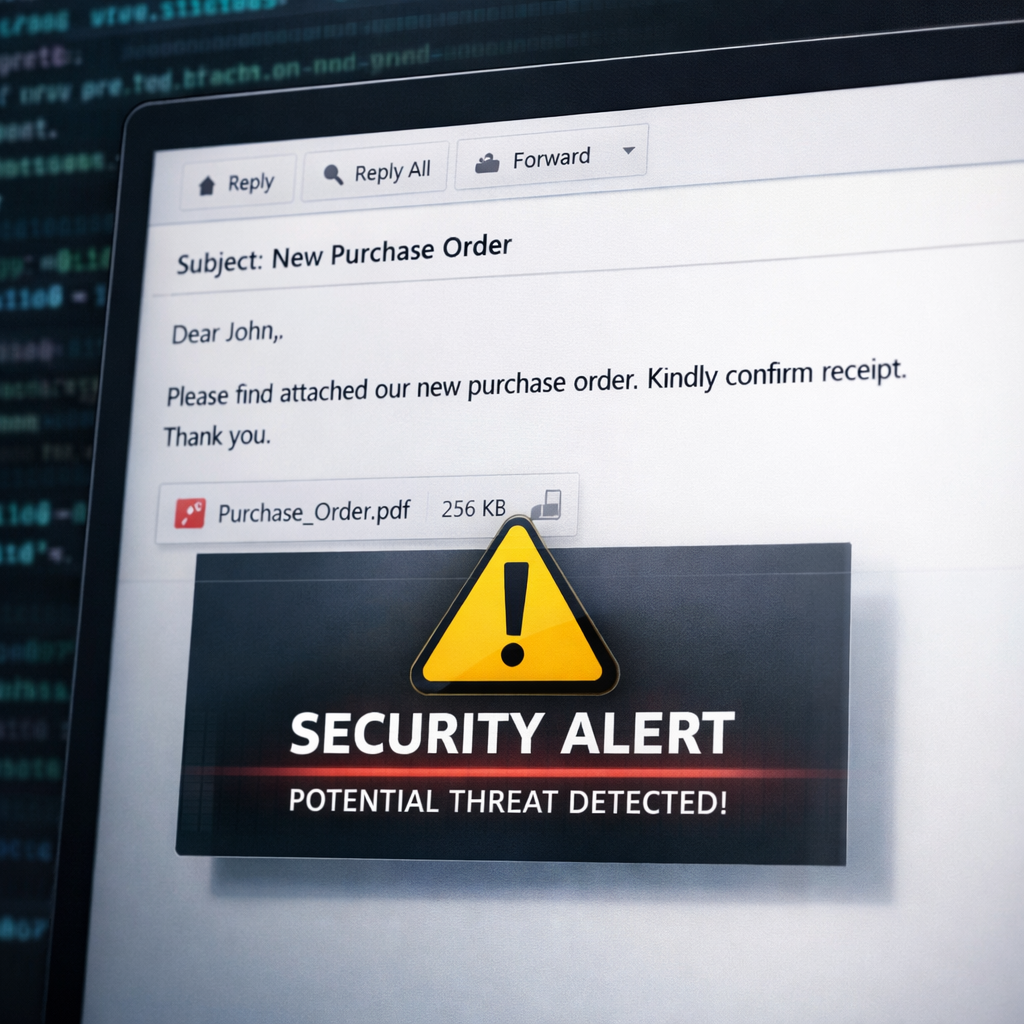
Cybercriminals have started using phony purchase order emails as bait to deploy XLoader, a potent information-stealing malware. The attack begins with what seems like a standard order confirmation, complete with large dollar figures and shipping details, but ends with hidden malicious payloads delivered via Word documents. The email includes a .docx attachment and uses familiar business language to lower recipients’ guard.
How the Attack Unfolds
The .docx attachment doesn’t contain the malware directly. Instead, it embeds a Rich Text Format (RTF) file through Word’s “Import Content from Another Document” feature, known as altChunk. This structure allows an embedded Microsoft Equation Editor object to exploit the old CVE-2017-11882 vulnerability, enabling execution of a Visual Basic Script (VBS) file dropped into the temporary folder.
Once triggered, that VBS launches a first-stage PowerShell script which handles an encoded payload. This data includes a loader, an encrypted payload, and a second script. A registry-based persistence mechanism ensures that the malware survives restarts, and XOR decryption is used so the final XLoader component runs purely in memory—making detection harder.
What XLoader Does and How to Defend
The end payload is an information stealer that harvests browser data and system details. Once inside, it can also pull in other malware, escalating risk. While the campaign didn’t identify the threat actors or confirm how many companies have been targeted, security researchers point out that keeping systems patched, especially Office and Windows components, is crucial.
Other recommended defenses include verifying suspicious purchase orders through trusted contacts, scrutinizing attachments, monitoring for Document-to-Script transitions, checking registry changes, and leveraging indicators of compromise. Sample IoCs include MD5 hashes of the malicious files, specific attachment names like “PORD051071.docx,” and registry keys such as entries under Run for persistence and script paths stored under HKCU.
This scheme shows how threat actors are combining old vulnerabilities with layered attack paths to bypass defenses. What seems like a mundane business document becomes the entry point for data theft and deeper compromise.
The use of purchase-order themed emails as lures isn’t new—earlier campaigns also used order emails to deliver XLoader. But this latest version is more complex with its multi-stage chain and use of an embedded RTF document to conceal its script stages, making it more dangerous.
For organizations, the stakes are clear: vigilance over email attachments, especially from unexpected senders, and fast patching are essential. Office setups left unpatched—even from old vulnerabilities like the Equation Editor issue—leave the door wide open.
Analytical note: This campaign highlights a growing trend of blending social engineering with technical sophistication. It’s not enough to train employees to spot suspicious emails; defenses need full visibility into malformed document behavior, script execution, and persistence. In short, detection needs to go deeper than the message—security operations, threat intelligence, and patch management must all work together tightly going forward.