Over the past few years, unpatched Qlik Sense Enterprise for Windows servers that are exposed to the internet have been repeatedly targeted by the Cactus ransomware group — also known under names like ZeroQlik or DoubleQlik. Cybersecurity researchers have tracked the attacks to three vulnerabilities (CVE-2023-41266, CVE-2023-41265, and CVE-2023-48365), each contributing to the compromising of business intelligence platforms often used for analytics and data reporting.
Attack Chain and Indicators
The intrusion typically begins with the path-traversal bug (CVE-2023-41266), which allows unauthenticated access to endpoints through manipulated directory paths. Once inside, attackers move on to tunnel HTTP requests using the other two flaws (CVE-2023-41265 and CVE-2023-48365), some of which were partially fixed, yet still bypassed by crafty adversaries.
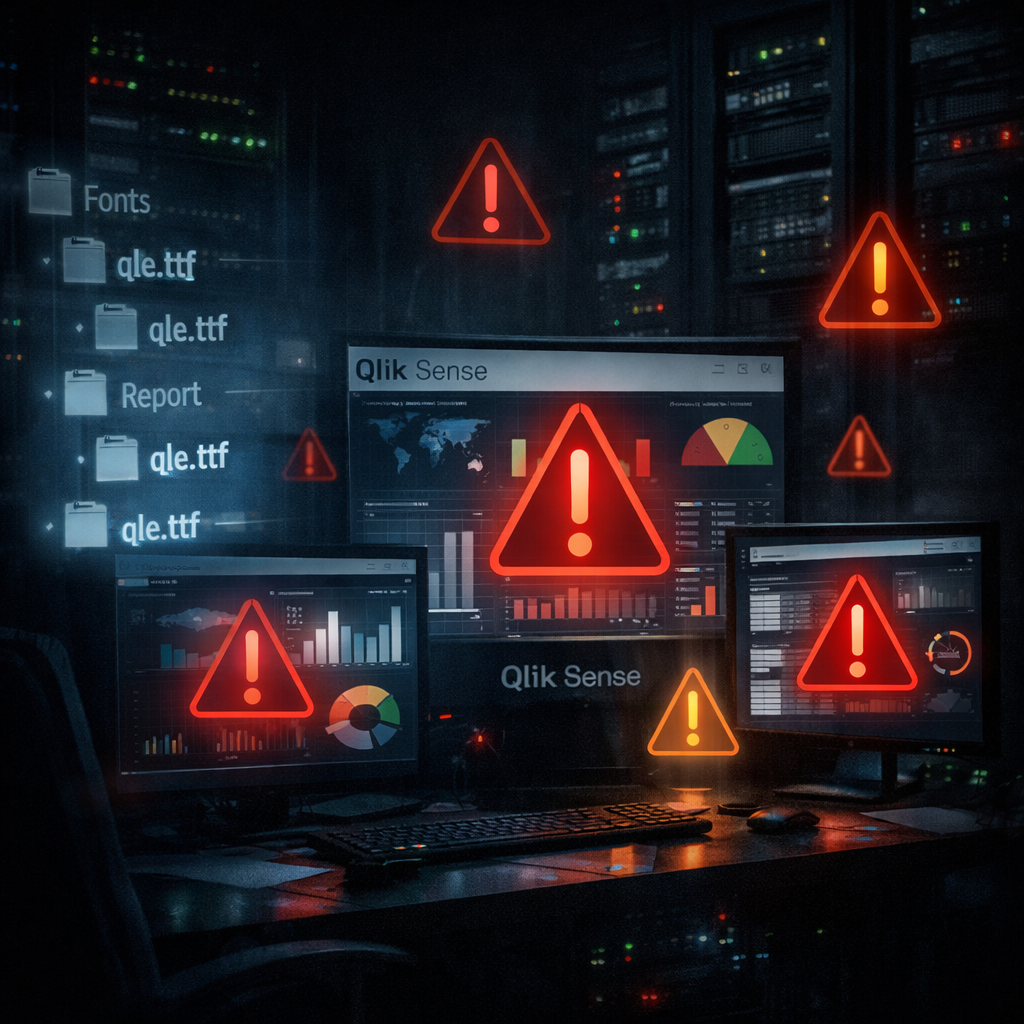
After gaining access, Cactus deploys familiar post-exploitation tools: Remote Monitoring and Management software like ManageEngine or AnyDesk; utilities such as Plink and PuTTY disguised under innocuous names; and tools like WizTree for disk usage maps. They often leverage PowerShell or batch jobs to run arbitrary commands. A key telltale sign is output redirected into TrueType font files like “qle.ttf” or “qle.woff” within Qlik’s fonts folder — these files don’t exist in clean installations, so their presence is a red flag.
Scale, Geographic Reach, and Risk
An internet scan carried out by researchers revealed over 5,200 Qlik Sense servers online, with about 3,100 (roughly 60%) still vulnerable to the DoubleQlik exploit. Of those, at least 122 servers showed signs of having recent compromise artifacts. Nations with high exposure include the U.S., Italy, Brazil, Netherlands, Germany, Spain, Ireland, and the UK.
The common denominator across all attacks is systems that haven’t applied patched updates. Despite fixes being released for these vulnerabilities (CVEs) as far back as 2022–2023, many organizations have lagged in implementing them, allowing Cactus to gain initial access easily.
Mitigations and Best Practices
To defend against these attacks, system administrators should immediately patch Qlik Sense Enterprise Windows environments to versions that fully cover CVE-2023-41265, CVE-2023-41266, and CVE-2023-48365. Servers should have exposed management interfaces removed or shielded behind VPNs or restricted networks.
Organizations should hunt for indicators of compromise such as the presence of qle.ttf or qle.woff in the /Client/qmc/fonts/ directory. Monitoring for abnormal processes — e.g. PowerShell or cmd spawning unexpectedly — and auditing binaries like Rclone, Plink, or AnyDesk in unusual locations are also advised.
These attacks underline a growing pattern: many organizations are failing to patch known vulnerabilities in mission-critical software, especially ones exposed to the internet. Products like Qlik Sense are often deeply embedded in enterprise ecosystems, meaning breaches or ransomware deployments can have serious operational and financial consequences. For stakeholders, this should prompt a reassessment of patch management, external attack-surface exposure, and incident detection readiness. Going forward, watch whether Cactus evolves new bypasses as administrators rush to remediate, and how detection tooling adapts to flag these font-file indicators and solve visibility gaps.