Security researchers have published a proof-of-concept (PoC) exploit for CVE-2026-59346, a serious integer overflow bug in VMware’s VMXNET3 virtual network driver. The vulnerability allows someone with admin privileges on a virtual machine (VM) to crash—or, in some cases, potentially execute code on—the host system, though the public exploit currently triggers only a host process crash rather than reliable remote code execution.
How the Bug Operates
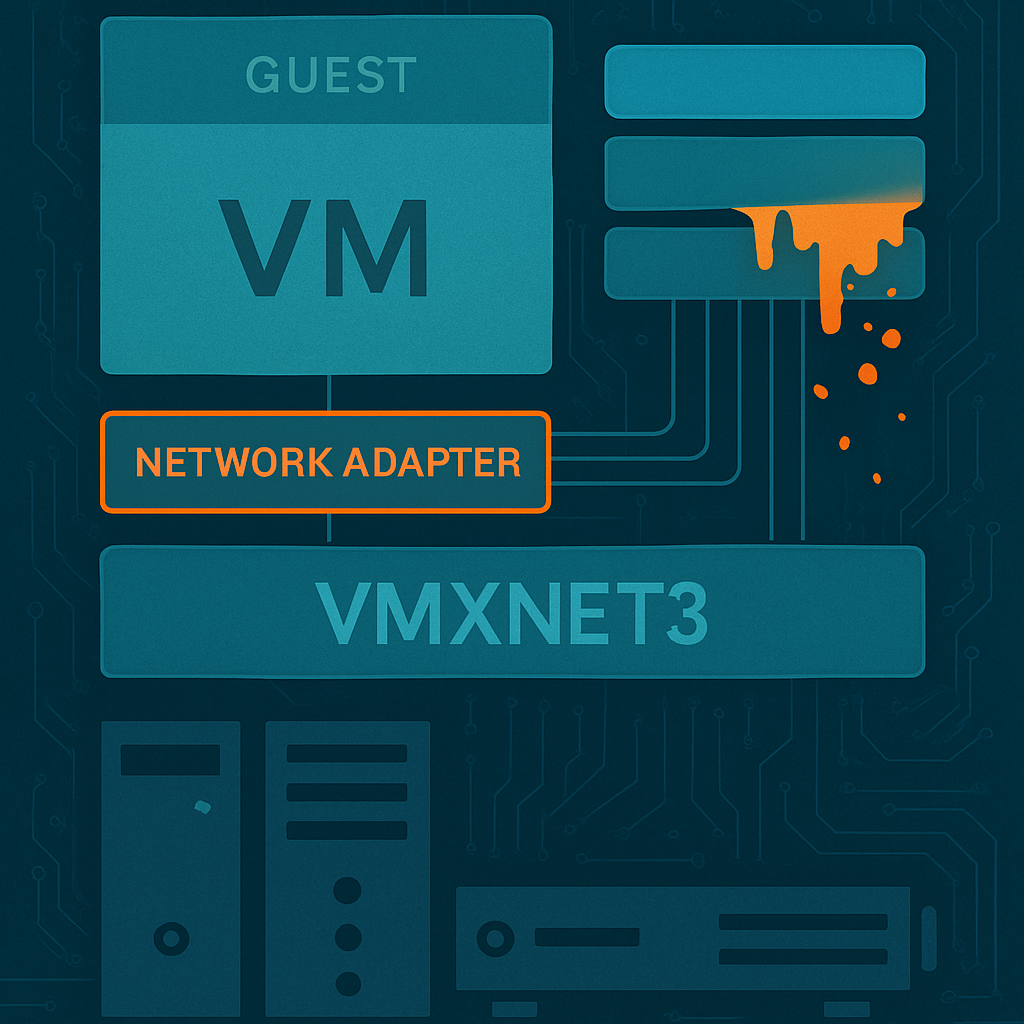
The flaw is embedded in the TCP Segmentation Offload (TSO) handling inside the host’s vmware-vmx process, which splits large network packets into smaller segments for transmission. A 32-bit multiplication used in calculating the total memory required for all segments can overflow when the result exceeds the 32-bit limit. When this happens, the calculation wraps around, prompting the host to allocate a buffer based on the incorrect (reduced) size. Meanwhile, the process copies data according to the original (overflowed) segment count—this mismatch enables guest‐controlled data to be written beyond the buffer, corrupting memory.
Impact, Timeline, and Mitigation
Broadcom, which now owns VMware’s security portfolio, assigned this vulnerability a high-severity CVSSv3 score of 9.3. A patch was issued in VMware Workstation and Fusion version 26H1u1, released on September 3, 2026. Older releases—specifically 25H2 and earlier 26H1 versions—are also affected.
The public PoC comes from a researcher known as 0xCyberstan. It operates as a Linux kernel module inside a VM equipped with a VMXNET3 adapter. By writing directly to network transmit descriptors (bypassing the guest driver’s TSO safeguards) and then invoking host processing, the exploit causes an out-of-bounds write that crashes the vmware-vmx process, shutting down the virtual machine.
While the Zero Day Initiative confirmed the bug could support full arbitrary code execution in the hypervisor, only a crash has been demonstrated so far. The previously patched CVE-2025-41236 issue addressed related TSO and packet size checks, but did not prevent this newer overflow in the multiplication stage.
Since there’s no recommended workaround beyond applying the update, VMware’s advisory urges users to install version 26H1u1 or newer. It also highlights that securing the guest OS won’t address this issue—only host systems running an updated version of Workstation or Fusion can be protected.
This newly published PoC illustrates how the vulnerability occurs in real-world testing only in isolated labs. In one documented test environment, the exploit used VMware Workstation Pro 25.0.1 with an Ubuntu host and Alpine Linux guest. The researcher warns such testing might wipe unsaved data or crash the entire VM environment.
What this means is that administrators need to scan host systems immediately for affected VMware versions and plan upgrades; cybersecurity teams should monitor for similar integer overflow conditions in other virtual network adapter code paths. Though the exploit isn’t a weapon yet, it very well could be in the wrong hands.