OpenCode, a widely used open-source AI coding agent, has been found vulnerable to a serious security flaw that lets malicious websites execute arbitrary commands on developers’ computers. This remote code execution vulnerability, designated GHSA-632h-h47v-g4x4, was introduced via content type confusion in OpenCode’s /global/upgradeAPI, alongside unsafe handling of externally supplied upgrade targets. The issue was patched in OpenCode version 1.18.22.
What Went Wrong
OpenCode, launched in June 2025 to help integrate AI language models into developer workflows—and now boasting over 208,000 GitHub stars and 16 million monthly users—runs a local browser interface by default on localhost (127.0.0.1:4096) without authentication. Versions 1.14.30 through 1.18.21, when installed via npm, pnpm, or Bun, are affected.
The core of the flaw lies in the /global/upgradeendpoint. It accepts an attacker-controlled target value, which is then used in a package manager command to install OpenCode at a specified version. The package specification also allows URLs pointing to remote tarballs. An adversary could supply a malicious archive containing a crafted package.jsonfile with a preinstall lifecycle script, which would then execute under the privileges of the OpenCode process.
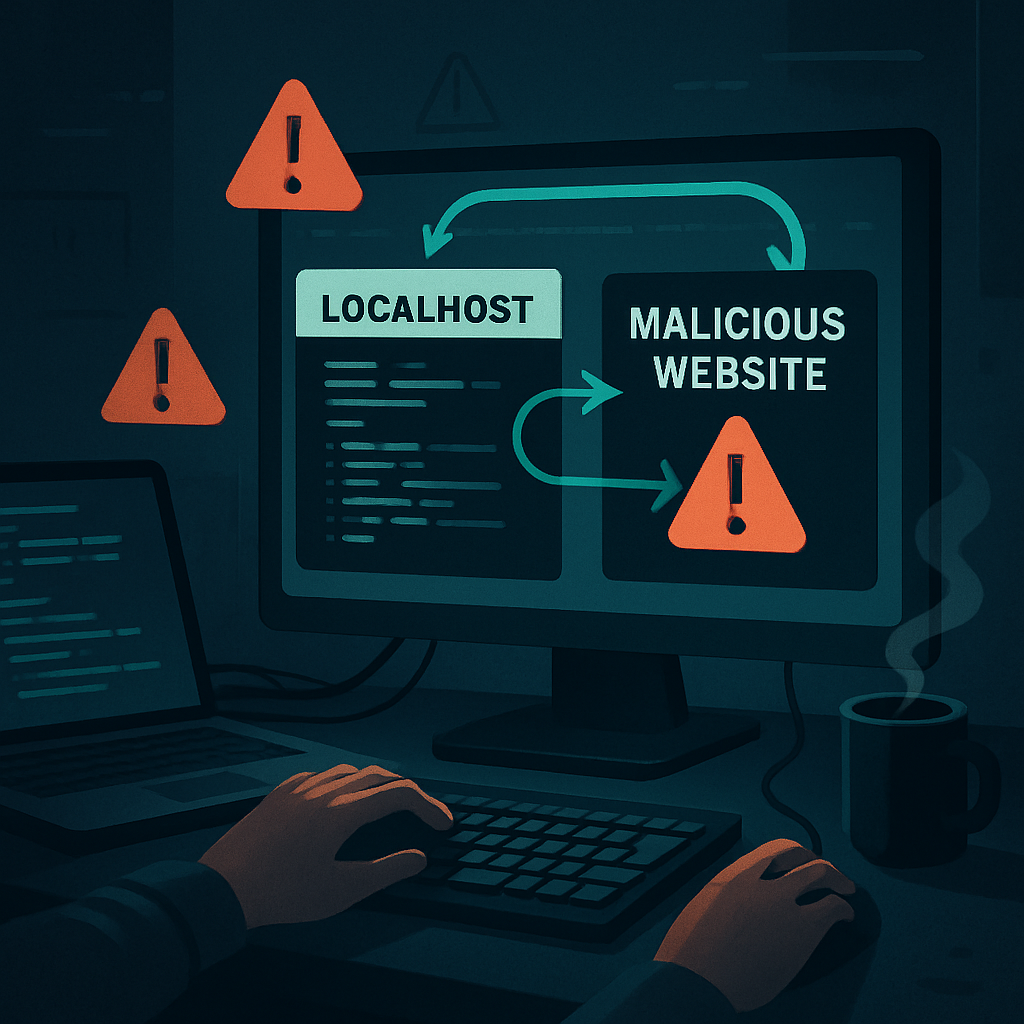
Even though the service listens only on localhost, researchers demonstrated that a malicious webpage could invoke the local API through a trick. Instead of using a fetchrequest with application/json—which would be blocked by CORS preflight—the attack uses a top-level navigation via an HTML form. The server expects JSON but doesn’t verify the content type, allowing form submissions encoded as text/plainto pass if they resemble JSON payloads. This enables the payload to reach the upgrade endpoint and install a rogue package.
How Many Are Affected?
The vulnerability impacts any system running OpenCode version 1.14.30 up to 1.18.21, when installed through npm, pnpm, or Bun; using the commands opencode serveor opencode web; and lacking strong access controls (either no password or cached credentials in the browser).
Metrics from public npm registries show that between September 17-23, 2026, over 647,000 downloads involved vulnerable versions—roughly 38.9% of all OpenCode downloads in that window. These figures don’t distinguish unique installations or reveal how many users had the web server exposed.
Patch and What Developers Should Do Now
The issue has been addressed in OpenCode version 1.18.22. The fix involves validating the upgrade target strictly as a semantic version (blocking remote package URLs) and replacing the generic raw handler with one that respects content types, specifically rejecting submissions marked text/plainfor this endpoint. From that version on, requests like the demonstrated exploit now return HTTP 415 “Unsupported Media Type.”
Developers are urged to update immediately to version 1.18.22 or newer, restart any running OpenCode processes, and confirm their version and install mechanism. It’s also advised to set the OPENCODE_SERVER_PASSWORDwhen using the web interface, avoid opening the service beyond localhost, and treat any unexpected package manager activity, lifecycle script executions, or outbound download attempts as potential signs of compromise.
Password protection helps, but it doesn’t replace patching, especially since browsers may carry over cached credentials that compromise the protection.
This vulnerability was reported privately to the maintainers on August 11, 2026. The code path leading to the patch has been in place since April 29. Version 1.14.30 was released the next day. No CVE was awarded for this issue, so users should watch for the GitHub advisory identifier GHSA-632h-h47v-g4x4.
Why It Matters
AI coding agents like OpenCode are increasingly central to developers’ workflow. When their local components expose interfaces on developer machines—especially without strong authentication—vulnerabilities like this cross a critical risk threshold. Attackers exploiting remote code execution can gain full control, leading to backdoors, data theft, or worse.
Going forward, the community should demand stricter defaults, clear isolation between local and remote operations, and better handling of content types. Keep tabs on your tools: update fast, review each version’s behavior, and avoid leaving trust assumptions unguarded. OpenCode’s fix is a strong move—but this incident underscores how easily high-visibility tools can become attack vectors if infrastructure security is overlooked.