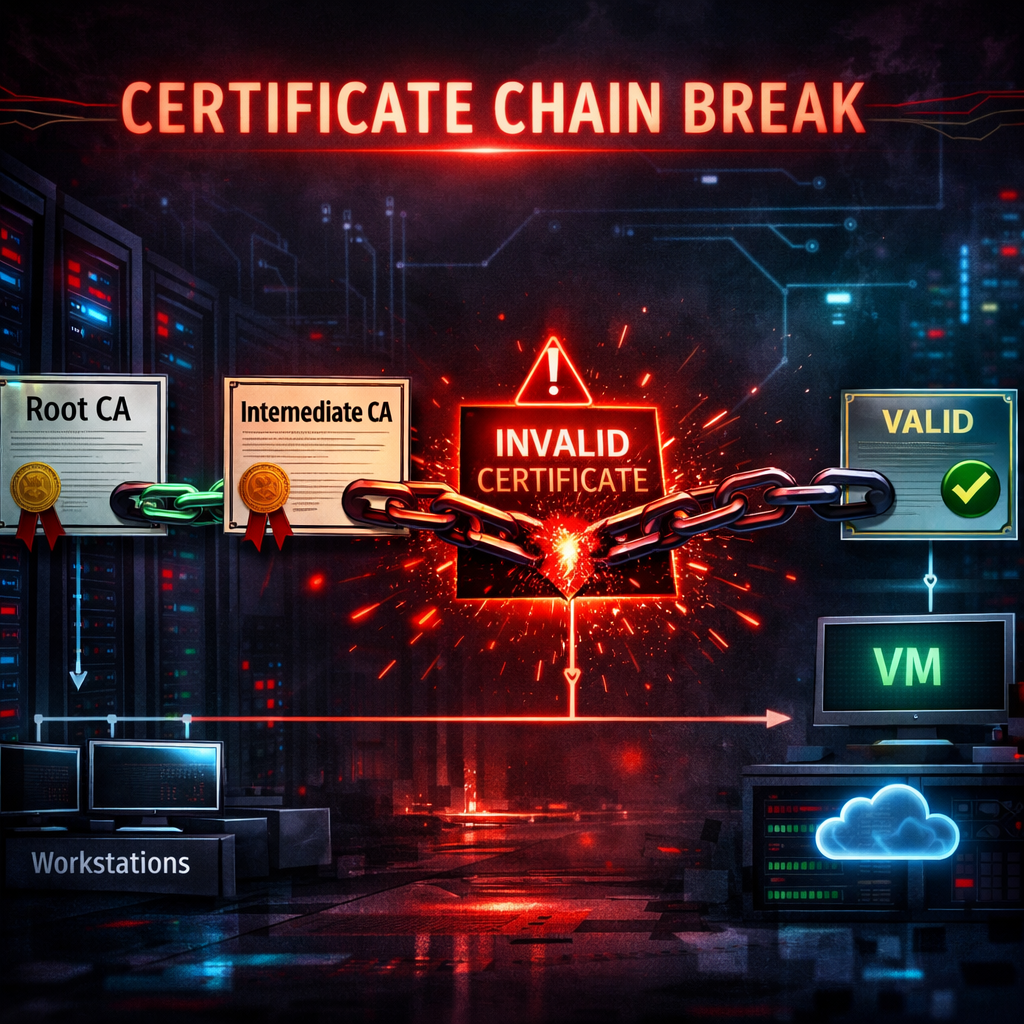
A newly disclosed certificate validation flaw in LXD and Incus could allow remote attackers to bypass login protections and take full control of clusters and managed virtual machines. The issue resides in how these services verify certificate chains during TLS handshakes — while the first certificate is correctly checked for private‐key ownership, subsequent certificates in the chain aren’t validated against the trust store. This gap enables malicious actors to impersonate trusted entities merely by providing their public certificates. The vulnerability has been assigned a maximum severity score of 10.0. Incus calls it “critical,” and Canonical issued its record under CVE-2026-112816.
How the Flaw Works
The flaw affects the HTTPS management listener used by both LXD and Incus. In a standard TLS exchange, a client must prove it holds the private key for the first certificate in its chain. However, attackers can manipulate the remaining chain elements — which are controlled on the client side — to include the public certificates of trusted hosts. Since only the initial certificate undergoes private key verification, the rest are compared only by their public content. As a result, an attacker presenting the public key of a trusted certificate can gain access as if they held that certificate’s private key.
This vulnerability grants attackers powerful privileges. Presenting the server’s own certificate provides access to database gateways; submitting another cluster member’s provides internal cluster access and bypasses authorization. It even exposes paths for manipulating the trust store — attackers can delete or renew entries via certain self-service workflows. The issue also undermines trust in agent-host and virtual machine connections, and even affects authorization decisions embedded in custom scripts or those using tokens or OpenID Connect, because those too rely on passed certificate chains.
Scope, Impact and Remediation
Incus versions prior to 7.6.0 are affected; anything from 7.6.0 onward includes the fix. For LXD, Canonical pushed patches in versions 4.0.15, 5.0.11, 5.21.9, and 6.10.1, covering the vulnerable release branches. Administrators must determine the version in use and match it against those releases to know whether they are exposed.
Until patches are applied, there’s no configuration workaround that fully closes the gap — restricting access to the HTTPS endpoint to trusted hosts helps reduce risk, but does not eliminate it. Organizations should also limit who can reach management interfaces. So far, there have been no reports of this flaw being exploited in the wild, though exposure does not equal confirmed compromise.
Given the severity of this flaw, immediate action is necessary for environments running Incus or LXD. Upgrading to patched versions is critical, alongside limiting external exposure of management interfaces. Organizations should also audit certificate trust stores and review any authorization scripts or workflows that accept client-presented certificate chains.
What this means and what to watch
This vulnerability strikes at the foundation of trust in Linux container orchestration. LXD and Incus serve as key infrastructure for managing virtual machines and clusters; a flaw this deep in certificate validation undermines security controls that many deployments rely on. Going forward, watchers should examine how certificate validation is implemented across orchestration tools, and whether other widely-used systems have the same weak chain verification. Defense will depend not just on patching, but on zero-trust practices: limiting who can access management layers, enforcing strict certificate policy, and avoiding implicit trust based solely on presented public certificates. Knowing a system is exposed isn’t enough; verifying that attackers haven’t already leveraged this hole will be essential.