A Spanish-speaking threat actor known as Blind Eagle has launched a fresh phishing campaign focused on Latin America, using bogus court- and administration-themed lures to deliver a remote access trojan (RAT) linked to AsyncRAT and DCRat. The group, also called APT-C-36 and active since at least 2018, crafted new scams in Spanish and Portuguese intended to bypass defenses in judicial, fiscal, educational, and institutional settings.
How the Phishing Scheme Works
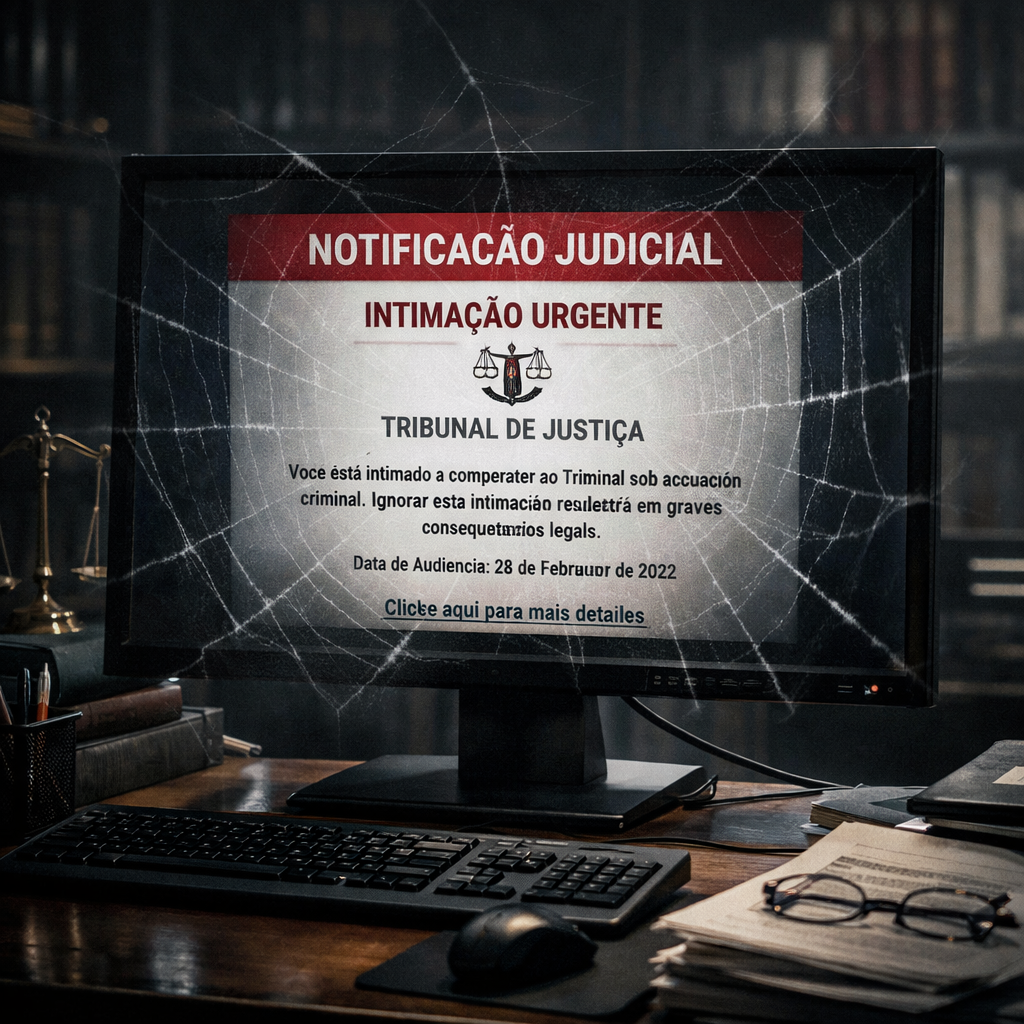
The attack starts with an email carefully tailored to individuals responsible for legal or administrative functions—contract handlers, court staff, or public officials. The message contains what looks like a legitimate judicial or administrative document—examples include notices from the Attorney General’s office, court proceedings, or tutela protections—all written in Spanish or Portuguese.
A striking example involves a Colombian-themed email using an XHTML file that embeds a weaponized SVG image. That image, when opened, triggers HTML smuggling: a technique that constructs a ZIP archive directly in the victim’s browser, sidestepping typical security filters. Inside, a JavaScript dropper disguised as a network auditing tool performs reconnaissance—collecting system details like OS version, memory size, network profile, localization (Spanish or Portuguese), and other environment metadata.
Payload and Post-Infection Tactics
Once executed, the dropper triggers a Visual Basic Script which disables built-in protections—namely, Windows AMSI (Antimalware Scan Interface) and ETW (Event Tracing for Windows). While this misdirection plays out, it displays a fake criminal citation to distract the user.
The malware also removes the original phishing artifact, clears “Mark of the Web” metadata which might be used by Windows to flag files downloaded from the internet, and installs itself persistently via the Windows Startup folder. The final stage uses PowerShell to decode and run the RAT payload entirely in memory. Analysis shows this RAT shares code structure, build traits, and behavior with AsyncRAT and DCRat.
So far, there’s no confirmation that any actual organizations have been compromised. But the capabilities of the attack are extensive: once inside, the malware could perform environment scouting, harvest sensitive documents, capture keystrokes or screenshots, surveil systems, and quietly extract data over encrypted connections.
Targets and Geographic Signals
The campaign zeroes in on judicial, educational, administrative, and fiscal institutions—entities likely to hold sensitive financial, legal, or institutional records. The use of Portuguese and Spanish in the lures, infrastructure ties to Brazil, and timing consistent with Brazilian operational hours indicate a regional focus. Experts assess that this cluster is operating out of Brazil under the Blind Eagle umbrella.
This attack marks another evolution in Blind Eagle’s phishing arsenal, which had previously leveraged RATs such as BitRAT, LimeRAT, NjRAT, Quasar, and Remcos to target Latin American clients. The new campaign, however, shows higher sophistication in disguising initial access and maintaining stealth once inside. Since 2018, the actor has followed a pattern of targeting roles involved in judicial or institutional processes using administrative-themed phishing to deliver malware.
This development matters because it highlights how advanced persistent threats (APTs) continue refining strategies to bypass defenses that companies might believe are robust—especially in localized or regional threats. The use of HTML smuggling and in-memory payload execution shows a deliberate move to skirt detection by traditional email filters, signature-based AV tools, and post-compromise monitoring.
Organizations in Latin America, particularly those dealing with tax, legal, and education, should watch for phishing emails claiming to be from court or government agencies. Employee training, disabling or sandboxing automatic execution of scripts, filtering archives and ZIP attachments, and ensuring endpoint detection tools catch anomalous behavior across AMSI/ETW bypass—and encrypted shellcode execution—are key defenses.
Blind Eagle’s renewed campaign provides a stark reminder: cyber threats are never static. While many organizations focus on large-scale or global threat actors, regionally specialized APTs like Blind Eagle sharpen their tools to exploit local bureaucratic systems, languages, and legal conventions. The danger is that any overlooked procedural detail—like recognizing a fake court notice—can become the opening shot in a full-scale breach. Defender investments in detection, response, and education need to stay ahead of this evolving playbook.