Phishing campaigns in November 2026 are exploiting Microsoft 365’s device code authentication to gain unauthorized access without needing to bypass multifactor authentication (MFA) or steal passwords. Targeting firms with seemingly routine payment tasks—such as verifying remittance or invoice status—attackers are using fake Microsoft sign-in pages combined with device code flows to hijack user accounts. Security researchers uncovered malicious HTML and SVG attachments that either redirect users or display phishing content to initiate the exploit.
How the Device Code Flow Is Weaponized
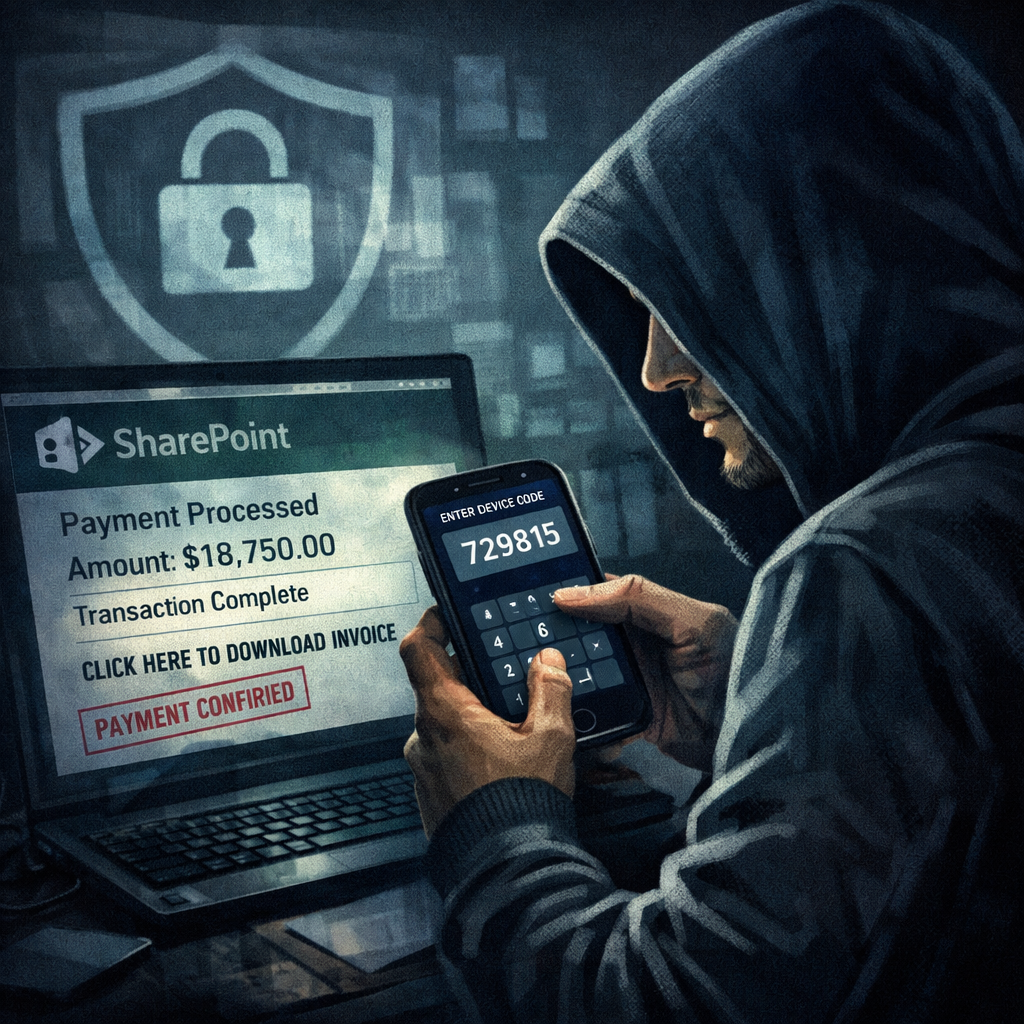
Device code authentication is intended for devices that have limited input capabilities, like shared displays—users enter a short code on another device to complete authentication. In these attacks, once employees click attachments masked as financial documents, they are led to counterfeit SharePoint workspaces. These pages prompt them to unlock documents by entering a code. When the user signs in and completes any required MFA, the attacker-controlled client obtains the session tokens.
Thanks to these tokens, threat actors gain access to whatever permissions that client has—potentially exposing corporate email, SharePoint files, or other sensitive data. Researchers note that this method doesn’t rely on any password or MFA weakness; the key point of failure is user interaction with the fake code flow itself.
Spotting & Thwarting Device Code Phishing
Organizations can defend by scrutinizing Microsoft Entra (formerly Azure AD) sign-in logs—filtering for sessions where the authentication protocol is “Device code”. Cross-checking those log entries with source IPs, app names, and timestamps helps identify suspicious behavior. Even if later tokens come via a different authentication flow, the original device code usage often leaves a trace in the “Original transfer method” field.
Admins should consider implementing Conditional Access policies that block device code flows wherever possible. Microsoft provides controls to disable this authentication path. It’s advised to run any such policy in report-only mode initially to see what legitimate workflows might be affected, then gradually enforce it—while carefully managing exceptions and emergency access settings.
After any suspected device code abuse, organizations should revoke the affected user’s sessions and conduct post-incident reviews—checking for any data moved or permissions escalated. Also, employees need training: they should never enter a device code unless they initiated the workflow and must verify any payment or invoice requests through known channels.
This threat circles back to broader issues: phishing via OAuth or device flows is a growing vector that doesn’t rely on weak passwords or misconfigured MFA, but rather leverages user behavior. Indicators of compromise tied to these attacks include specific malicious domains, HTML/SVG redirectors, ZIP attachments with hidden scripts, and fake document workspaces. Detecting those early is critical.
As phishing techniques evolve, this method marks a dangerous escalation. Blocking device code flows may disrupt some workflows, but the alternative—leaving organizations exposed—poses a more serious risk. Security teams must balance usability with protection, monitoring logs vigilantly and educating staff on the subtle cues of advanced phishing threats.