A suspected China-based advanced persistent threat (APT) group has revamped the EggStreme malware framework in sophisticated ways to continue targeting Philippine government entities. The reengineered toolkit now includes passive backdoors, upgraded network protocols, and enhanced command capabilities — all designed to evade static and heuristic detection engineered after EggStreme’s initial exposure in September 2025.
What’s changed with EggStreme?
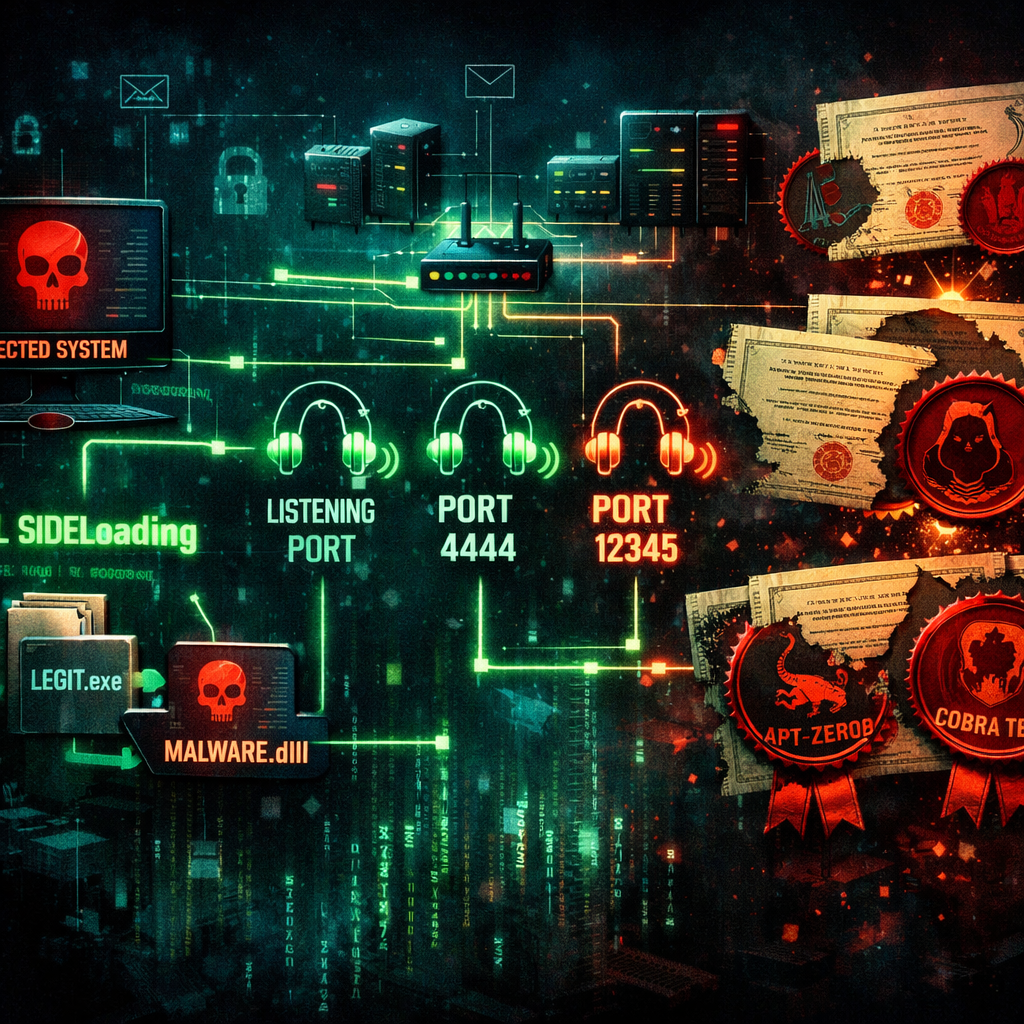
The core EggStreme bundle still uses DLL sideloading to load payloads, but several elements have been significantly altered. Components like EggStremeFuel (also called RawCookie), EggStremeLoader, EggStremeReflectiveLoader, and EggStremeAgent (also known as Gorem RAT) remain central. Agent features enable reconnaissance, lateral movement, data theft, reverse shells, and executing payloads via EggStremeWizard. An extra keylogger component, EggStremeKeylogger, was previously part of the arsenal, though it has since been removed from new builds. Tools shared with another actor cluster, CL-STA-1048, were also observed between March and September 2025.
Detection evasion, passive mode & new tactics
Several changes have been implemented to enable stealthier attacks. The toolkit’s cryptography has shifted from RC4 to RC5 before moving to a custom cipher. Previously single certificate authorities have been replaced with campaign-specific ones. Core agents now support features for Active Directory discovery, Windows Management Instrumentation (WMI) queries, and remote code execution using PowerShell, .NET assemblies, and Portable Executables.
Later builds also incorporate passive backdoor behavior: instead of “calling home” to command-and-control (C2) servers, this variant opens a listening port and waits for operator access. Lateral movement has shifted away from built-in tools toward use of unmanaged systems that can stage payloads via Server Message Block (SMB) and execute DLL sideloading remotely via VBScript. Persistence tactics such as sideloaded system library DLLs, staging through file shares, and in-memory execution persist.
Wider attack landscape in Southeast Asia
EggStreme isn’t the only China-aligned APT targeting the Philippines. Mustang Panda has recently deployed PlugX malware against government officials by sending phishing emails disguised as bilateral meeting agendas related to the ASEAN Summit. The emails claimed to be from Laos’s Ministry of Foreign Affairs and referenced actual diplomatic priorities to appear legitimate.
Meanwhile, another threat actor known as Earth Alux (aliases Ink Dragon, Jewelbug, REF7707, UAT-11587) has been running espionage operations across Southeast Asia through advanced custom payloads. Since mid-2025, Earth Alux has used FINALDRAFT, and more recently new remote access trojans called PerfectPioneer RAT and KUKURAT. Their arsenal supports HTTP/3 communication — a less common protocol leveraged to evade detection — and employs lateral movement via tools like PsExec, WMI, WinRM, credential dumping, domain controller compromise, and more.
Rebuilding EggStreme with passive backdoors and upgraded evasion techniques shows the operators are acutely aware of what triggers detection. Such fast adaptation underlines both the maturity of the adversary and the limits of many existing defenses. For security teams, this means reliance on signature-based detection and heuristics isn’t enough — proactive monitoring for anomalous behavior (such as unexpected listening ports or unusual SMB activity), certificate misuse, and deployment patterns will be crucial. With other aligned groups like Mustang Panda and Earth Alux operating in the same theater using related stealth tradecraft, Philippine government entities — and organizations with similar exposure — remain high-value targets. What comes next: seeing how defenders update visibility, response, and attribution in this evolving threat environment.