A new method disclosed by researchers allows attackers with physical access to source PCs bypassing the TPM lockout protecting Windows Hello and BitLocker PINs. The attack exploits vulnerabilities in firmware and hybrid flash chips—meaning PINs can now be cracked in hours or days rather than years.
How the Attack Works
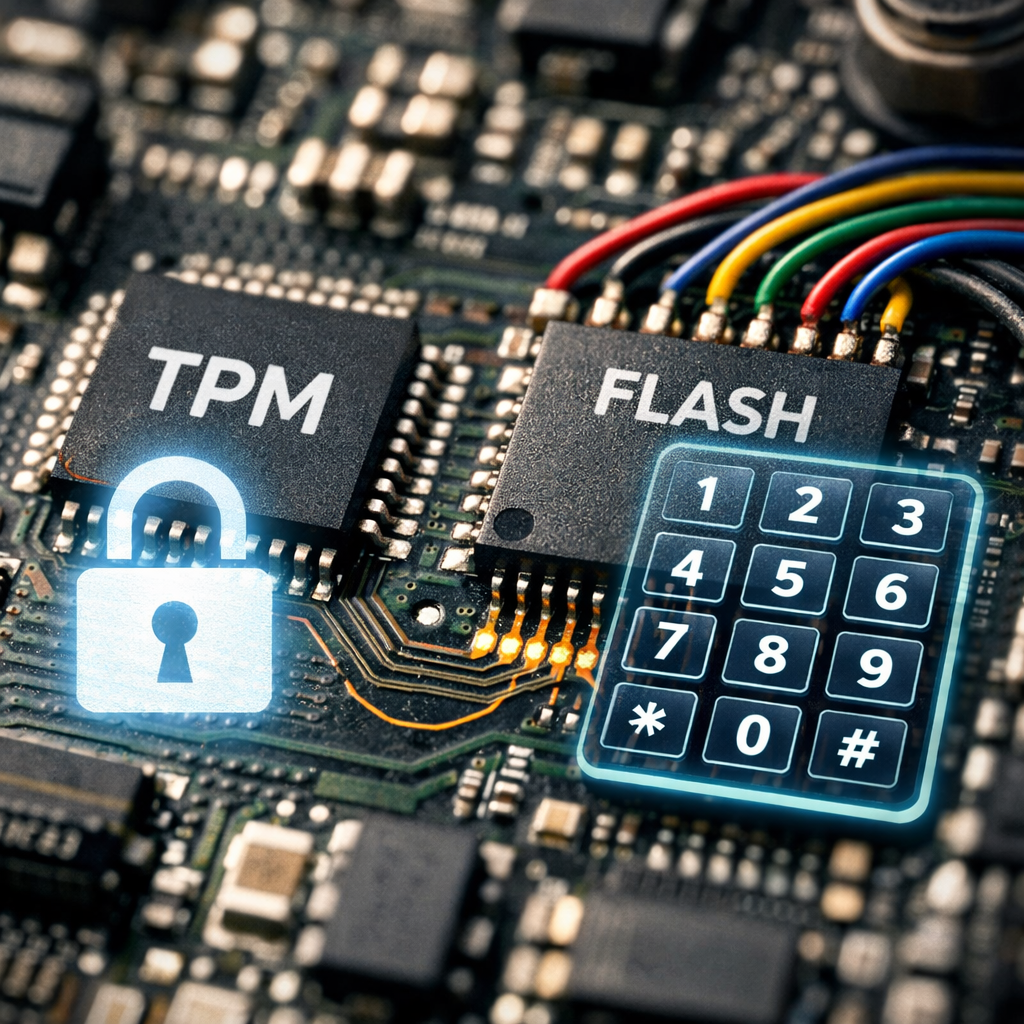
Trusted Platform Modules (TPMs) are security components used to protect PIN-based authentication. When PIN guessing fails repeatedly, TPMs typically lock out and impose delays before allowing more attempts, severely limiting brute-force attacks. However, many modern PCs use firmware TPMs embedded in their CPU instead of separate chips. These processors store sensitive state—including the count of failed PIN attempts—encrypted on the onboard flash memory.
Some of these flash chips include a counter mechanism called RPMC (Replay Protected Memory Counter), intended to ensure the failure count can only increase. Researchers discovered that on many AMD PCs, firmware doesn’t verify that the RPMC counter has been updated. An attacker can insert a tiny board between CPU and flash chip to block counter updates while still signaling success, enabling repeated PIN attempts with no lockout.
Flash chips from Winbond present another terrifying vector. A brief voltage glitch—a method that temporarily disturbs power supply—can cause the chip to leak its secret signing key for the counter. Armed with that key, attackers can forge counter values arbitrarily, tricking the system into thinking it still has remaining attempts.
Testing Scenarios
In one lab test, on an AMD Ryzen AI 5 330 system, researchers broke a 4-digit Windows Hello PIN in 57 minutes by trying fewer than 240 guesses. With TPM lockout functioning properly, the same attack would have needed months. In another test, targeting BitLocker on an Intel Core Ultra 5 125H with Winbond flash, they cracked a 6-digit PIN in under seven minutes. If lockout worked correctly, the same guess work would span years.
Which Devices Are Vulnerable, and What’s Being Done
Vulnerability depends heavily on which processor firmware and flash chip are present. AMD PCs that use RPMC flash are at risk from the counter-blocking trick; those with Winbond chips are at risk from voltage glitch attacks regardless of the CPU manufacturer. PCs without RPMC flash are also exposed via simple write-back attacks of old state copies.
AMD has acknowledged the issue (tracked as CVE-2026-43613) with a moderate threat score, and expects to ship firmware patches between November 2026 and February 2027 across Ryzen, Ryzen AI, Threadripper, Athlon, and EPYC lines. Intel has pushed back, stating the issue is specific to the flash chip maker’s hardware rather than its own CPUs. Winbond, meanwhile, has not yet committed to a full fix for its flash technology.
What Users Can Do Now
- Increase PIN length: For both Windows Hello and BitLocker, using at least a six-digit PIN significantly increases time needed to crack.
- Enable enhanced PINs: BitLocker supports symbolic and mixed character PINs; using those improves resistance.
- Apply firmware updates: Once manufacturers publish patches, installing them can prevent or mitigate the vulnerability.
- Maintain physical control: Since attacks require opening the case, keeping devices secure is essential.
This flaw underscores a critical nuance in system security: physical access still matters immensely, even in modern architectures built around robust principles like TPM protection. Firmware TPMs and flash storage corner cases have exposed a weak link—if any element in the chain can be tricked or bypassed, the whole system’s guarantees unravel. Going forward, manufacturers and enterprise security teams must ensure firmware integrity, mandatory counter-validation, and minimum PIN complexity are enforced. Watch for upcoming firmware updates, and in the meantime treat physical tampering threats seriously—not just software vulnerabilities.