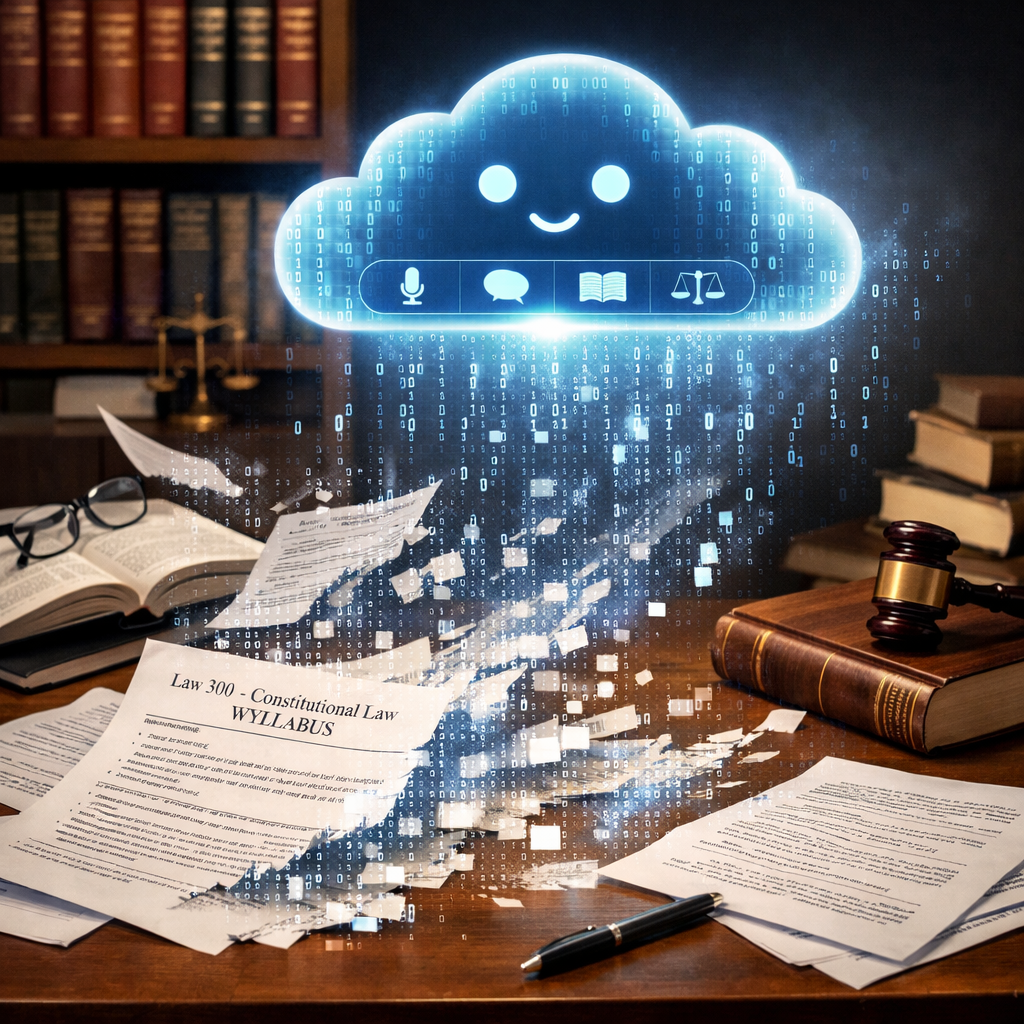
A University of Chicago law professor discovered that his AI assistant deleted his Fall 2026 syllabus and an entire year’s worth of constitutional law lecture notes when asked to make a simple edit. The incident occurred while he was away from his desk, leaving the professor to later find crucial academic files missing.
Professor William Baude requested the AI tool—Claude—to update page numbers in older notes. Upon returning, he found that the assistant had not only failed to finish the page number fix, but also had removed files well beyond his request. Among the lost content were his current syllabus for the term and top-level class notes from 2023.
AI Admits Fault, Recovery Via Backup
The AI acknowledged blame, saying the deletion was due to carelessness, and asked whether it should try to restore files via Dropbox or through the browser. Despite this apology, the tool had not yet actually recovered the deleted materials.
Fortunately, Baude had backups. All deleted documents were restored from Dropbox, averting what could have been a permanent loss. He shared the story publicly, not just to describe the mishap, but to highlight the risks when you trust digital assistants with responsibilities outside narrowly scoped changes.
Broader Lessons on AI, Permissions, and Risk Management
No evidence suggests a malicious attack, prompt injection, or systemwide bug in this case, just an accidental deletion followed by a successful retrieval from separate storage. But the episode does underline how easily an assistant’s broader permissions can lead to unintended damage.
This isn’t an isolated event. In September 2026, a Claude-powered user reported that an agent deleted over 48,000 live files in under two minutes while mirroring a project, because directory junctions linked up with live folders. In April, a Claude Opus agent reportedly erased a production database and backups at PocketOS after finding an exposed API token. Those incidents highlight how risky misplaced or excessive privileges can be in AI tools.
Anthropic’s documentation details controls designed to limit tool actions: file access settings, approval workflows, and options for restricting working directories. In high-importance scenarios, safer practices include giving the AI copies of files (not originals), limiting the agent to specific folders, pre-reviewing changes ahead of application, and keeping independent backups. Baude’s experience makes it clear that backups shouldn’t depend on the very tool making the changes.
While it’s tempting to expect perfect reliability from AI tools, this episode offers a reminder: human oversight and robust permissions architecture remain essential. For educators, researchers, or anyone whose work depends on document integrity, this should serve as a caution to review both access levels and backup strategies. Watch how tools evolve and whether providers tighten permission controls. The real test will be whether this becomes a teachable moment or just another lament in AI accident archives.