Apple’s Lockdown Mode, designed to shield high-risk users from digital attacks, has been compromised by a newly demonstrated jailbreak that persists through iOS 27.2 updates. The exploit, shared via a video from a hacker group called Calif, reveals the flaw despite Apple’s previous claims of perfect protection since 2022.
How the Exploit Works
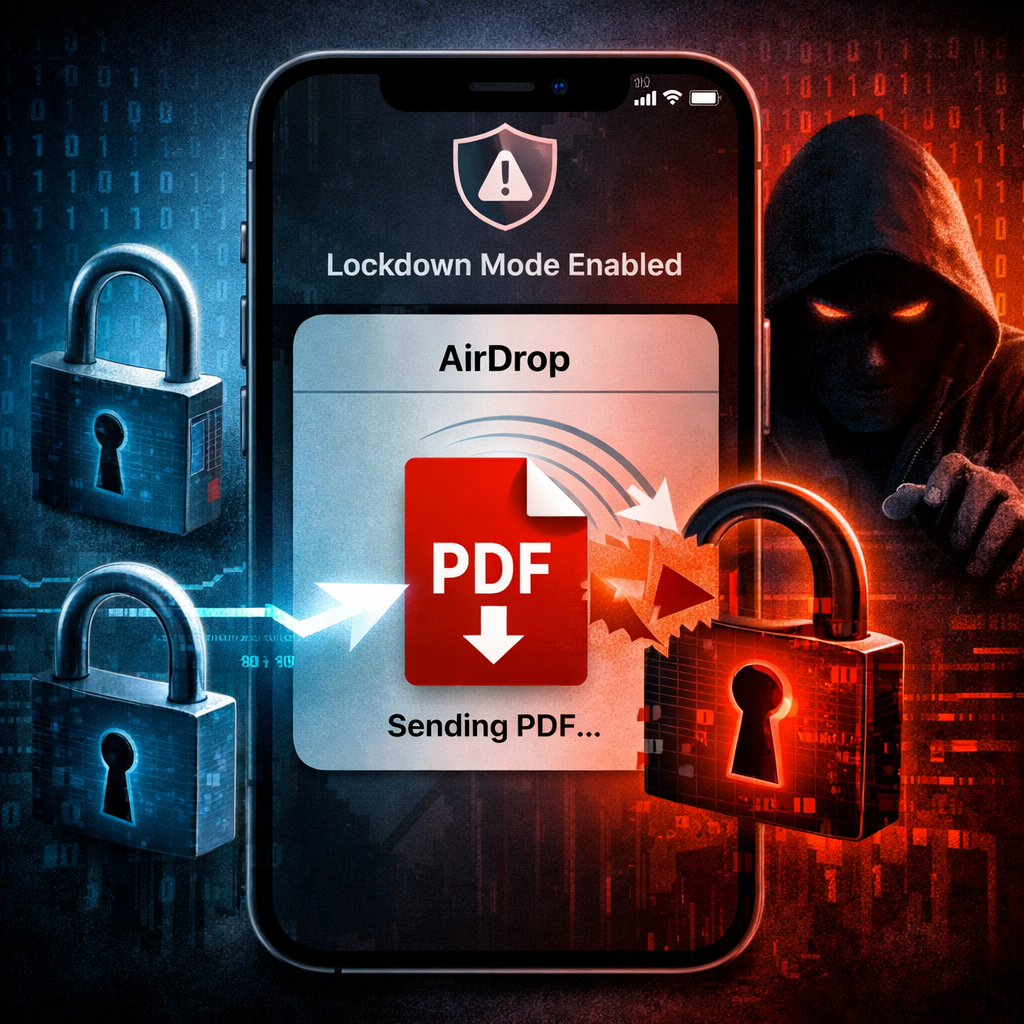
The incident involves an iPhone 18 Pro with Lockdown Mode enabled. A PDF delivered over AirDrop is opened while Lockdown Mode is active. After that, the device is updated to iOS 27.2 despite the security mode remaining engaged throughout. The video shows the user ignoring a warning in the Software Update section that Lockdown Mode could constrain certain settings. After dismissing the notice, the update proceeds upon entering the device passcode.
No technical proof has been released yet by Calif. It’s possible the jailbreak was pre-installed before recording, or that the video omits key details. The group claims it is informing Apple of the vulnerabilities involved, but says it won’t be releasing a tool for public use.
What Lockdown Mode Was Designed to Do
Introduced in iOS 16, Lockdown Mode severely limits the iPhone’s communication and content channels. It blocks many browser technologies, restricts messaging content, disables configuration profiles, prevents connection to non-secure Wi-Fi, and stops enrollment in Mobile Device Management (MDM) systems. The measure targets users such as government officials, activists, and executives who are especially vulnerable to targeted cyberattacks.
Apple maintained that since 2022, no successful bypass had been demonstrated in the wild while Lockdown Mode was active. This claimed perfect record, reiterated in March 2026, appears to have been broken.
Implications and What Remains Unclear
If authentic, this jailbreak undermines Lockdown Mode’s promise of near-absolute defense for high-profile targets. Attack vectors involving document files—like PDFs delivered over AirDrop—are now under scrutiny as potential weak points during Lockdown Mode.
There are still many unknowns. It’s not confirmed whether the jailbreak acts during update installation or if some other legacy vulnerability is involved. Whether the exploit applies to all modern iPhones or just the iPhone 18 Pro is also unresolved.
Apple now faces pressure to investigate and patch this bypass. Users relying on Lockdown Mode for protection should be cautious about opening unsolicited PDFs, even in a heightened security posture.
What this means: Lockdown Mode remains a valuable security envelope—but it’s not infallible. This jailbreak reminder that threats evolve, even against defenses designed for high-risk users. The key will be how quickly Apple closes the loophole and whether further exploits sharpen focus on document-based attack vectors. Watch for whether upcoming security updates explicitly address this bypass, and whether Apple provides more transparency about Lockdown Mode’s limits.