Oracle PeopleSoft systems are under renewed attack as threat actors find ways to bypass Web Application Firewalls (WAFs) and exploit a critical vulnerability, known as CVE-2026-35273. With a CVSS score of 9.8, this flaw allows unauthenticated remote code execution and has been actively weaponized by a group linked to ShinyHunters, in a campaign targeting organizations globally.
The vulnerability was first exploited as a zero-day in attacks directed at academic institutions. Attackers performed reconnaissance, deployed remote access software such as MeshCentral, moved laterally through SSH using known credentials, and extracted data. Over 100 organizations, primarily in the U.S., were alerted by security firm Mandiant after their systems were identified as vulnerable.
How WAFs Are Being Outwitted
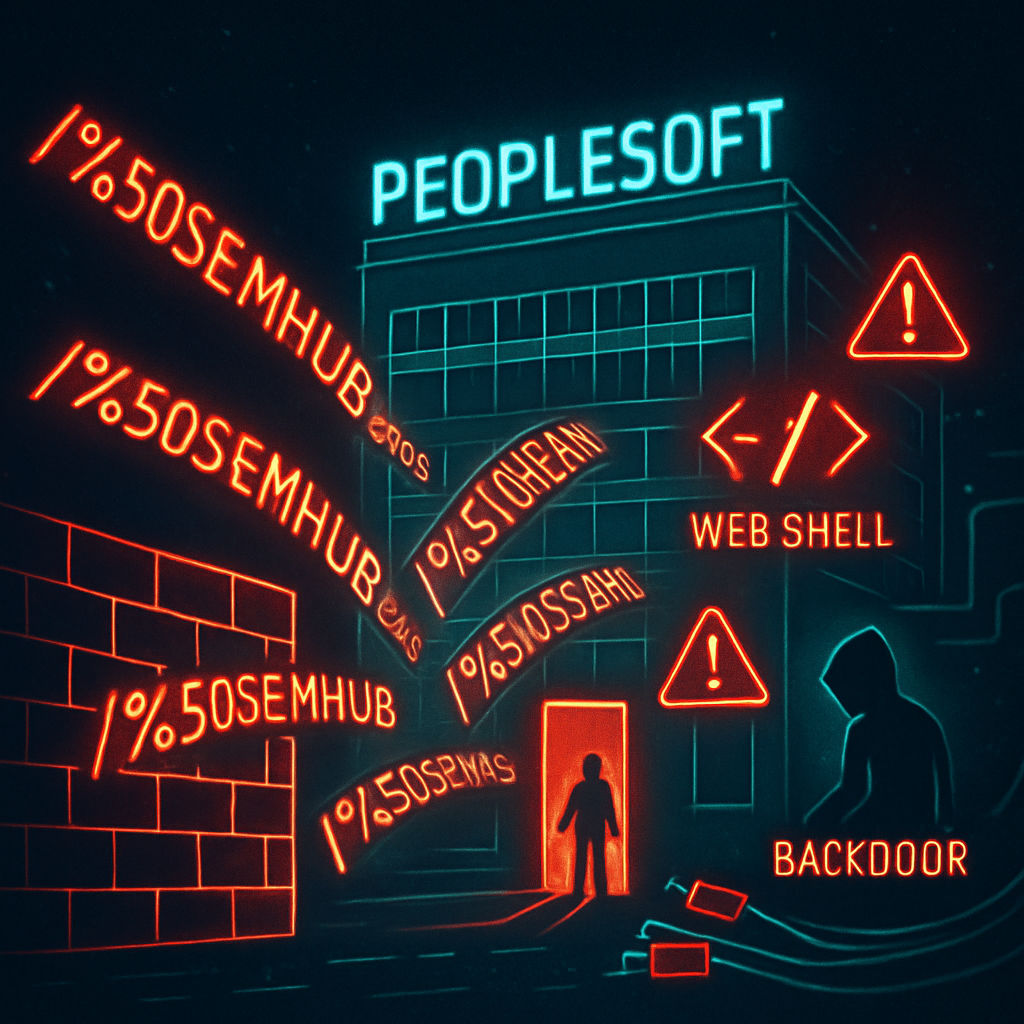
The attackers—tied to UNC6240—have modified their exploit to sidestep WAF rules that block access to a specific vulnerable endpoint: PSEMHUB under PeopleSoft’s Environment Management Hub (EMHub). They are using URL-encoding of a single character (“P” replaced with “%50”) in the request path (/\%50SEMHUB/) to evade detection. WAFs typically match literal strings before decoding, while the backend server correctly decodes and routes the request to the vulnerable servlet.
Full Attack Chain & Payload Details
The attack unfolds in several stages:
- Sending POST requests to
/\%50SEMHUB/hubwith a serialized Java object. - Abusing Java deserialization in the PSEMHUB hub servlet to execute code without dropping files (“fileless”).
- Installing two JSP web shells in the
PSEMHUB.wardirectory:x.jspfor cross-platform commands, andu.jspto upload files in chunks (including executables) and execute system commands. - With
u.jsp, a signed installer namedPle64.exe(trojanized) is uploaded. This loadsSIDEEYE, a C++ backdoor that communicates with a remote server. It enables credential theft, file/process management, reverse shell functionality, and acts as a reverse proxy. - On Linux systems, persistence is achieved through open-source tunneling tools (Neo-reGeorg) and remote monitoring/management tools like MeshAgent.
Damage and Scope
The campaign has victimized entities in higher education, healthcare, technology, agriculture, transportation, and government sectors. Web shells have been deployed on dozens of systems. Approximately 25% of commands are run with root or NT AUTHORITY\SYSTEM privileges, offering full system control; the remainder run under limited PeopleSoft or WebLogic service accounts.
Mitigation & Incident Response Steps
To defend against these attacks, organizations are urged to take the following actions:
- Apply the patch for CVE-2026-35273 immediately.
- In multi-server setups, disable the EMHub service; for single-server configurations, remove the
PSEMHUBapplication entirely. - Search WebLogic access logs for requests to
/PSEMHUB/and any percent-encoded versions. - Inspect the
PSEMHUB.wardirectory for JSP web shells likex.jspandu.jsp. - Rotate credentials that are accessible to the PeopleSoft application service account.
- Look for large archive files in temporary or web-accessible directories on PeopleSoft or database hosts.
- Review audit logs in databases for bulk data queries or exports involving HR, payroll, or student records.
- Monitor outbound traffic from PeopleSoft hosts for suspicious connections.
The attackers are expected to steal data and threaten to release it unless ransom demands are met. Organizations should be on guard for extortion attempts and make contingency plans for potential public exposure of stolen information.
This alert arrives just after ShinyHunters reportedly breached the U.S. FBIJobs.gov portal, stealing 2-3 TB of data. The group claims this breach used a different Oracle PeopleSoft zero-day bug not related to CVE-2026-35273.
Why this matters: despite widespread adoption of WAFs as a frontline defense, this attack shows simple bypass techniques—like encoding a single character—can defeat string-based rules. For enterprises relying on PeopleSoft, WebLogic, or similar enterprise apps, this is a stark reminder that patching, service hardening, and careful inspection of both logs and applications are essential. Beyond this specific bug, we will be watching how fast organizations respond, how broadly this campaign spreads, and whether similar evasion tactics emerge elsewhere.