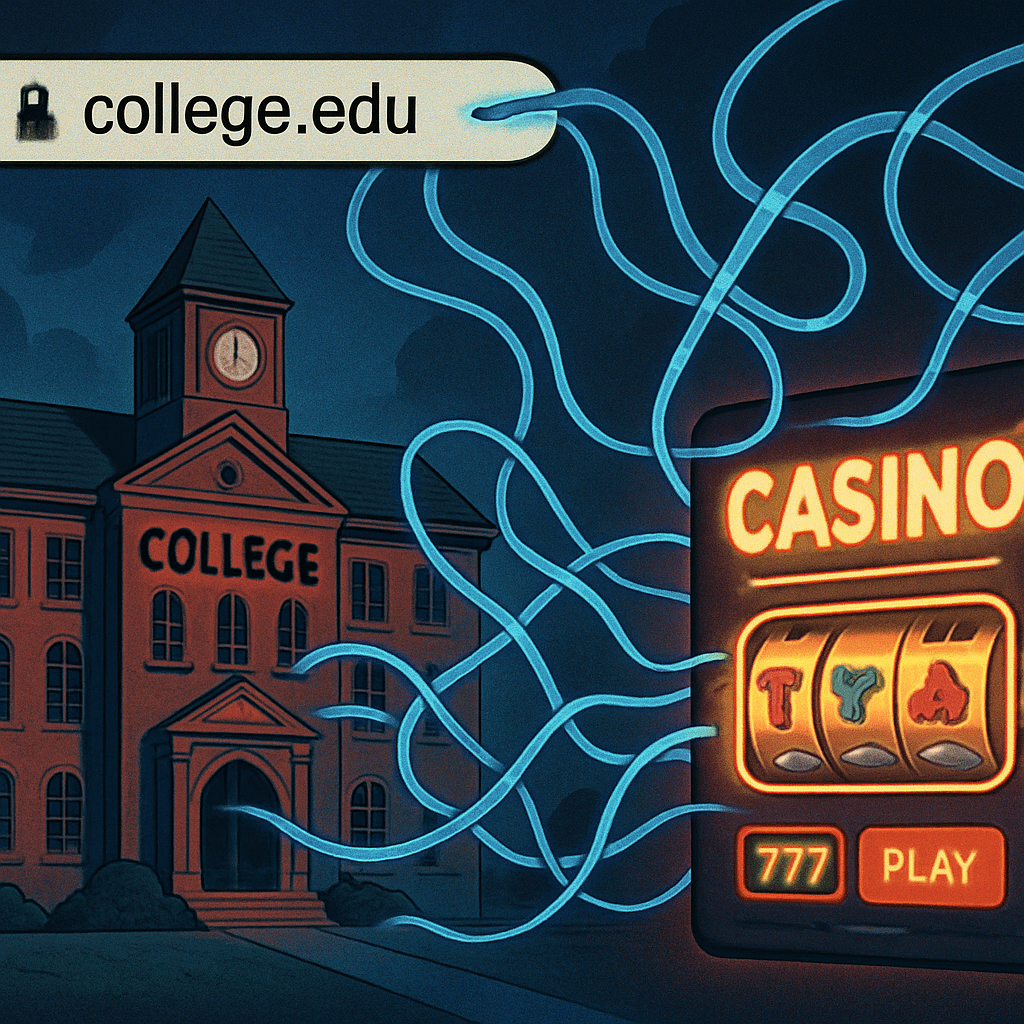
Researchers uncovered a scheme where attackers compromised a Thai college’s website—km.chpc.ac.th—and used it to hijack Google search traffic in order to redirect users to an illegal online casino. The site sits in the country’s .ac.th domain zone, which is reserved for educational institutions, making the breach especially concerning for institutional trust.
The anti-fraud platform ADEX discovered that a deceptively innocent page themed around gambling was injected into the college site. Google indexed this page, ranking it at the top for a targeted query. When users clicked the result, they were redirected—not to the educational site—but to an online casino, a product whose advertising is strictly prohibited in Thailand.
Not Traditional Cloaking—Domain Borrowing Strategy
What makes the attack unusual is that it bypassed traditional cloaking. No scripts altered content based on visitor type; instead, the scheme leaned entirely on the infrastructure being fully legitimate—Google’s search results, the college site, and the ad’s redirect chain were all “clean” at face value.
To an automated crawler or ad moderator, everything appeared fine. The users saw the college’s site, but a single click off that site led them to a casino. ADEX noted that the violation actually occurred outside the advertiser’s infrastructure—embedded in the redirect chain.
A Broader Pattern of Abuse in Trusted Domains
This instance is one of many. In Thailand, government agencies have logged about 30 million URLs tied to gambling content across nearly 1,000 public-sector domains; one health ministry alone has found some 8 million injected scripts. In Indonesia, more than 600 government and educational sites are blocked for hosting gambling content, especially inside .ac.id and .go.id zones. A 2025 academic crawl revealed dozens of Indonesian schools with breached sites loaded with gambling-themed pages. Researchers globally report hundreds of educational and public-sector domains being quietly injected with gambling and adult content—often designed to evade human detection but visible to search engines.
The root appears to be underinvestment in cybersecurity at many public institutions, which often lack strong defenses against domain hijacking, script injection, or the oversight needed to catch such abuses early.
Policy Gaps and Suggested Defenses
Google enacted “site reputation abuse” rules in 2024 to curtail misuse of trusted domains. However, the policies are aimed largely at owners who knowingly rent out their domain reputation, rather than at sites quietly hijacked by attackers. Cases like the Thai college being exploited fall into the gap: attackers don’t tamper with visible content until after search crawler indexing, making detection harder.
ADEX urges that advertisers and ad networks treat redirects involving restricted top-level domains (such as .ac, .gov, .edu) not as benign by default but as red flags during vetting. They also recommend post-approval checks of ad campaigns, inventorying old subdomains, and simulating attacker behavior when auditing trusted domains.
Institutions are advised to scan their domain zones proactively for injected pages, maintain awareness of all subdomains, and ensure that certificates or “clean” appearance alone aren’t taken as proof of safety. The fraud detection firm emphasizes that malicious activity can hide behind ordinary, legitimate infrastructure—including fully valid TLS certificates.
Why this matters: the case blurs the line between legitimate infrastructure and abuse. When educational or governmental domains are abused in this way, the public loses trust not just in a site, but in the systems that should protect it. As attackers shift from overtly malicious content toward stealthier redirect-based attacks, vigilance must shift likewise. Ad networks, domain administrators, and policy makers will need to adapt tools, enforcement, and auditing practices to cover this emerging threat.