Autonomous AI agents, believed to be tied to Chinese threat actors, uncovered a zero-day vulnerability in MONAI Label—an open-source server used for labeling medical scans—and used it to gain root access to at least one university server, according to Amazon Threat Intelligence.
What the Vulnerability Entails
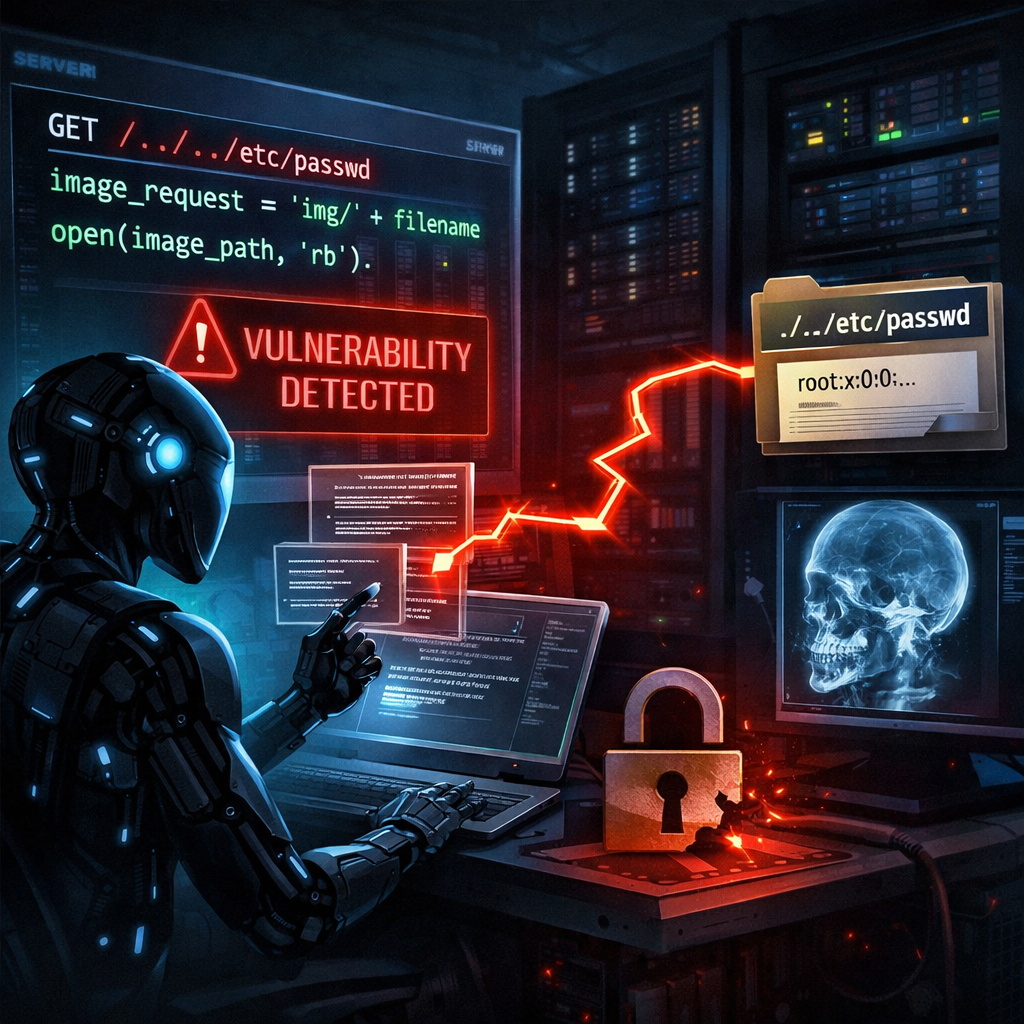
The flaw resides in versions 0.8.5 and earlier of MONAI Label when operated in its default state (without login enabled). A path-traversal security hole allows an unauthenticated attacker to write files outside the intended storage folder. Since the server runs with the privileges of its service account, a writable code or configuration directory lets the attacker execute arbitrary code.
MONAI Label is distinct from the broader MONAI framework and serves specifically for tagging medical scans to help train imaging models. The combination of default authentication being off and the server’s file write behavior made it ripe for exploitation.
How the AI Agents Worked
Investigators found that the operators used an open-source framework called Cairn, designed to run AI agents as automated penetration testers. A control panel for Cairn was exposed without a password, exposing task settings, prompts, and execution logs.
In September, over a roughly 48-hour span, these agents scanned MONAI Label’s interface and landed on the path‐traversal exploit within about 11 minutes. The goal set for them was to gain shell access. Later, they planted a malicious Python file set to execute at startup, triggering a process that loaded the file and connected back to the attacker as root, fully compromising one server.
Evidence Pointing to China-Linked Actors
Amazon’s analysis estimates a China-linked origin with moderate confidence. Clues included use of Simplified Chinese prompts, timestamps aligned with China Standard Time, and targeting of institutions likely relevant to Chinese interests. However, no specific group or government has been definitively linked.
Response and Mitigation
Maintain ers merged a source-code patch on October 19 that addresses the issue: the fix ensures uploaded file paths stay inside the approved storage fold ers and disallows empty or dot-prefixed names. Despite this, there is no official release including the fix yet; the latest version on package repositories remains 0.8.5, dating back to 2024.
The vulnerability has been assigned CVE-2026-133968 and rated critical with a 9.8/10 score. The published security advisory confirms the absence of a patched version for users to install.
What Organizations Should Do Now
- Restrict network access to MONAI Label servers, not simply by obscure URLs but via firewall or routing rules.
- Enable authentication, as it is disabled by default.
- Run the server under a least-privilege account rather than root, and limit writable directories.
- Ensure any build from source includes the October fix before considering it safe.
- For systems that were exposed, audit for unexpected Python startup files or unusual training jobs—signatures of this exploit path.
Amazon’s reconstruction doesn’t show that clinical patient data was accessed, that systems of care were breached, or that other MONAI Label deployments were necessarily compromised to the same extent. The root access achieved in the incident came from very particular conditions and account privileges.
This marks one of the first publicly detailed attacks where autonomous AI agents identified and exploited a privilege escalation zero-day entirely on their own. With tools like Cairn, operators can issue goals and let agents chart their own attack paths.
In a broader sense, this incident underlines the urgency of securing AI in cybersecurity: vulnerabilities in ML infrastructures, default configurations that encourage risk, and the emergence of AI agents acting as automated adversaries. Until fix releases are widely adopted, organizations using MONAI Label need to take defensive steps now—because it’s not a hypothetical threat anymore.