The Apache Software Foundation has revealed a serious vulnerability in Apache Tomcat that can allow remote adversaries to join trusted server clusters without having to authenticate themselves. Labeled CVE-2026-133325, this flaw specifically affects Tomcat clusters configured with TLS 1.3 and a pre-shared key setup. The advisory was released on November 19, 2026, crediting security researcher Mike Read for identifying the issue.
Which Versions Are Affected & What’s Being Fixed
Tomcat versions impacted include 11.0.28 and 11.0.29, along with 10.1.62 and 9.0.124. These releases are vulnerable only under specific cluster encryption settings—servers must be using TLS 1.3 with a pre-shared key. Public-facing Tomcat instances may not be exposed unless the cluster communication service is reachable externally.
Patch versions are in progress: 11.0.30, 10.1.63, and 9.0.125 will resolve the issue once released. Until then, administrators are urged not to assume safety merely because they’re on an affected version.
How the Flaw Works
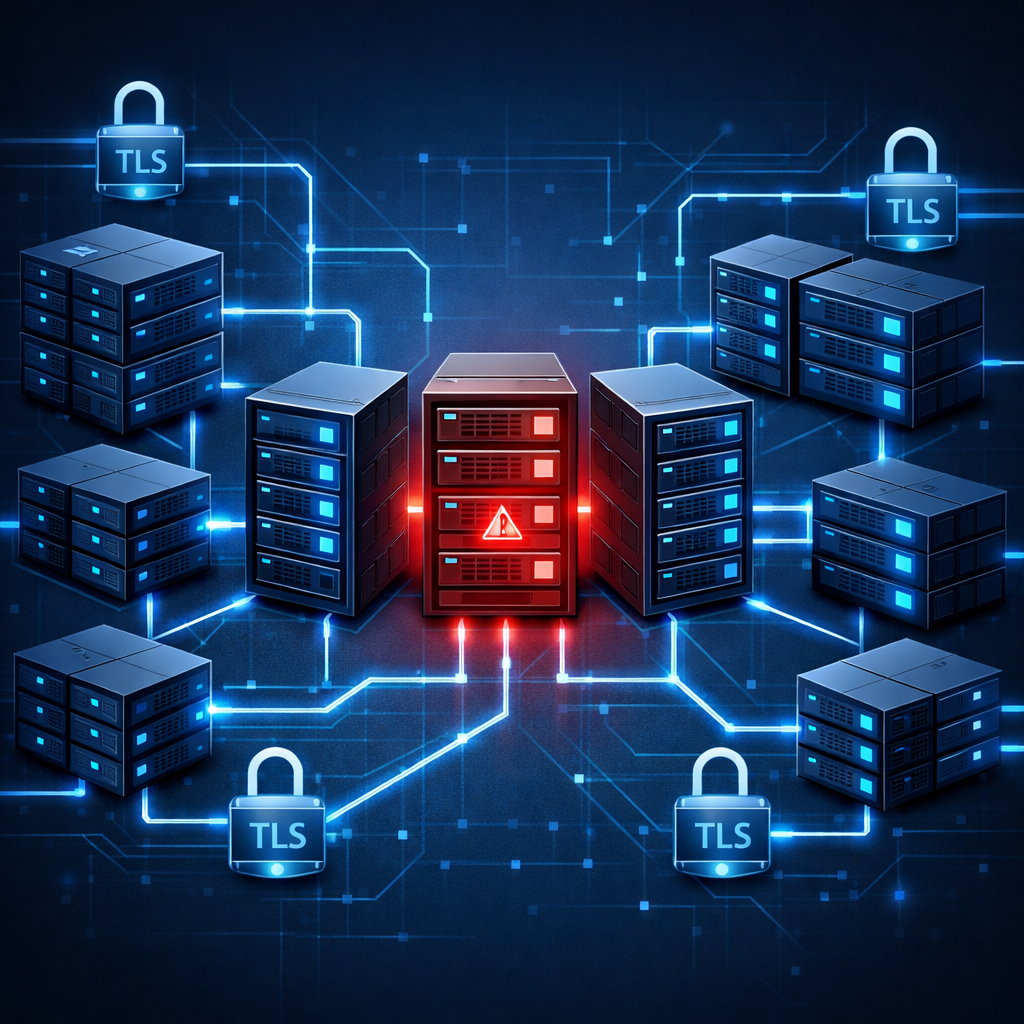
Tomcat’s clustering relies on Apache Tribes to let multiple server instances share session data. With this flaw, the system’s implementation of TLS 1.3 with pre-shared key fails to verify the identity of a connecting server. In short, a remote system could present valid pre-shared key credentials without any proof of being a legitimate cluster member, and Tomcat would accept it.
It’s important to highlight what this exploit does not do: there’s no current evidence of it being used in the wild, nor does joining a cluster automatically grant the capability to execute remote code. The risk centers on unauthorized cluster access.
What Measures You Should Take Now
Apache recommends downgrading cluster communication to TLS 1.2 while still using pre-shared keys as an interim defense. This change only impacts server-to-server cluster traffic, not client-to-server HTTPS connections.
Additional precautions include verifying the Tomcat version and cluster configuration on each node, locking down cluster-related ports so only trusted hosts can connect, and scrutinizing logs for any unexpected additions to cluster membership. After applying fixes or workarounds, ensure that all legitimate cluster members reconnect properly and that session replication is functioning as intended—sites may still reply to requests even if cross-server session sharing is disrupted.
Note: this vulnerability is separate from an earlier Tomcat issue tracked as CVE-2026-34486. That older flaw has been exploited; CVE-2026-133325 has not been linked to active attacks.
Why this matters: Server clusters are often used to distribute load and ensure resilience. A configuration flaw that lets attackers sneak into a cluster undetected undermines one of the core security assumptions—trust between cluster members. Any breach of that trust can open pathways to data leakage, takeover of session persistence, or broader internal reconnaissance.
What to watch for: When the patched versions (11.0.30, 10.1.63, 9.0.125) are released and verified, plan to upgrade immediately. Also monitor threat intelligence feeds for signs that attackers may be attempting to leverage this vulnerability. For now, TLS 1.2 fallbacks, proper network segmentation, and audit logging are your best defenses.