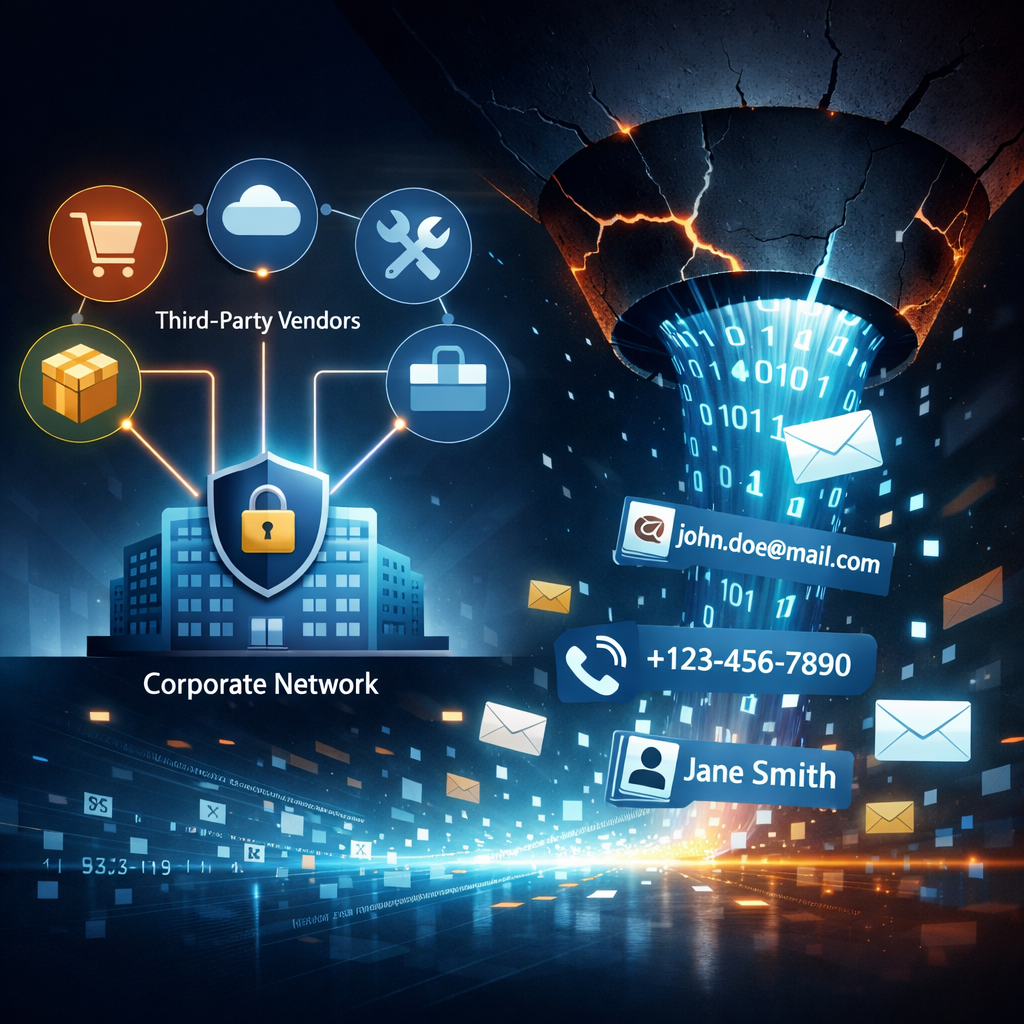
On November 19, 2026, customer data tied to Visa, Mastercard, and JPMorgan Chase was leaked after cyberattacks on third-party service providers—not from breaches of their own systems. Each company says its core networks remain intact, but important personal data and marketing information have been exposed.
What Was Affected and How
Visa confirmed that a vendor based in the Asia-Pacific region was involved, though no card numbers were impacted. Instead, records linked to marketing and contact details—such as email addresses and phone numbers—were among the data published. Mastercard similarly reported exposure of email addresses of certain cardholders in a benefits program, stressing that its payment network continues to function normally.
JPMorgan Chase said marketing data—including customer names and email addresses—were accessed in the breach. Some leaked records also revealed phone numbers and postal codes. JPMorgan plans to notify affected individuals and provide free credit monitoring where appropriate.
Scale & Risk
An initial analysis found over 16,000 email addresses connected to JPMorgan, along with sensitive location data. Visa’s files reportedly also contained thousands of email addresses and marketing campaign details in the Asia-Pacific market. It’s not yet clear if a single vendor serves all three companies or whether multiple vendors were compromised.
The hacker group n0n claimed responsibility for the leak, posting files associated with the three financial firms. None of the companies disclosed how access was gained or whether vendor systems were encrypted by the attackers.
Because details such as email, postal code, and benefit plan information can enhance phishing attacks, customers are advised to remain vigilant. Suspicious emails should be verified through official bank channels—not via embedded links. JPMorgan specifically asks customers to forward potential phishing messages to a designated email address and to report any fraudulent transactions immediately.
Visa emphasized that card usage and transaction systems were unaffected. Mastercard said the situation has been contained and it is collaborating with its service provider to assist affected cardholders. The company didn’t offer a total count of those impacted.
Financial institutions routinely engage third-party partners for everything from marketing to benefits administration. Breaches like this expose the risk inherent in such relationships: strong internal security isn’t enough if vendors are weak links. These events should prompt a renewed scrutiny of vendor management, data access controls, and transparency. What’s next: ongoing investigations need to clarify how widespread the impact is, which vendors are involved, and whether similar exposures are happening elsewhere.