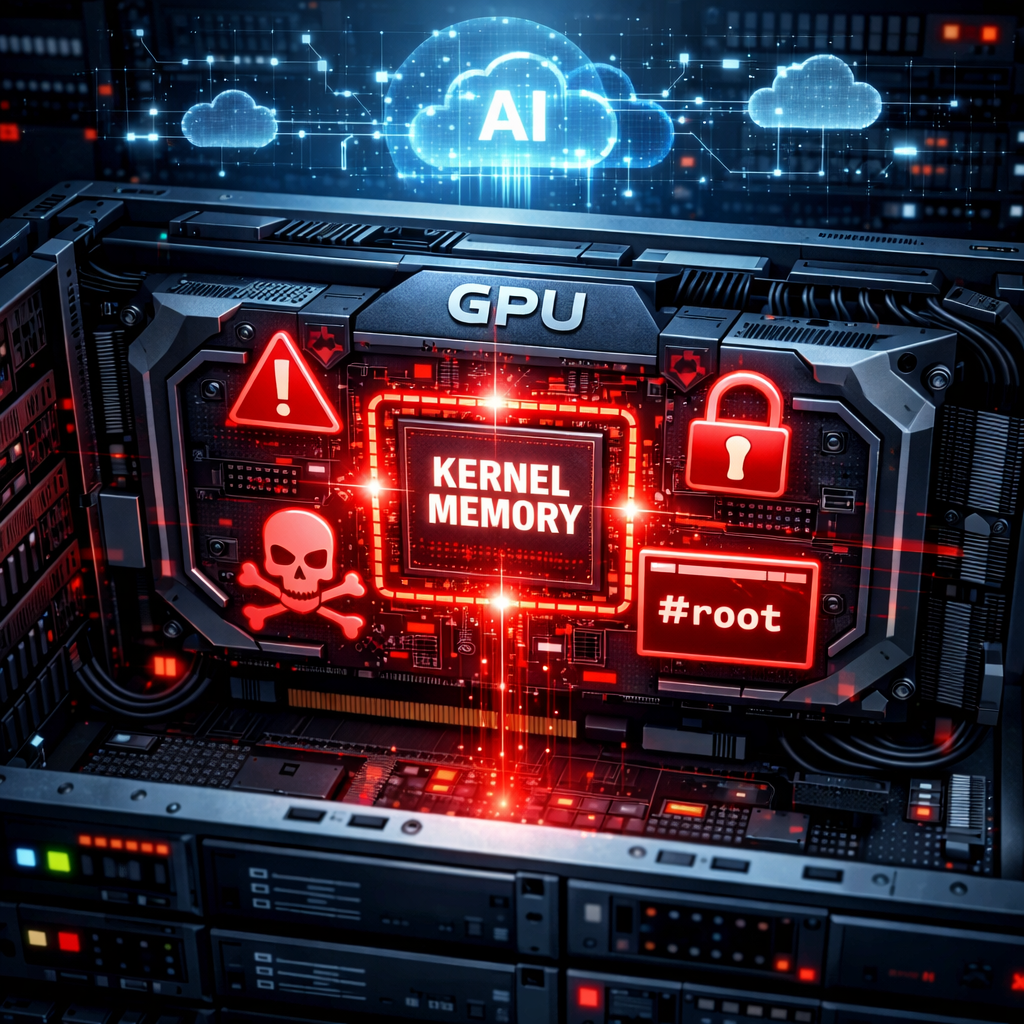
NVIDIA recently patched a deep-seated Linux GPU driver vulnerability that could let unprivileged users take full control of shared server hosts. Dubbed ForgePtr and tracked as CVE-2026-47501, the flaw enables root access even when attackers are confined to unprivileged containers, posing a serious risk for AI training and inference workloads on shared GPU infrastructure.
What Went Wrong
The flaw was introduced in May 2022 in version 515.43.04, the initial public release of NVIDIA’s open kernel modules. Security researchers from Stealthium found the issue persisted unaddressed through versions up to 610.57.04, confirming the vulnerability could be exploited in version 610.43.02 to achieve host root privileges. NVIDIA released a fix in driver version 615.71.09 on September 9, 2026, but only disclosed the vulnerability publicly on September 30. Stealthium’s detailed report went live on November 12, though they did not provide proof-of-concept exploit code.
The root cause lies in a missing error check during event buffer setup. When the driver tries to convert a supplied reference into a memory address and fails, it fails to halt execution. This oversight allows an out-of-bounds write, enabling arbitrary alterations to kernel memory. To complete the attack, researchers leveraged a separate vulnerability to locate live kernel addresses. Crucially, no administrator privileges or special container permissions were required—just local access to the vulnerable GPU driver.
Why Shared GPU Hosts Are in Peril
Shared GPU servers are often used in cloud or AI infrastructure, where multiple tenants run workloads in containers without full trust. ForgePtr turns even limited access into full host control, exposing every tenant’s model weights, data, and credential secrets. Tests additionally showed that Secure Boot didn’t defend these systems: researchers loaded an unsigned module, bypassed signature enforcement by altering the running kernel’s security state, and triggered host-wide changes—all without compromising the signed boot chain.
For Linux display driver users, upgrading to version 615.71.09—or later—is essential. Those operating NVIDIA’s virtual GPU (vGPU) products need to consult the specific advisory for their branch, since display driver updates may not cover all affected components. Until patches are applied, it’s strongly recommended that operators deny GPU access to untrusted containers or tenants, as container configuration settings alone won’t block exploitation. Teams should also monitor for signs of compromise, such as unexpected kernel module activity, changes to crash or lockdown defenses, or other host modifications tied to container workloads.
Unlike past container escapes or vulnerabilities in container management tools, ForgePtr stems from within the driver itself—meaning that updating container runtimes won’t fix the underlying danger. Despite NVIDIA assigning the flaw a 7.8 out of 10 severity rating, security experts suggest treating it as critical in contexts where shared access is standard.
What this means for GPU infrastructure: the ForgePtr flaw reveals just how fragile shared-resource environments can be when deep kernel-level bugs go undetected for years. Infrastructure providers should prioritize driver updates, tighten tenant isolation, and enhance runtime detection of low-and-slow compromise attempts. For end users and organizations reliant on GPU servers—think AI startups, labs, cloud tenants—this is yet another wake-up call. Watch for kernel memory alterations, module signature violations, and other host anomalies. The true measure of security here isn’t just patched software, but robust processes that guard against threats buried deep in driver code.