AMD’s SEV-SNP, designed to keep virtual machines’ (VMs) memory encrypted and shielded from the host hypervisor, has been bypassed in a newly disclosed attack dubbed “Mior.” Researchers report this exploit allows a malicious host, armed with specific privileges and a GPU, to read and even modify guest VM memory while also forging measurements used to verify VM integrity. The vulnerability has been assigned CVE-2026-0462 and carries a moderate severity rating (CVSS 5.9).
How SEV-SNP Is Supposed to Work—and Where It Failed
Secure Encrypted Virtualization with Secure Nested Paging (SEV-SNP) is AMD’s strongest virtualization security mode. It encrypts VM memory and uses hardware-based checks to stop the hypervisor (which cloud providers manage) from accessing or tampering with it. SEV-SNP also supports attestation—or a proof that VM setup is legitimate before sensitive data is handled.
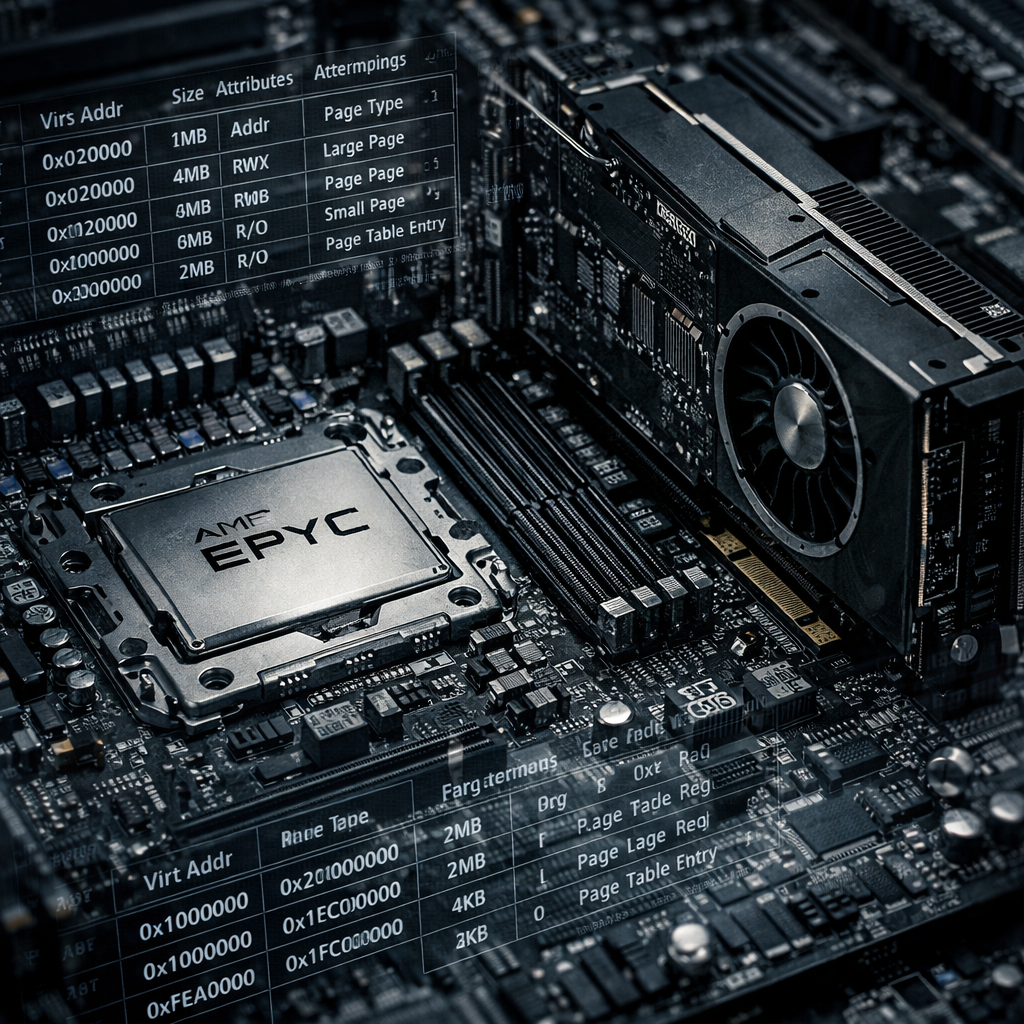
The “Mior” exploit doesn’t break the encryption itself or steal the cryptographic keys. Instead, it abuses a flaw in how the Reverse Map Table (RMP) is established. That table maps physical pages to their owners and enforces access rights. Researchers found that during setup, some writes intended for system memory were redirected into GPU memory, or mistaken for such, causing misconfigurations invisible to a key security component—the Platform Security Processor (PSP). This gap undermines the very checks that SEV-SNP depends on.
Attack Conditions and What It Enables
The Mior exploit requires pretty high privileges: access to the firmware, control over the hypervisor, and a PCIe device like a GPU. It was demonstrated on a Zen 5-based AMD EPYC 9135 server, with debugging disabled—that is, in a configuration similar to what you’d find in production. Once positioned, the attacker can not only read guest VM memory but also alter it. Even worse: the exploit can spoof attestation reports, disguising a modified VM as a clean and trusted launch.
It’s important to note this is not something a regular cloud tenant could pull off remotely. It’s an attack by someone who already controls the underlying host infrastructure—e.g. a rogue hypervisor or malicious firmware. But the implications are serious, especially for environments where strong isolation between host and guest is critical.
AMD’s Response and What Owners Should Do
AMD has acknowledged that SEV-SNP is affected (but not its older SEV or SEV-ES modes). The fix involves firmware updates, which AMD issued in a bulletin on November 10, 2026, covering several EPYC series processors: 7003, 8004, 8005, 9004, and 9005. Server manufacturers are expected to receive updated platform firmware by December 2026, while embedded EPYC models have target firmware release dates in 2027.
For defense, operators must verify their hardware has received the relevant BIOS/firmware update. Cloud customers should ask whether hosts running their workloads are patched, and check that attestation values match those published by AMD. Updating the guest operating system alone won’t help, since the vulnerability stems from flaws in host firmware.
Background: RMPocalypse and Other Related Issues
Mior builds on earlier vulnerabilities in the RMP mechanism, including a previous attack named “RMPocalypse” that highlighted how misconfigurations in RMP setup could be exploited. Another related issue, “BadRAM,” exposed how memory module information can be misinterpreted by AMD systems. Together, these findings underscore that both the path of memory writes and their interpretation by trusted firmware matter just as much as the access-control checks themselves.
What this means: SEV-SNP’s protections, while robust on paper, have weak points that sophisticated attackers can exploit. For organizations relying on AMD EPYC servers for isolation—especially in cloud or multi-tenant setups—this vulnerability potentially breaks a core trust assumption.
Watch for firmware rollout status in coming weeks. The real test will be whether cloud providers can apply patches fast and whether hosts can provide updated attestation to end users. Until then, SEV-SNP should be considered guardedly—the promise of hardware-based VM isolation remains strong, but the margin for error has narrowed.