After a seven-year hiatus, the Retadup USB worm is active again, now delivering CoffeeLoader malware to Windows machines. Though French authorities dismantled Retadup’s botnet in 2019, its infrastructure began creeping back into operation in 2024. New findings outline how attackers revived old command domains and are using them to spread sophisticated malware via infected removable drives. The identity of those behind the resurgence remains unknown.
What’s Retadup & How It Spreads
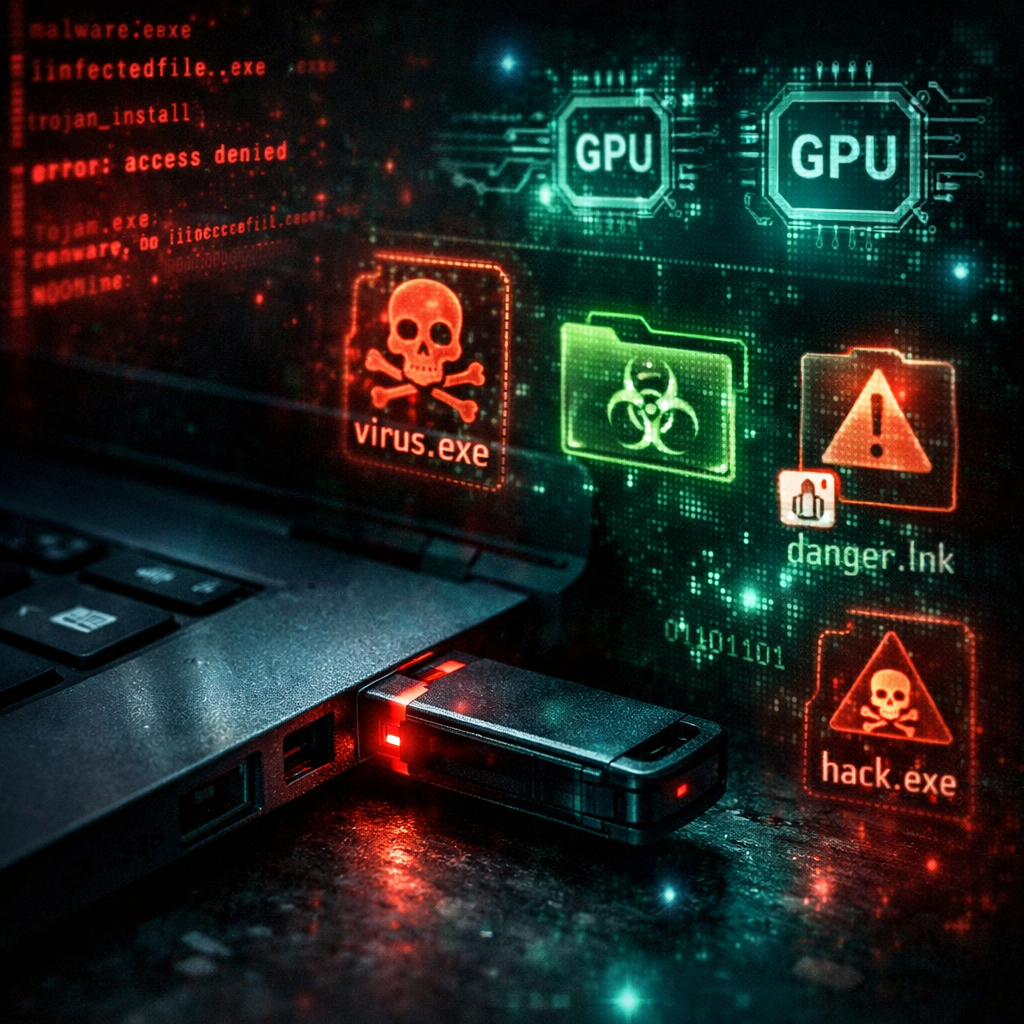
Retadup—originally discovered in 2017—uses AutoIt and AutoHotkey to copy itself onto USB sticks and external drives. It hides via system shortcuts and hidden files, waiting for someone to open a malicious shortcut on another computer to spread. The method relies on user interaction—just plugging in a device isn’t enough; a click triggers the infection.
In mid-2019, French law enforcement seized Retadup’s command and control (C2) servers. Infection-reports dropped sharply after systems under Retadup’s control received instructions to uninstall the worm. Over 850,000 devices were cleansed in a matter of weeks.
Revival, SmokeLoader & Shift to CoffeeLoader
Researchers monitoring network traffic have found that old C2 domains began to register activity again in 2024. These servers first delivered SmokeLoader, a malware loader, then shifted into distributing CoffeeLoader by early 2025. Analysts are unsure whether the original creators reactivated Retadup or a new group commandeered it. One variant from 2017 still connects successfully to these revived servers.
The new CoffeeLoader payloads pack upgraded tricks. They drop modified 7-Zip libraries laced with self-decrypting shellcode. For both decryption and execution, the malware abuses graphics interfaces. Earlier versions used OpenCL; the current iteration uses OpenGL. The malware also introduces an intermediate downloader that handles persistence (copying its library into AppData, registering startup entries), protects itself from being disabled via Task Manager, and injects into legitimate Windows processes. Once in place, it securely fetches, verifies, decrypts, and then executes its main body. The payload execution may happen via process injection, launching executables, or loading DLLs.
Impact & IoCs
Kaspersky mitigated about 15,000 Retadup infection attempts in the first three quarters of 2026. Most blocked incidents occurred in Peru, Angola, Russia and Bolivia. Note: these were attempted infections—not confirmed CoffeeLoader infections. Other malware using similar USB-shortcuts remain active globally, reinforcing the risk posed by removable media even today.
Key indicators of compromise include various former Retadup command-and-control (C2) domains—such as alphanoob[.]com, newblackage[.]com, roro2016.linkpc[.]net, among others—and new CoffeeLoader C2s like internet-speed-check[.]com. Files associated with installation have specific MD5 hashes listed for both DLLs and executables. Any detections matching these signatures call for immediate response in enterprise or personal security environments.
The return of Retadup shows how dormant threats can regain power when their infrastructure is reactivated. The shift to CoffeeLoader, with GPU-assisted decryption and new stealth techniques, means what once seemed neutralized now poses renewed danger. Organizations should monitor removable media behavior closely, reinforce endpoint defenses, and scrutinize any USB-driven operations.
What this resurgence means extends beyond just Retadup’s story. It demonstrates that takedown operations—while valuable—may not be sufficient unless domain ownership and control are maintained permanently. The blending of old code with fresh attack chains like CoffeeLoader elevates the stakes for cybersecurity teams. Looking ahead, defenders must assume that even legacy malware infrastructures can return with modern enhancements—and prepare with layered defenses, hardened endpoint controls, and active domain-monitoring.