SAP has released fixes for four critical vulnerabilities—each rated CVSS 10.0, the maximum score—as part of its November Security Patch Day. None of these flaws require any user interaction. They affect SAP NetWeaver’s application server and its Internet-facing components, and two of them allow remote code execution (RCE). These discrepancies pose a serious threat to business-critical SAP systems unless patched immediately.
What’s at stake?
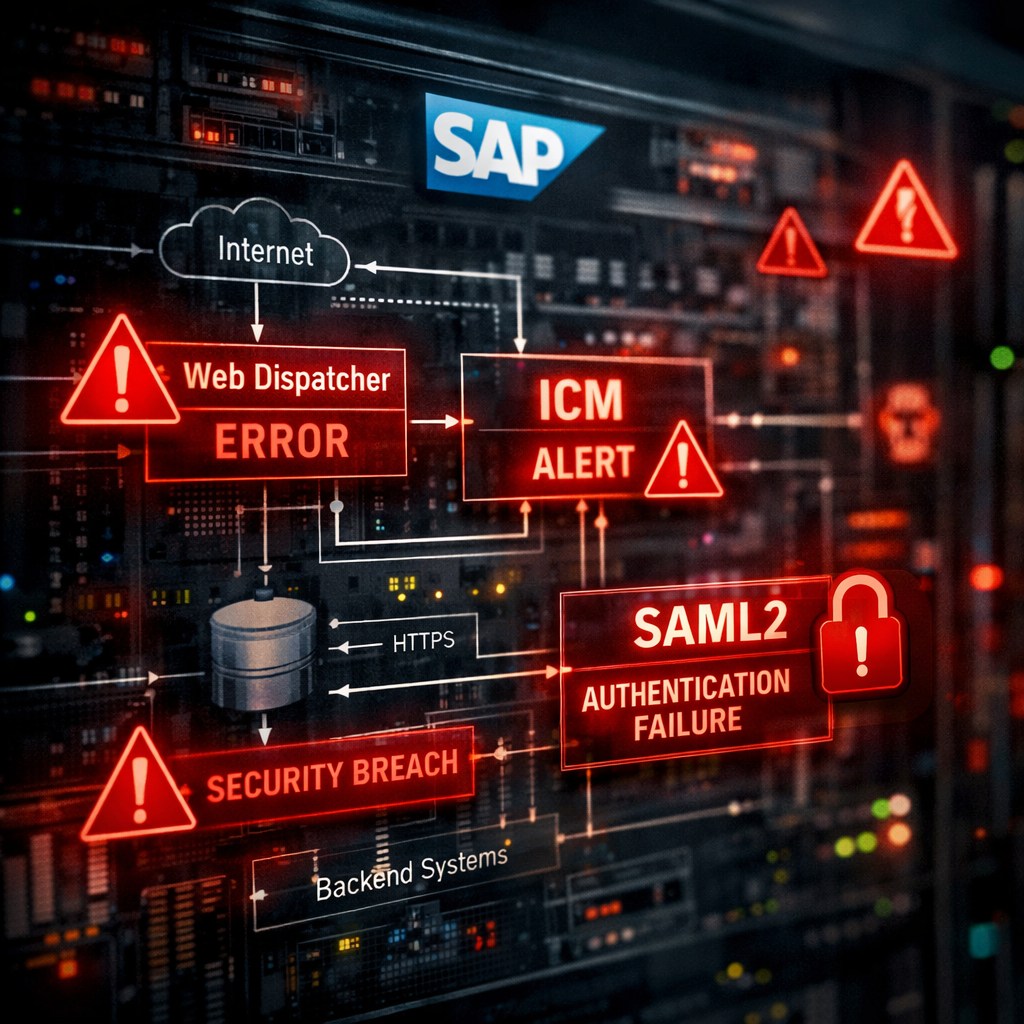
The vulnerabilities are spread across four components. Two of them reside in the Web Dispatcher and the Internet Communication Manager (ICM), both of which parse web traffic coming from external sources. Attackers who can reach these network-accessible components could deliver crafted input that corrupts memory and achieves arbitrary code execution without any authentication.
A third flaw involves the SAML2 service provider used in SAP NetWeaver AS ABAP. In environments where SAML single sign-on is deployed, this bug could let attackers impersonate users—including privileged ones—without valid authentication. The final issue is in the SAP Gateway: misuse of default access control lists can enable attackers to pretend to be internal components and issue commands or manipulate systems.
Affected versions & fixes
Each vulnerability is assigned its own CVE and addressed via individual SAP Notes. The affected versions vary by component:
- Internet Communication Manager (CVE-2026-76964): Multiple NetWeaver ABAP and Kernel versions (like 7.53, 7.54, 7.77, 7.93, 9.16-9.20) are impacted.
- Web Dispatcher (CVE-2026-89126): Includes both standalone and embedded Web Dispatchers, plus relevant Kernel and SAP HANA XS Classic and Advanced components.
- SAP Gateway (CVE-2026-89103): Affected are versions including Kernel 7.22, 7.53, and newer, across ABAP systems using Gateway functionality.
- SAML2 service provider (CVE-2026-120017): Systems using ABAP Platform and components like SAP_BASIS versions from 702 up to recent levels are vulnerable.
Mitigations & best practices
SAP has issued specific Notes for each issue, providing updated packages or support stack updates as fixes. For organizations using SAML2 single-sign-on with NetWeaver, there’s no workaround for signature-validation failures—updating is the only remedy. In Gateway environments, tightening or explicitly defining access control lists is essential; a parameter gw/acl_mode_proxy is introduced (for older kernels) to fix default leniency.
Temporary mitigations include disabling WebSockets where RCE exploits are possible—but that will disrupt features like Fiori Push Channels. Protecting the ICM by ensuring it isn’t directly exposed to the network (e.g. make it accessible only through Web Dispatcher) is another stopgap.
What organizations must do now
Security teams should treat all four patches as high priority and rollout updates across Kernel, Web Dispatcher, Gateway, and SAML2 components. Missing just one instance—such as a single Web Dispatcher—can leave the environment open. Teams must also audit their identity providers, SAML login logs—especially privileged-user logins—and ensure network boundaries prevent unauthorized component access.
These vulnerabilities are especially dangerous in enterprise environments using SAML-enabled ABAP systems, hybrid setups, or internet-exposed portals. The combination of remote code execution risk and fully bypassing authentication makes this among the more severe batches of SAP bugs in recent years.
Analysis: This patch release lays bare that even well-trusted enterprise platforms are brittle when internet-facing modules are involved. The ability to execute code without any user interaction or credential use ramps up risk exponentially. For defenders, it means there’s no more time for patch holidays—organizations must inventory every NetWeaver/ABAP system, validate boundary configurations, and deploy these fixes immediately. Long-term, this underscores the need for stricter default ACLs and more rigorous signing and validation in identity protocols like SAML.