Microsoft has rolled out a powerful safeguard in Edge to tackle websites that trick users into granting notification permissions, only to repeatedly send fake virus alerts. Starting with Edge version 156, the browser now cuts off these malicious sites at the source—blocking further notifications tied to scam pages detected by Microsoft Defender SmartScreen or the Scareware blocker. This prevents a common pattern where closing a deceptive page does nothing to stop the flash of dangerous alerts that flicker back through notifications users previously allowed.
How the Scam Works—and What Edge Does Differently
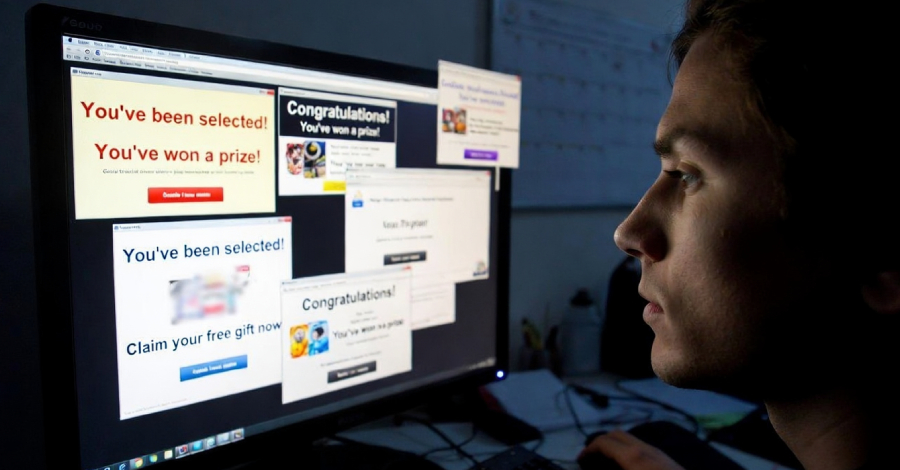
The scam begins when a website implores a visitor to click “Allow” on a browser prompt, often under the guise of proving they’re not a robot. Granting this permission gives the site a long-term channel to push alarming notifications, even when the original page is gone. These alerts often mimic antivirus software with urgent claims about malware, system failures, or security breaches—designed to scare users into unsafe action.
Edge’s response bridges detection tools and permission systems. When SmartScreen or Scareware blocker spots a scam reached via a site’s notification, Edge promptly disables notification access for that site—not just closing the scam page. On launching the browser, users will see an information bar explaining the block. There’s also a view in Settings where blocked sites are listed, with the option to restore notifications if a block was made in error.
Empowering Users to Take Action
Edge also now offers a “Block and report” button alongside notification permission requests. This allows users to block the site and send SmartScreen a report—complete with the URL and a screenshot—before even granting access. It gives Microsoft early insight into shady behavior.
For immediate threats, users can still interact with the notification menu: clicking the options beside “Block” lets them stop future prompts from the same site. Until automated detection steps in, this serves as the frontline defense. Edge warns that fake alerts may include controls that seem “official”—but are often traps leading to more pop-ups or scare tactics.
These changes reflect a shift in focus from managing individual instances of problematic pages to cutting off the vectors that allow repeated abuse. The browser makes suspicious activity a community concern—automated detection feeds from user reports and Microsoft’s cloud reputation grow smarter with every incident.
Deploying this protection is especially critical given campaigns like those using the CypherLoc browser locking kit, which combine full-screen disruptions, fake error messages, and alarming media to push users toward fake support calls. Edge’s new tools disrupt the ecosystem by snipping off the delivery path. Microsoft reports that tens of thousands of users avoid new scams daily through Scareware blocker, and each new report helps shield dozens of others during preview phases.
What to watch: how effective the auto-blocking measures are in real-world use, especially for edge cases where notifications are borderline or misleading. Also worth monitoring: whether malicious sites evolve new consent-bypassing methods, or if browser vendors like Google or Mozilla adopt similar protections. Edge version 156 is live now, so users should ensure they’re up to date and remain cautious before clicking “Allow” on any notification request.