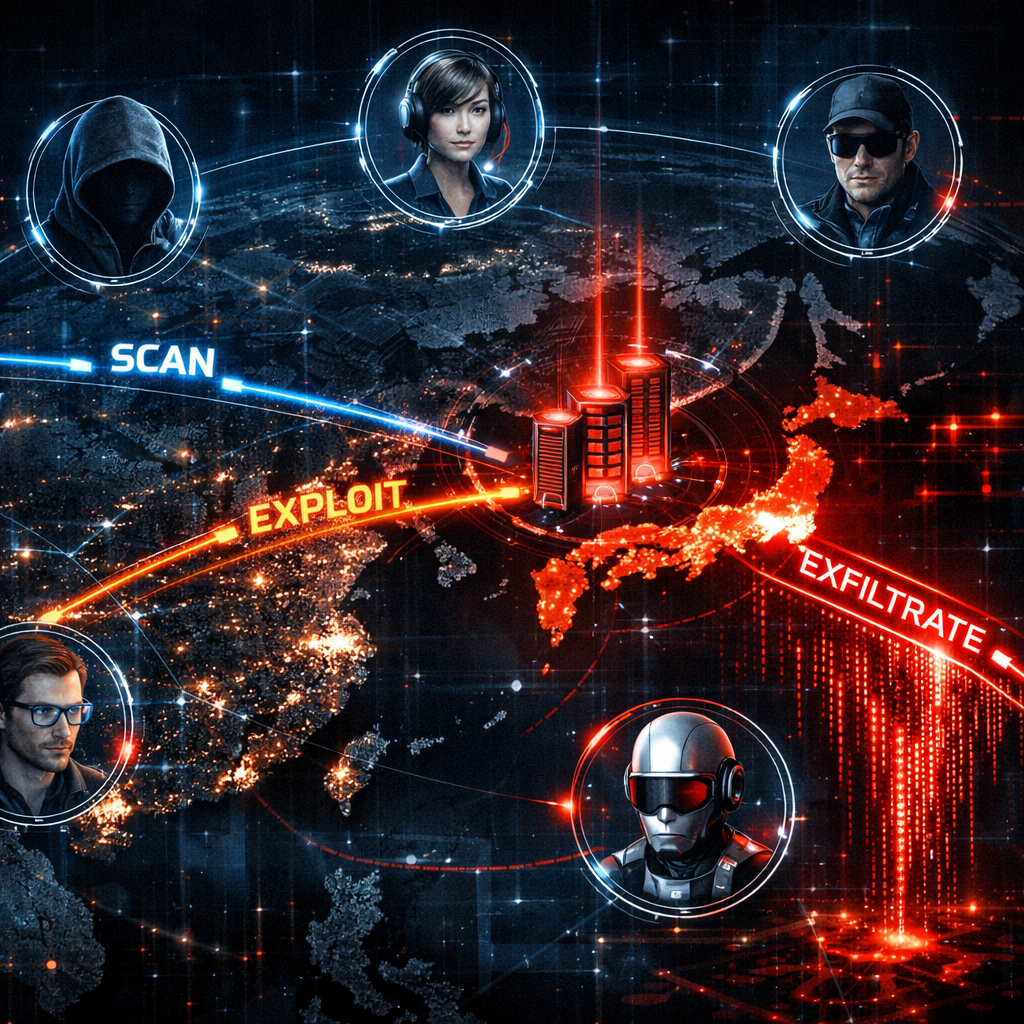
New intelligence reveals that threat actors have repurposed CyberStrikeAI, an open-source penetration testing platform, to orchestrate automated campaigns against multiple Japanese targets. Rather than manually executing every phase of an attack, adversaries deployed 44 specialized AI agents to scan for vulnerabilities, exploit systems, maintain persistence, steal data, and produce reports—all without first uncovering novel bugs. This approach elevates the automation of intrusion workflows to a new level.
Autonomous, Agent-Based Attack Chain
In mid-October 2026, attackers leveraged CyberStrikeAI to target at least 19 organizations—16 of them in Japan. For each target, agents within the platform carried out specific roles: some focused on reconnaissance, others on validating and exploiting vulnerabilities, credential gathering, or exfiltration. The system even created fake login interfaces and produced Japanese-language forms tailored to the victims. A central dashboard tracked the performance of each agent, reported success rates, token usage, and managed campaigns in batches, creating consistency across reports and evidence records.
This campaign differed from past incidents involving CyberStrikeAI, such as those attacking FortiGate devices. While those earlier cases displayed that the same tool was abused, the recent activity shows that automated AI coordination—not simply human-guided use of AI—was the driving force. The setup didn’t rely on new or zero-day vulnerabilities but instead exploited exposed interfaces on older systems, often without authentication protection.
Detection Challenges and Defensive Measures
Researchers pieced together the operation by examining publicly accessible logs, scripts, target lists, and command histories hosted on attacker-controlled servers. Though compromised data was recorded, deeper confirmation on which organizations suffered full breaches is limited due to absence of internal logs or forensic images—many targets saw evidence of reconnaissance without data exfiltration or web shells.
For defenders, traditional hardening strategies still apply: audit externally exposed applications, disable or patch legacy systems, eliminate open administrative portals, and avoid default credentials. Organizations should also monitor for low-volume, dispersed intrusion attempts which can evade detection when spread across many targets. VPN setups and AI service exposure, in particular, warrant heightened scrutiny based on weaknesses revealed in this investigation.
While the precise attribution of this campaign remains ambiguous—despite consistent use of Simplified Chinese in the infrastructure—there’s no clear proof tying it to state actors or a singular group. Importantly, no definitive links were found between this event and other AI-assisted operations. Evaluations instead underscore automated orchestration at scale as one of the defining threats emerging today.
Why this matters: The use of CyberStrikeAI in this way illustrates a fast-growing paradigm shift—tools intended for red teaming and vulnerability assessments are now being weaponized by malicious actors into fully autonomous campaign frameworks. Organizations and defenders must treat AI-enabled workflows as an emerging priority in threat modeling. Going forward, watch for further misuse of open-source or multi-agent platforms and increased innovation in evasion tactics built on coordination across autonomous agents.